Your account
Three small pages hold everything personal to you in Aegis: your profile, how you sign in — password, one-time codes, passkeys — and the AI notices you have acknowledged. This chapter walks all three, in plain words.
Everything else in Aegis is shared with your colleagues; these pages are yours alone. Each person sees and changes only their own settings here — an administrator cannot open your security or privacy pages, and you cannot browse anyone else's. Administrators do see the job title and phone number on your profile, and can correct your name and job title from Settings.
Who uses it
Everyone, whatever their role: Viewer, Contributor, Manager and Admin all get exactly the same pages, covering their own account only.
What's on this screen
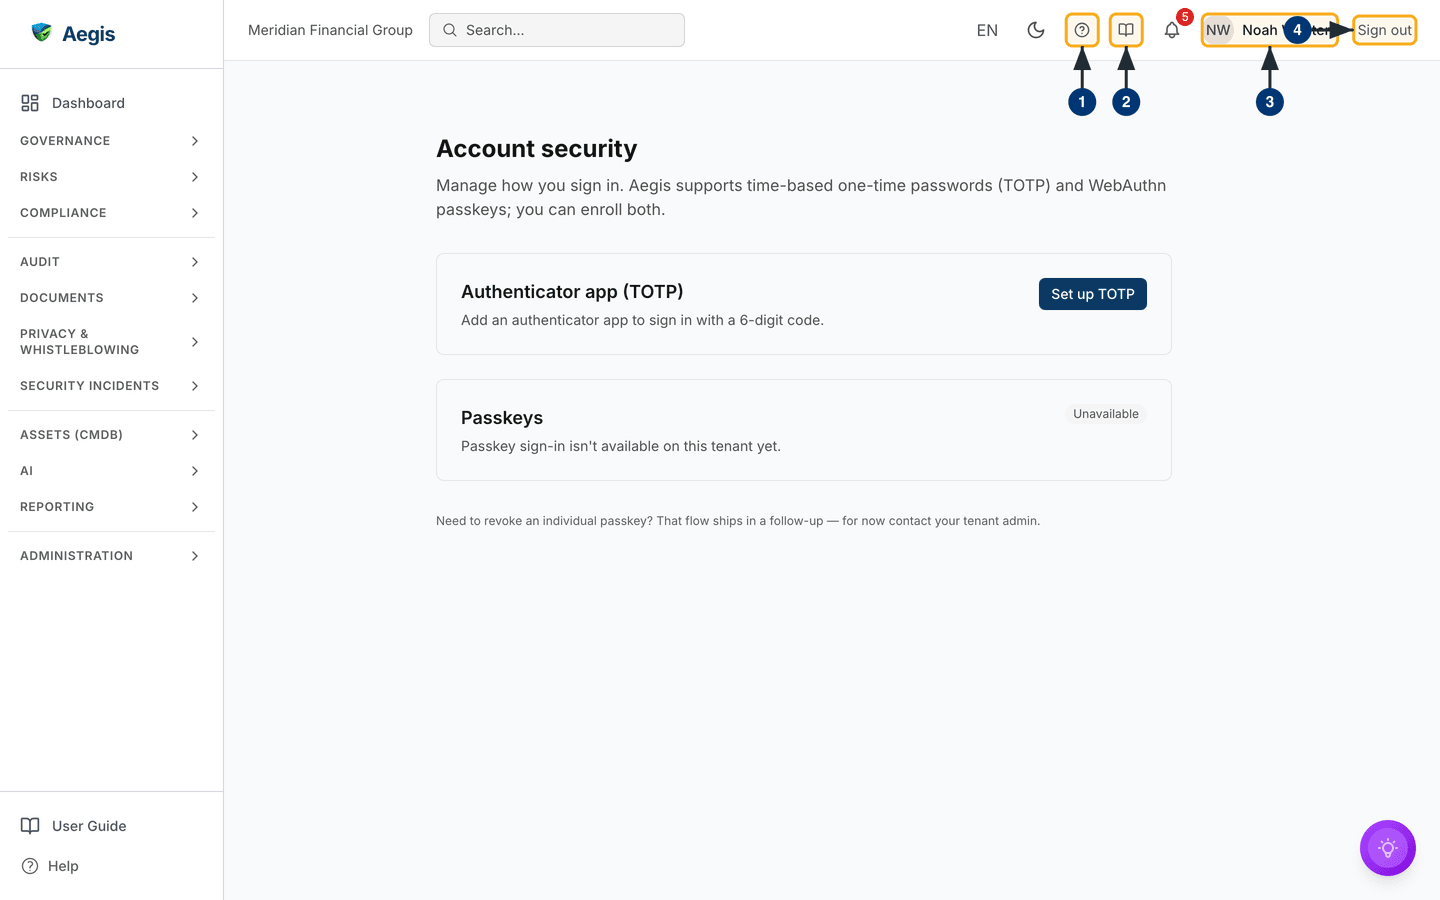
The Account security page (/account/security) is the
one you will visit most, so it is the one captured here. It sits inside the
normal Aegis frame:
-
The top bar shows your organisation's name and the
Search...box on the left. On the right, from left to right: the language picker (EN), the light/dark theme toggle, the help-panel button (a question mark), the User Guide button (an open book), the notification bell with its unread count, your initials and name, andSign out. -
The left menu starts with
Dashboard, lists the module groups (GOVERNANCE,RISKS,COMPLIANCEand so on) and ends withUser GuideandHelplinks at the foot. None of them leads to your account pages — the next section explains how to reach them. -
The page itself opens with the heading
Account securityand a line explaining that Aegis supports time-based one-time passwords (TOTP) and WebAuthn passkeys, and that you can enrol both. Below it are two cards. On the captured screen theAuthenticator app (TOTP)card offersSet up TOTP, because this user has not enrolled yet, and thePasskeyscard shows anUnavailablebadge, because passkeys are not switched on for that workspace. - A note at the foot of the page says that revoking an individual passkey is not yet possible here and that, for now, you contact your administrator.
How to get there
There is no entry for these pages in the left menu. Select your name or avatar
at the right of the top bar to open
Profile (/account/profile). Each of the three account
pages — Profile, Security, Privacy — carries the same account navigation at the
top, so from any of them you reach the other two with one click. You can also
reach Security through the amber banner on the
Dashboard that invites you to
Set up MFA, or when Aegis sends you there itself, when your
organisation requires a second factor for your role and you have not enrolled
one yet. The addresses are /account/profile,
/account/security for sign-in security, and
/account/privacy for the AI notices.
The top-bar controls you use around these pages, from left to right:
- Select the question-mark button. The help panel slides in from the side with help topics for the screen you are on and a search box.
-
Select the open-book button. The User Guide opens at the chapter for the
current screen: on
Account securitythat is Signing in; onProfileandPrivacyit is this chapter. -
Select your initials or name. The
Profilepage opens with your own details. -
Select
Sign out. Your session ends and you return to the sign-in screen. On a narrow phone screen this control shrinks to an icon.
The profile page: your name and contact details
The Profile page holds how your name and contact details appear in
Aegis. Your Email is shown greyed out: it is your sign-in identity
and cannot be changed here.
-
Select your name or avatar in the top bar. The
Profilepage opens withDisplay name,Job titleandPhone number. -
Change what you need. The display name is required and can be up to 70
characters, the job title up to 40, and the phone number up to 32 characters
with at most 15 digits, using digits, spaces and
+ ( ) - .. Clear the job title or phone number to remove it. -
Select
Save.Profile savedconfirms the change. If a value breaks one of the limits above, Aegis refuses it and tells you which rule it broke; nothing is saved.
The note under the fields says it plainly: your job title and phone number are visible only to you and to administrators.
If you sign in with single sign-on, or your account was created by the
directory connector, your organisation's identity provider owns your name.
The field is read-only with the hint
Managed by your organisation's directory, and each single
sign-on takes the name from the provider again, so ask your IT team to
change it there. Job title and phone number stay yours to edit.
The security page: your second factor
A password alone can be guessed or stolen. A
second factor (an extra proof of identity on
top of your password, such as a code from your phone) means a stolen password is
not enough to get in. The Account security page shows two cards —
one for each kind of second factor Aegis supports — each stating plainly whether
it is on.
-
The
Authenticator app (TOTP)card covers 6-digit codes. TOTP (a time-based one-time password — a code that changes every 30 seconds in an app such as Microsoft Authenticator or Google Authenticator) is the most widely supported option. If you have not enrolled, the card offersSet up TOTP; once enrolled it shows anEnabledbadge, the date it was switched on, and a control to disable it. -
The
Passkeyscard covers signing in with the fingerprint, face or PIN you already use to unlock your device — no code to type. When passkeys are switched on for your workspace the card offersAdd a passkey(orAdd anotheronce you have one), shows how many you have enrolled, and lists each one by its nickname — orUnnamed passkey— with its device type and date. When they are not, the card saysPasskey sign-in isn't available on this tenant yet.and shows anUnavailablebadge instead of a button that would lead nowhere. - Enrolment for either happens on its own page. For TOTP you confirm your password, scan a square code with your authenticator app, and type the 6-digit code it shows to prove the link works. For a passkey you follow your device's own prompt — the same gesture you use to unlock it — and can give the passkey a nickname such as "MacBook Touch ID".
A passkey is tied to one device; an authenticator app follows your phone. Having both means losing one device does not lock you out. The second-factor check applies when you sign in with email and password — single sign-on through your organisation's identity provider carries that provider's own protections instead.
Setting up an authenticator app
Selecting Set up TOTP opens
Set up two-factor authentication
(/account/security/2fa/enroll). The page reminds you that the code
is asked for when you sign in with email and password, and that single sign-on
and magic-link sign-ins are not challenged.
-
Type your current password under
Confirm your current passwordand selectContinue. A square QR code appears underAdd this account to your authenticator app, with a text link (theotpauthaddress) underneath for apps that cannot scan. -
Scan the code with your authenticator app, type the 6-digit code it shows,
and select
Verify and enable. The button stays inactive until all six digits are in. A wrong code givesThe code you entered did not match. Try again.; too many tries in a row ask you to wait a moment. -
Save your backup codesappears. The page says each backup code works exactly once if you lose your authenticator app, and the list is shown only this once. UseCopy codesand store them somewhere safe. -
Tick
I have securely saved my backup codesand selectDone—Donestays inactive until the box is ticked. Aegis confirms that two-factor authentication is now enabled. If Aegis had sent you here because your role requires it, you go straight on to the page you were trying to open.
Adding a passkey
When passkeys are available, Add a passkey opens
Add a passkey to your account. Each device gets its own passkey,
and you can enrol several.
-
Optionally type a
Device nickname, such as "MacBook Touch ID" or "YubiKey 5C", so you can tell your passkeys apart later. -
Select
Enroll passkey. The page saysFollow your authenticator prompt…while your device asks for your fingerprint, face, PIN or security key. -
When it completes,
Passkey enrolled. You can use it the next time you sign in.appears and the passkey is listed on the security page. If the device prompt is cancelled or the device does not support passkeys, the page says enrolment did not complete and you can try again.
When your organisation asks for a second factor
Your administrator can encourage or require a second factor:
-
Encouraged. While you have no authenticator app enrolled, the
Dashboard shows the amber banner
Add a second factor to your accountwithSet up MFAandRemind me later.Remind me laterhides it for a while; it comes back if you still have not enrolled. -
Required for your role. If you sign in with a password and have not
enrolled, every Aegis page sends you to the authenticator-app set-up until
you finish it.
Sign outkeeps working, so you are never stuck. Accounts that sign in only through single sign-on are not redirected — they have no Aegis password to confirm.
Turning two-factor off
-
With TOTP enabled, the card gains a
Disable two-factor authenticationcontrol. Select it and a confirmation section unfolds, explaining you will sign in with your password alone until you set it up again. -
Re-enter your current password — this proves it is really you at the
keyboard — and confirm with
Disable two-factor, or back out withCancel. A wrong password leaves two-factor exactly as it was, and the page says so:That password is incorrect. Two-factor authentication is still enabled.On success,Two-factor authentication disabled.appears and the card offersSet up TOTPagain.
To revoke a single passkey, for example after losing the device, click
Revoke on its row and confirm. The passkey stops working for
sign-in at once, the revocation is recorded in the audit log, and you can enrol
the device again later.
If your organisation requires a second factor for your role, turning it off sends you straight back to the set-up page on your next navigation.
Your password
There is no password box on the security page. To change your password, sign out
and use
Forgot password? on the sign-in screen — a reset link arrives by
email — or ask an administrator, who can send a reset from
Settings. If you sign in through your organisation's
own system (single sign-on), your password lives there, not in Aegis. There is
also no page listing your open sessions; Sign out in the top bar
ends the one you are in.
The privacy page: your AI acknowledgements
The first time you use an AI feature in Aegis, a
transparency notice (a short statement of
what the AI feature does with your data, shown before you first use it) asks for
your acknowledgement. The Privacy page is the record of those
acknowledgements — one row per notice, with the version you accepted. The page's
own description says it: revoking an acknowledgement means you are asked to
acknowledge the notice again the next time you use that AI system.
-
Open
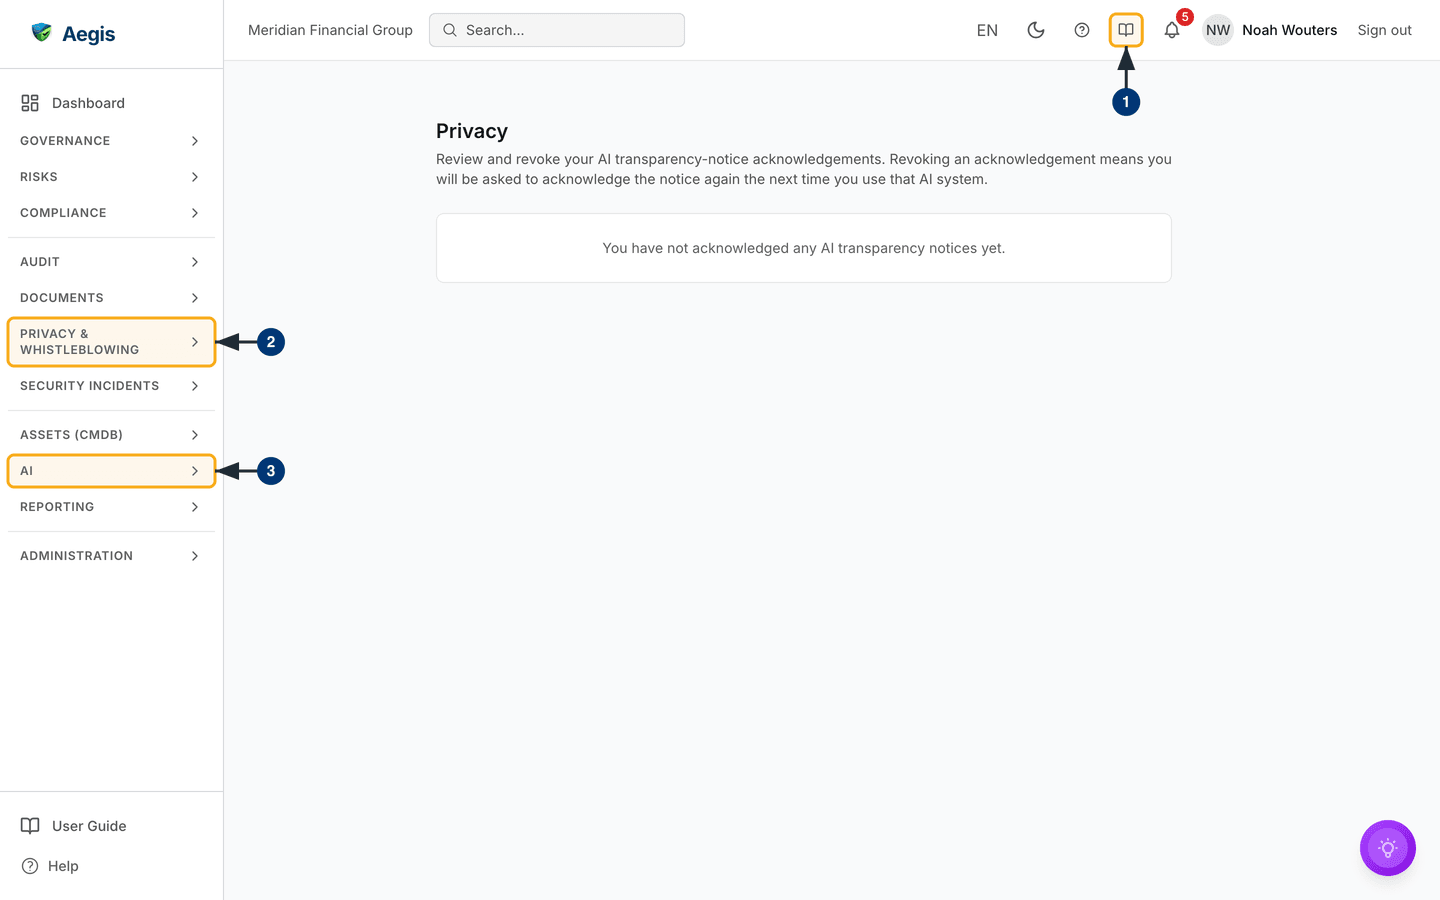
Privacyin the account navigation at the top of any account page (top-bar avatar →Profile→Privacy), or/account/privacydirectly. While you are there, the open-book button in the top bar opens this chapter. -
Do not confuse it with the
PRIVACY & WHISTLEBLOWINGgroup in the left menu: that group holds your organisation's privacy and whistleblowing work (see GDPR), not your own consent record. -
Use an AI feature — many sit under the
AIgroup in the left menu, others inside modules. When its notice appears and you acknowledge it, a row is added here.
Reading and revoking acknowledgements
If you have never acknowledged a notice, the page says so:
You have not acknowledged any AI transparency notices yet. — which
is what the captured screen shows. Once you have, each row shows the notice
title, the AI system it belongs to and the notice version you acknowledged, such
as acknowledged v1. If a notice has moved on since, the row adds
that the acknowledged version is superseded and names the current version.
Select Revoke on a row to withdraw an acknowledgement.
Acknowledgement revoked confirms it and the row disappears. Nothing
is switched off — the next time you use that AI feature, the notice is shown
again and asks afresh.
If the list cannot be loaded, the page says
Could not load your acknowledgements. with a
Retry button.
Tips and limits
-
You edit your own name, job title and phone number on
Profile; your email and role are managed by an administrator under Settings, and your role decides what the rest of Aegis shows you (see What each role can do). - If codes from your authenticator app are rejected, check the phone's clock — TOTP codes depend on the time being right. If the phone itself is gone, an administrator can help you regain access.
- Backup codes are shown only once, at the end of TOTP set-up, and the security page offers no way to view them again. Note that the sign-in screen currently asks only for the 6-digit code from your authenticator app; it has no box for a backup code.
- Revoking an AI acknowledgement is about consent bookkeeping, not a switch: AI features stay available to your role, and the notice reappears on next use.
Where this connects
- Signing in — the sign-in flow itself, including what the second-factor challenge looks like.
- Dashboard — where the second-factor banner appears.
- AI Dashboard — where the AI features behind those transparency notices live.
- Settings — the administrator's side: users, roles and single sign-on.