Scenario: handling a data-subject request
A former customer emails to ask for a copy of everything you hold about them, and the legal clock starts the moment the request arrives.
Under the GDPR (the European Union's data-protection law) people may ask to see, correct, delete, restrict, or take away the personal data an organisation holds about them. You then have one calendar month to respond, with a single two-month extension allowed for genuinely complex cases. This chapter follows one data-subject request (DSR — a formal request from an individual to exercise one of those rights) from the inbox to closure, across three screens: the DSR queue, the request's own page, and the audit log. The GDPR chapter is the full module reference; this one shows the order the screens come up in and who does what at each turn.
Who handles a DSR
Two people appear in the journey, because Aegis splits the work along real permission lines. Marta, a Manager and the organisation's privacy lead, logs the incoming request — creating one needs the compliance write permission that only Manager and Admin hold. Sofia, a Contributor on the privacy team, then works it: acknowledging, responding and refusing are covered by a separate DSR-handling permission that a Contributor does have.
One more rule shapes what each of them sees. A
Contributor or
Viewer sees only the requests
assigned to them plus the unassigned ones;
Manager and
Admin see every request. There is no
separate "DSR handler" role. Each request can carry an assignee — its page shows
an Assigned To line when one is set — but no Aegis screen sets it
today, so a request logged from the form arrives unassigned. That matters later:
on an unassigned request a Contributor can acknowledge, but the advancing and
closing actions are left to a Manager or Admin (see
Tips and limits). The whole area needs the
GDPR module switched on for your organisation.
What's on this screen
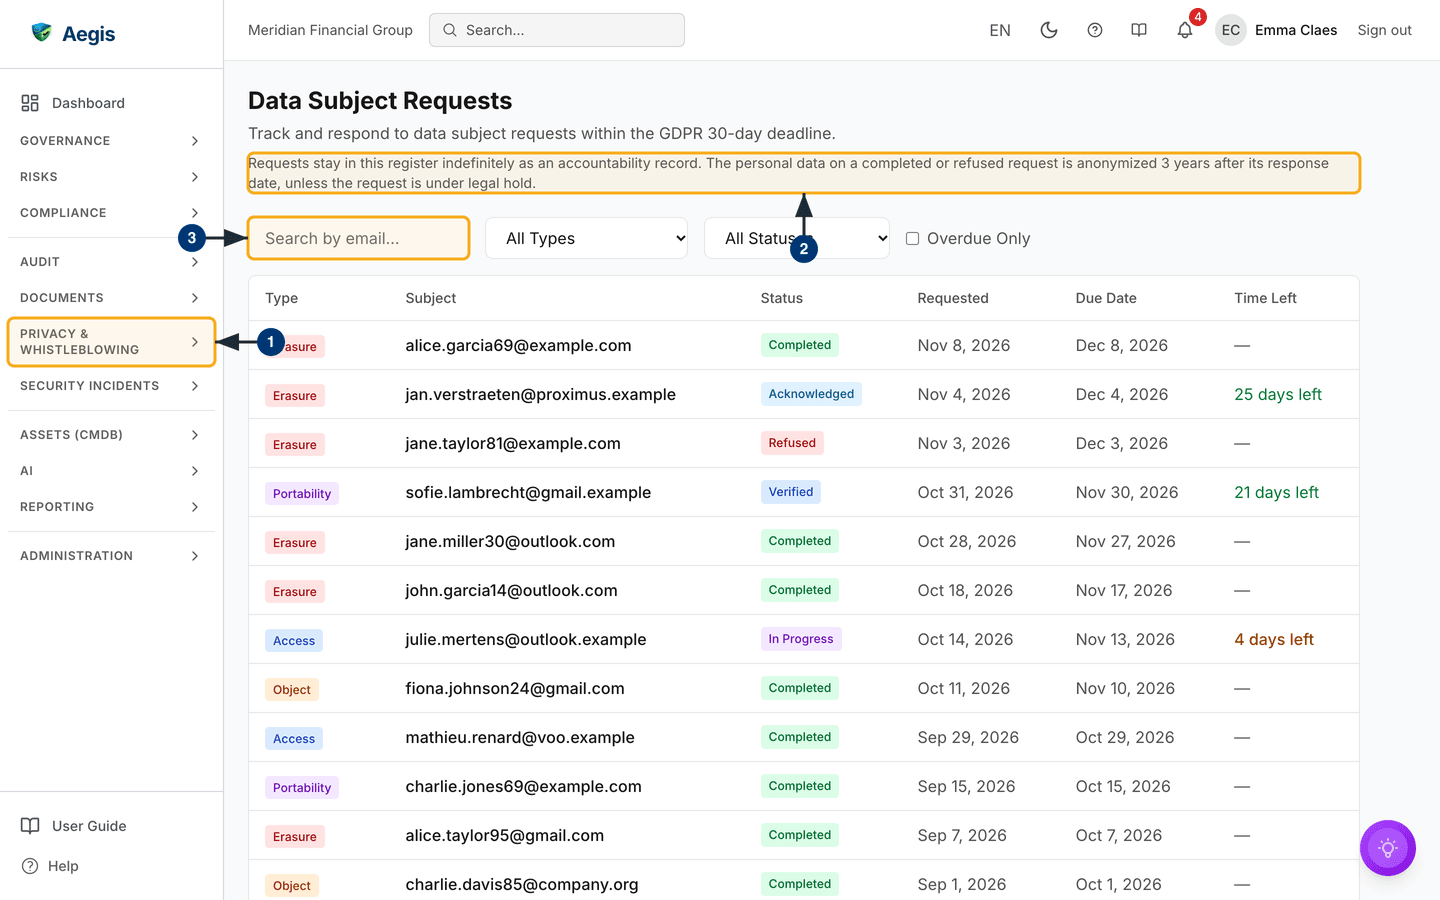
The queue lives at /gdpr/dsr. The header reads
Data Subject Requests
above the reminder line "Track and respond to data subject requests within the
GDPR 30-day deadline". Beneath that, a smaller line states the register's
retention position: requests stay in the register indefinitely as an
accountability record, and the personal data on a completed or refused request
is anonymised three years after its response date, unless the request is under
legal hold. Two banners can appear above the header but are absent from the
capture: one when your role could not be loaded (permission-gated controls are
then hidden), and one when an administrator has turned AI assistance off,
explaining that the AI steps are paused while deadlines and manual handling
continue.
Directly under it sits a filter bar with four controls: a
Search by email... box, an All Types dropdown, an
All Statuses dropdown, and an Overdue Only tick box.
The search matches any part of the requester's email address, the filters
combine, and changing any of them returns you to the first page. The status
dropdown offers every status plus Open (not closed), which groups
the requests still in progress — the same set the GDPR overview counts. The
New Request button belongs at the far right of that same row and
leads to the full-page form at /gdpr/dsr/new — but it is drawn only
for someone who may create requests. The screenshot below was captured as a
Contributor, so that corner is empty. That is exactly what Sofia sees. Your own
name sits at the top right of the header, between the notification bell and
Sign out; it decides both which requests the queue returns to you
and whether New Request is drawn at all.
The table beneath has six columns: Type (a coloured badge such as
Access, Erasure, Portability or
Object), Subject (the requester's email address),
Status, Requested (the date logged),
Due Date (30 days later), and Time Left. Every status
has its own coloured badge, including Acknowledged. Next to the
status badge, a red Acknowledgement overdue badge appears when a
request is still Pending after its three-day acknowledgement
deadline, and an amber Legal hold badge marks a request exempt from
the retention anonymisation. The countdown reads green while there is room — "25
days left" and "21 days left" in the captured screen — turns amber at seven days
or fewer ("4 days left" on the In Progress row), red once the
deadline has passed, and shows a dash once a request is
Completed or Refused. Twenty requests fit on a page,
with Back and Next below the table when there are
more; when nothing matches, the table reads "No data subject requests found".
Selecting any row opens that request's own page. The queue shown is the
fictional demo organisation, so the addresses are placeholders rather than real
people.
Step 1 — Open the queue
-
Open the
Privacy & Whistleblowinggroup in the left menu and chooseGDPR. The GDPR overview appears with a row of metric cards. TheData Subject Requestscard carries the pending and overdue counts and links straight to/gdpr/dsr, where the queue opens. - Read the retention line under the heading. It tells you what Aegis will do with a closed request: keep it as a record, and anonymise the requester's personal data three years after the response date unless the request is on legal hold. Bear it in mind before you promise a requester anything about retention.
-
Find the request with the search box and filters. Typing
part of the requester's address into
Search by email...narrows the table as you type. SettingAll StatusestoPendingshows everything not yet acknowledged; tickingOverdue Onlyshows only requests past their due date. Each change reloads the table in place. -
Select the row for the request you are working. Aegis opens
that request's own page at
/gdpr/dsr/<id>, with a breadcrumb back toData Subject Requestsand a heading naming the request type and the requester's address. Because it is a real page and not a pop-up, you can bookmark it or paste the link into a task.
Step 2 — Log the request and start the clock
The email lands in the privacy mailbox. Marta records it, because a request that
is not in the queue carries no deadline. Selecting New Request at
the end of the queue's filter bar opens a page of its own,
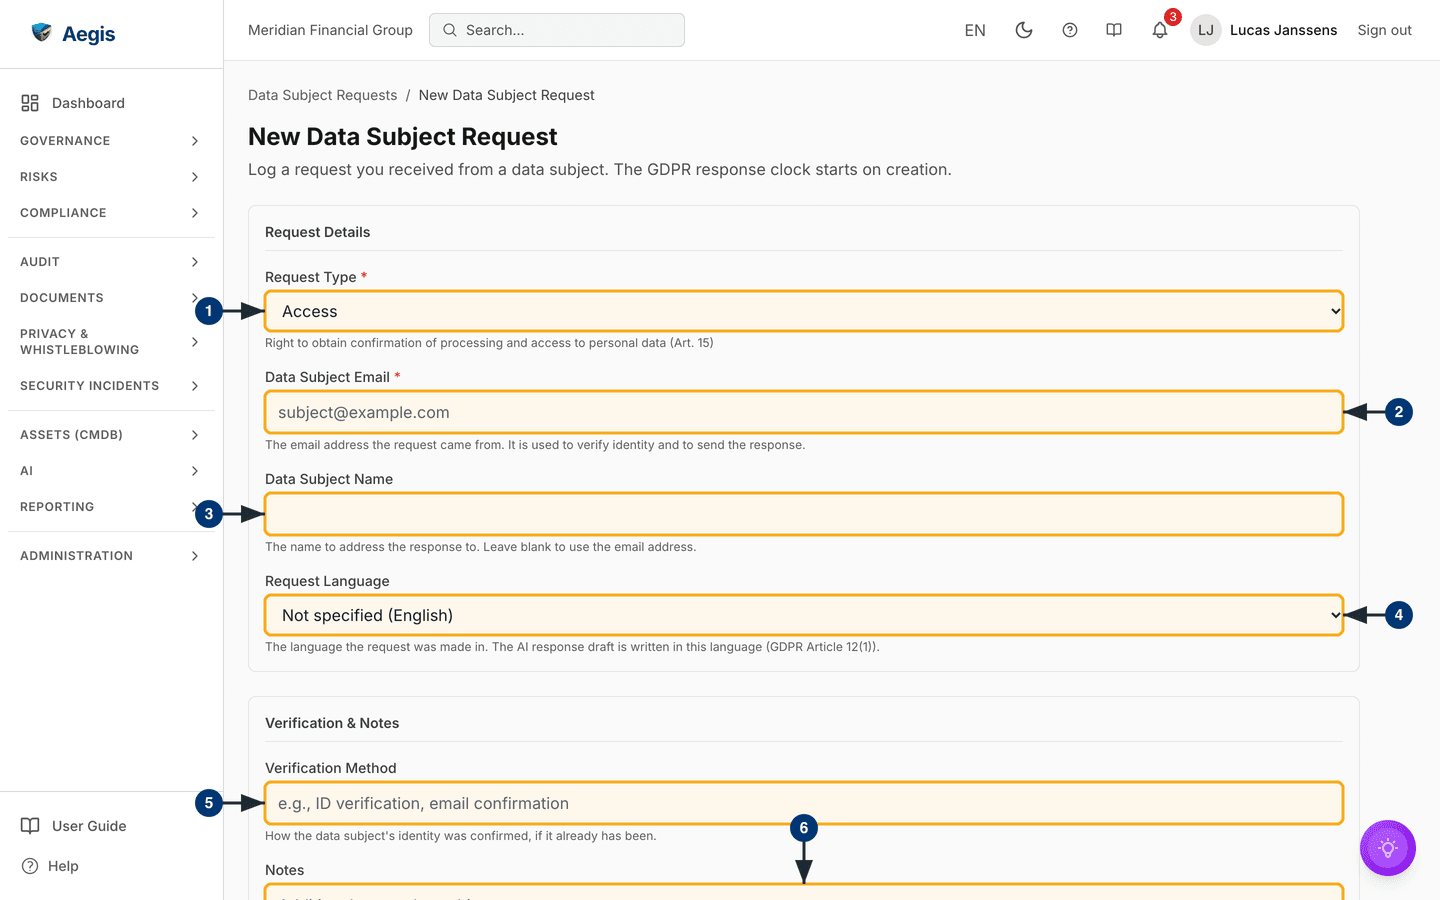
New Data Subject Request at /gdpr/dsr/new, with a
breadcrumb back to Data Subject Requests and the reminder "Log a
request you received from a data subject. The GDPR response clock starts on
creation." under the heading. The form sits in two boxed sections —
Request Details and Verification & Notes — with a
short line of help under every field. Opening the address as Sofia would end
differently: a role without the compliance write permission is turned away to an
unauthorised page.
-
Choose the right the person is exercising in
Request Type. The dropdown starts onAccess; seven types are offered, listed below. The line under it explains the selected right — "Right to obtain confirmation of processing and access to personal data (Art. 15)" in the captured screen — and rewrites itself when you change the type, so you can confirm the choice before going further. -
Enter the requester's address in
Data Subject Email. This field is required and must be a valid address; as the help text under it says, it is used to verify identity and to send the response, and it is the identifier the request carries throughout. An invalid entry shows a message under the field and the form does not submit. -
Add the requester's name in
Data Subject Name, if you have it. Optional. It is the name the response is addressed to; left blank, the email address is used instead. -
Set
Request Languageto the language the request was written in. The dropdown starts onNot specified (English)and offers the seven languages Aegis supports. As the help line explains, the AI response draft is written in this language, in line with GDPR Article 12(1); the request page shows it asRequest Languageonce set. -
Record how you checked identity in
Verification Method, if you have already checked it. Optional free text — "copy of passport", "video call with ID check". This form is the only place that writes the field: nothing on the request's page can add it afterwards, so if verification is still to come, keep your own record of how it was done. -
Add any context in
Notes. Also optional, and as the help line states, never shared with the data subject — it is internal context for whoever handles the request. A blue note further down the page restates the 30-day deadline rule and the possible two-month extension. -
Select
Create Requestat the foot of the page. If your organisation requires the AI transparency notice to be acknowledged first, it appears now; once you accept it, the request is created. A confirmation appears and Aegis takes Marta straight to the new request's own page. The request starts inPendingwith aDue Date30 days out and an acknowledgement deadline three days out; back in the queue it shows a green countdown.Cancelbeside the button returns to the queue without saving anything.
| Type | What the person is asking for |
|---|---|
Access |
A copy of their personal data and how it is used (Article 15) |
Rectification |
Correction of data that is wrong or incomplete (Article 16) |
Erasure |
Deletion of their personal data (Article 17) |
Restriction |
A pause on using their data without deleting it (Article 18) |
Portability |
A machine-readable copy they can take elsewhere (Article 20) |
Object |
An objection to your processing of their data (Article 21) |
Automated Decision |
Human review of an automated decision about them (Article 22) |
Aegis counts the deadline from the moment you create the record, not from
the date the email arrived. If a request sat in a shared mailbox for four
days, write the real received date into Notes at creation and
manage the earlier legal deadline yourself. The Due Date column
will always be the slightly generous one.
Step 3 — Acknowledge receipt
Sofia opens the request. The details grid shows the type, the data subject, the
requested and due dates, the Acknowledgement Due date (in red once
it has passed unacknowledged), and the request language when one was set. Under
it is a section headed Fulfillment, with a stepper showing the
stages Pending → Acknowledged → Verified → In Progress, each
stamped with its timestamp once reached, and the actions available at the
current stage below it. Aegis gives acknowledgement its own short clock: three
days from creation. Past that, the request carries a red
Acknowledgement overdue badge in the queue and on its page.
-
Select
Acknowledge Request. Aegis records the acknowledgement, stamps the time, adds a line underNotesnaming who acknowledged it and when, and moves the request toAcknowledged. Only then does it try to email the requester an acknowledgement with a reference number and the due date. The stepper advances and the button disappears — it is offered only while a request isPending, and only once. -
Read the
Acknowledgement deliverypanel that appears. This amber panel stays on the page and reports what happened to the email: the mail service accepted it, delivery is still in progress, it could not be confirmed, or no attempt has started. Aegis never resends an email whose outcome is uncertain, so the trail never claims a notification that did not go out — and never sends the requester two. -
Close the gap if the email did not go out. Where no attempt
has started, the panel offers
Send pending acknowledgement. Where you informed the requester some other way, or verified the original delivery yourself, choose the method underHow was delivery confirmed?, write a confirmation note of up to 2,000 characters, and selectRecord confirmation without sending email. The panel then shows your name against the confirmation.
If no mail server is configured for your organisation,
Acknowledge Request still records the acknowledgement, but no
email is sent: the delivery panel says no attempt has started, and
Send pending acknowledgement will fail until email is set up.
Tell the requester by another route and record it with
Record confirmation without sending email, and ask an
Admin to set up email in
Settings.
Step 4 — Verify the requester's identity
Aegis tracks this part of the work; it does not do it for you.
-
Confirm the requester is who they claim to be. Releasing
one person's data to another is itself a breach. The check happens outside
Aegis — an ID document, a video call, a confirmation from an existing
account. If the method was recorded in
Verification Methodat creation, the request's page shows it; if not, keep the evidence of how you checked in your own files, because the page cannot add it afterwards. -
Record the check with
Mark Verified. Once the request isAcknowledged, the fulfilment section offersMark Verifiedto a Manager or Admin, and to a Contributor on a request assigned to them. Selecting it moves the request toVerifiedand the stepper advances. Do this only after the identity check has actually been done — the button records your judgement, it does not perform the check. -
Select
Start Workwhen the gathering begins. On aVerifiedrequest the same spot offersStart Work, which moves it toIn Progress— the only stage at which an AI draft can be approved, and an honest signal to colleagues that the request is being handled.
Step 5 — Gather what the organisation holds
- Collect the data and its context — the categories held, why each is processed, who it is shared with, and how long it is kept. Your records of processing activities are the map for this work.
-
Assemble the reply outside Aegis. The request page has no
field for working notes after creation, so the export or letter lives in
your own systems while you build it. When it is ready, the
Complete Manuallyaction in the next step records the text against the request; Aegis holds the record, the deadline and the trail.
Step 6 — Respond, or refuse
A request ends one of two ways, and both are final: once it reads
Completed or Refused, the fulfilment actions vanish
and the status cannot move again. The route to Completed is either
approving an AI draft where one is offered — see
The AI assist below — or the
Complete Manually action, which the page offers at every stage from
Acknowledged on. Refuse is offered at every open
stage. All three go to a
Manager or
Admin, and to a
Contributor only on a request
assigned to them. On any other request a Contributor sees, in place of these
buttons, the note "Unassigned — ask a manager to assign it to you before
responding or refusing."
-
To fulfil the request with your own text, select
Complete Manually. A green panel opens with a required box for the response you are sending to the requester.Confirm Completionstays disabled until you type something; selecting it saves the text against the record, marks the requestCompleted, stops the countdown, and shows the text in a greenResponsepanel. Completing is final — check the text before you confirm. Sending it to the requester through your normal channel remains your job. -
Or approve the AI response. Where an
AI-Drafted Responsepanel is present and the request isIn Progress,Approve & Senddoes the same with the drafted text, including any edits a reviewer saved: it saves the draft against the record and marks the requestCompleted. -
To decline, select
Refuse. A red confirmation panel opens with the warning that refusing is final and a requiredRefusal Reasonbox.Confirm Refusalstays disabled until you type something;Cancelcloses the panel and changes nothing. -
Select
Confirm Refusal. The request moves toRefused, the reason is saved permanently and shown in a red panel on the page, and the countdown column switches to a dash.
A manifestly unfounded or excessive request may be declined. You must still tell the person you are declining, give your reasons, and point them to their right to complain to a supervisory authority — within the same one-month window. Aegis records the refusal; the letter is yours to send.
Step 7 — Consider whether it is also a breach
Some requests surface something worse than they asked about: data that should
have been deleted years ago, or an address sitting in a system nobody knew
about. If the work uncovers a personal-data breach, open
Incidents in the Security Incidents group of the left
menu and log it there, on its own 72-hour clock. The
incident-response scenario picks the story
up from that point.
Step 8 — Keep the record
Months later a supervisory authority may ask how the request was handled. Open
Audit Log in the Audit group, at /log.
There is no filter for a single request, and the
Search description... box matches only an entry's description,
never the requester's address. For a DSR the descriptions read
DSR acknowledgement delivery event for an acknowledgement and for
each delivery follow-up, Update on Dsr for
Mark Verified and Start Work,
Dsr Refuse on Dsr for a refusal and
Dsr Complete on Dsr for a response — so search for those words, or
narrow with Filter by action or by date. Opening an entry shows the
timestamp, the person who acted, and the recorded detail: for a response or
refusal, the request type and the subject's address; for an acknowledgement, the
delivery status. The queue itself has no bulk export. The
audit log has one where the licence includes audit
export, and it is the record to rely on for an inspection.
The AI assist
When a request is logged, and where the licence includes GDPR automation and AI
is switched on, Aegis queues a data-mapping job that chains into a drafted
reply, written in the request's language. The draft is stored as an AI
suggestion for a person to review, and the request page now shows it: an
AI-Drafted Response panel appears at any open stage —
Pending, Acknowledged, Verified or
In Progress — once a draft exists, and a line under
Notes records when it was generated. The panel carries a confidence
percentage and counts of the systems and records the draft drew on, above three
buttons:
-
Edit Draftturns the draft into an editable box withSaveandCancel; a saved edit is markedEdited by reviewer. -
Reject Draftopens a red panel warning that the draft is discarded and cannot be restored, with an optional reason box andConfirm Rejection. -
Approve & Sendappears only once the request isIn Progress, and closes it with the draft text as the response.
Nothing is ever recorded as the answer until a person approves it — the AI proposes, Sofia decides. The buttons follow the same assignment rule as the closing actions, so a Contributor sees them only on a request assigned to them.
If an AI step ran but stored nothing, the panel's place is taken by an
AI draft not available notice that says why — for example that
AI is turned off for the organisation, or that drafting failed after its
retries — and suggests handling the request by hand. When an administrator
has turned AI off, a banner at the top of the queue and the request page
says the AI steps are paused. Without GDPR automation in the licence no
draft is made at all. In every case Complete Manually closes
the request with a response you write yourself.
Tips and limits
-
The two-month extension for complex cases is not a status in Aegis, and
Notescan only be written when the request is created — nothing on the request page edits it afterwards. Track an extension outside Aegis and watch theDue Datecolumn yourself; it will not move. - To correct a response after a request is locked, log a fresh request for the same person and note that it supersedes the earlier one.
-
Expiredis a final status a request can reach once its deadline passes. Where the licence includes GDPR automation, a background job checks every fifteen minutes, raises escalating alerts on both the acknowledgement and the 30-day deadline, and expires overdue requests still sitting inPending,AcknowledgedorVerified. Without that automation nothing expires by itself — work theOverdue Onlyfilter instead. -
Retention is automatic. Three years after a completed or refused request's
response date, the personal data on it is anonymised and the request page
shows when that happened; the request itself stays in the register. A
request under legal hold is exempt and carries a
Legal holdbadge, but no screen sets or clears that hold today. - A Contributor who cannot find a request they expect to see is probably outside its assignment — it is assigned to someone else, so the queue does not return it to them. A Manager or Admin sees every request and can work it instead.
-
Assignment also gates the advancing and closing actions. A
Contributor may open and
acknowledge an unassigned request, but
Mark Verified,Start Work,Complete Manually,Refuseand the AI draft buttons are offered only on requests assigned to them — on an unassigned one the page shows the "Unassigned" note instead. Manager and Admin may close any request. Because no screen sets the assignee today, in practice the closing action on an unassigned request falls to a Manager or Admin. - Logging by hand is not the only intake route. Where the licence includes GDPR automation, an Admin or Manager can point Aegis at a privacy mailbox from Connectors. This chapter follows the manual path, which every licence has.
Where this connects
The full module reference — all seven request types, every status, and the rest of the privacy area — is in the GDPR chapter, and Incidents covers the breach path. The permanent record of every change lives in the audit log, which an assessor will also ask for during an external audit. For who may log, work and close requests, see What each role can do; for the sidebar groups used here, see The left menu. Terms glossed in brackets are collected in the glossary.