DORA Compliance
Keep your Digital Operational Resilience Act programme in one place — the entity profile, the ICT asset register, your third-party providers, your resilience tests, and the Article 18 incident register.
DORA (the Digital Operational Resilience Act, EU 2022/2554 — the European law that requires banks, insurers, investment firms and similar financial entities to show their IT can withstand and recover from disruption) rests on five pillars. This module holds the records a supervisor asks for: who you are under DORA, which ICT systems carry your critical functions, which suppliers you depend on, how you test, and which incidents crossed the reporting thresholds.
It is a pay-per-framework module, and two states can replace its pages. Without
the DORA entitlement on your licence, the dashboard shows a short message that
DORA is not available on your current plan, and each register page shows a
DORA Not Available card in its place. If your organisation holds
the entitlement but an administrator has switched DORA off in
Settings → Frameworks, every DORA page shows
DORA is switched off instead: the data is kept and comes back when
the framework is switched on again, and an Admin also sees an
Open Settings → Frameworks link. Neither state redirects you; the
card appears on the page you opened, so you can see why it is empty.
Who uses it
Access is granted by permission, not by one minimum role. Every DORA page
requires
dora:read; anyone without it is redirected to
/unauthorized. Writing needs dora:update, and the
buttons that need it are hidden rather than disabled. Classifying an incident
needs dora:classify, and each register's
Export CSV button needs dora:report — without it the
button is not rendered at all. The AI Register Readiness button
additionally needs the permission to run AI actions.
| Role | What they can do in DORA |
|---|---|
| Admin |
Every DORA permission — read, update, classify and report — so every
control on every page, plus the link back to
Settings → Frameworks when DORA is switched off.
|
| Manager |
Read everything, configure the profile, add, edit and delete assets,
providers and resilience tests, classify incidents, run the AI
action, and — holding
dora:report — export the registers to CSV.
|
| Contributor |
The same, apart from dora:report — so the
Export CSV
button does not appear on any of the registers.
|
| Viewer |
Read-only. Every page opens, but Add, row
Edit and delete, the profile Edit control,
Export CSV and AI Register Readiness are
all hidden. The classify action on the DORA incidents list is still
drawn, but the request behind it is refused without
dora:classify.
|
What's on this screen
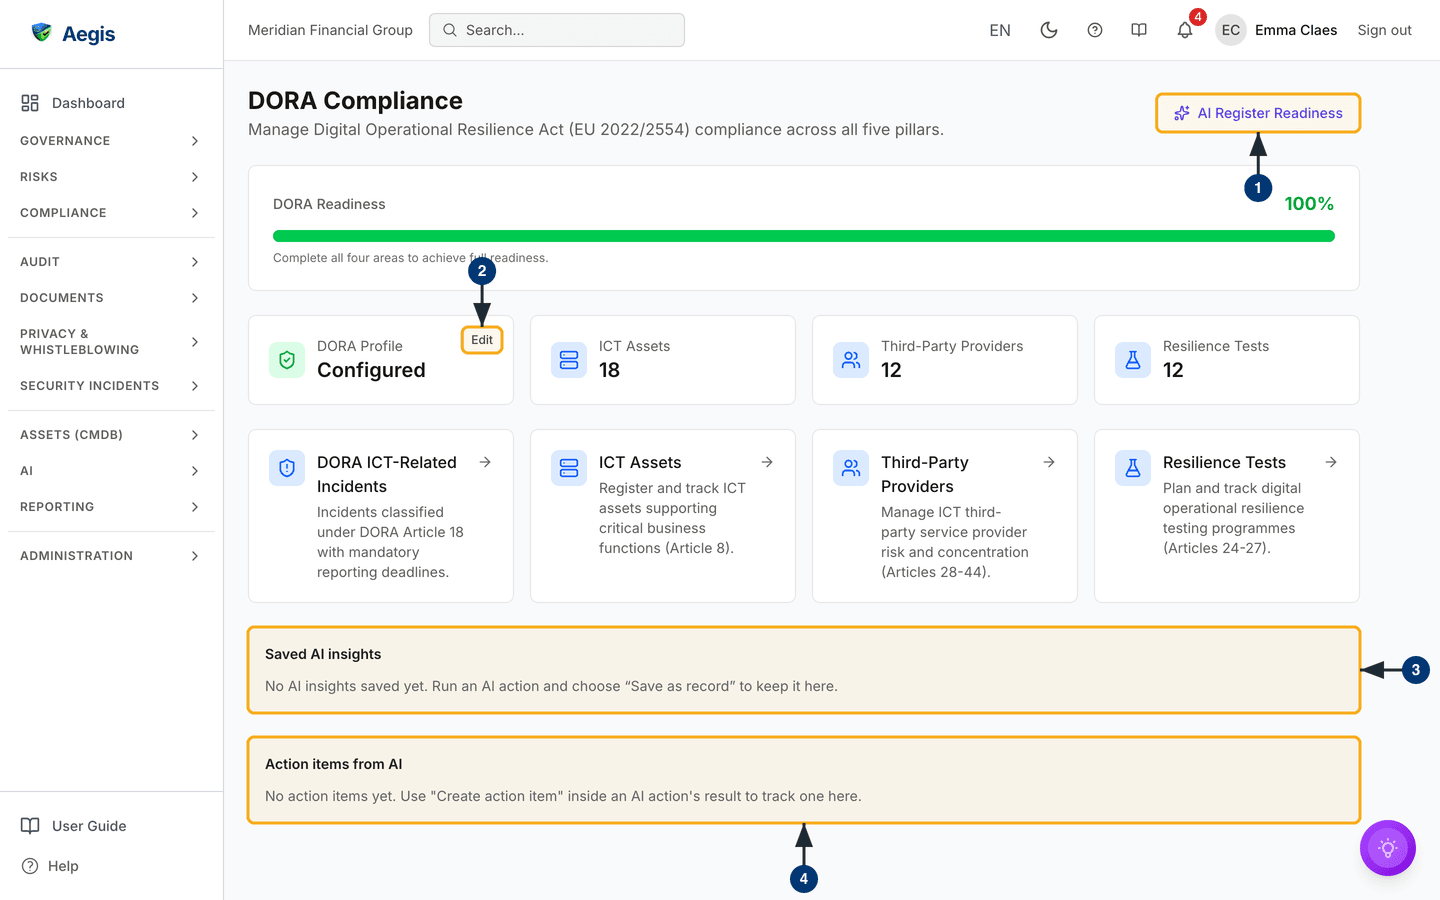
Open /compliance/dora from the Compliance group in the
left sidebar. The screenshot below was captured as a Contributor, so every write
control is visible but no export control is. The header reads
DORA Compliance, with the subtitle "Manage Digital Operational
Resilience Act (EU 2022/2554) compliance across all five pillars." and the
page's only primary action — AI Register Readiness — on the right.
Below it, the DORA Readiness bar scores four areas at 25% each: a
configured profile, at least one ICT asset, at least one third-party provider,
and at least one resilience test. It is red below 25%, amber from 25% and green
from 75%, captioned "Complete all four areas to achieve full readiness." In the
captured screen it reads 100% in green, because the demo
organisation has something in all four areas.
Under the bar sit four summary cards: DORA Profile, showing
Configured (or Not configured) with a small
Edit button in its corner, then ICT Assets,
Third-Party Providers and Resilience Tests, each with
a count — 18, 12 and 12 on the captured screen. A row of four navigation cards
follows, each with a one-line description and an arrow:
DORA ICT-Related Incidents (Article 18 incidents with their
reporting deadlines), ICT Assets (Article 8),
Third-Party Providers (Articles 28–44) and
Resilience Tests (Articles 24–27). Each opens the matching
register.
Two panels close the page. Saved AI insights lists the readiness
narratives you have kept; on the captured screen it is empty and reads "No AI
insights saved yet. Run an AI action and choose “Save as record” to keep it
here." Below it, Action items is also empty and says items are
created with Create action item inside an AI action's result.
-
Select
AI Register Readiness. A modal opens explaining what the action reads, with aRun Register Readinessbutton; the narrative then streams into the modal. -
Select
Editon theDORA Profilecard. TheEdit DORA Profiledialog opens with the entity fields pre-filled; with no profile yet, the button readsConfigureand opensSet up DORA Profile. -
Read the
Saved AI insightspanel. Each kept narrative shows its save date, a confidence badge and the opening lines, withShow moreto expand it and — for a user holdingdora:update—Create action item,EditandDelete. On the captured screen the panel is empty. -
Check
Action itemsbelow. SelectingCreate action itemon a saved insight opens no form: Aegis creates the item straight away, taking its title from the insight's first line and its description from the whole narrative, confirms with a short message, and the item appears here without a page reload.
Each 25% only confirms that an area has been started — a profile exists, and each register holds at least one record. It says nothing about whether your asset inventory is complete, your tests passed, or your providers have been assessed. A green 100%, as on the captured screen, is a finished setup checklist, not a finished programme.
Configure the DORA profile
The profile records who you are under DORA and is the first 25% of readiness. It is set from the dashboard card, not a separate page.
-
Select
Editon theDORA Profilecard — the button readsConfigurewhen no profile exists yet. TheEdit DORA Profile(orSet up DORA Profile) dialog opens. -
Choose the
Entity Typefrom the list of DORA entity types — credit institution, payment institution, investment firm, insurance undertaking, crypto-asset service provider, ICT third-party service provider and the others the regulation names. This is the only required field; theSave profilebutton stays disabled until it has a value. -
Choose an
Entity Category(Financial entityorICT service provider), type yourFinancial Sector, and pick aProportionality Tier—Simplified,StandardorEnhanced, the lighter or fuller regime that matches your size and risk. -
Add the supervisory details that apply: tick
ESA Designatedif a European Supervisory Authority has designated you, then fill inCompetent Authorityand its URL,Lead Overseer Authority, and theApplicable SinceandLast Assessmentdates. All of these are optional. -
Select
Save profile. The dialog closes with a "DORA profile saved" message and the card showsConfigured, adding 25% to the readiness bar if it was not set before.
If a stored profile carries an entity type that is not on the DORA list — from an older free-text entry, for example — the card turns amber and says the type is not recognised. The dialog then selects nothing for you and asks you to choose the type that applies.
Register ICT assets (Article 8)
This is your information-asset inventory under Article 8: the hardware,
software, network, data, services and cloud systems behind your critical
business functions. Open it from the
ICT Assets navigation card.
The header carries Export CSV (with dora:report) and
Add ICT Asset (with dora:update). The columns are
Name, Type, Criticality,
Status, Business Function and Actions,
with a view (eye) action on every row and, for writers, an edit (pencil) and a
delete action. Twenty-five rows fit a page. An empty register reads "No ICT
assets registered yet."
-
Select
Add ICT Asset. TheAdd ICT Assetdialog opens. -
Enter the
Asset Name— the placeholder suggests "e.g. Core Banking Platform" — then pick theAsset Type: Hardware, Software, Network, Data, Service, Cloud or Other. -
Set the
Criticality— the form offers Low, Medium, High and Critical, and new records start at Medium — then theBusiness Functionit supports and itsLocation. The form has no status field; a new asset is saved asActive. -
Select
Save. An "ICT asset created" message appears, the table reloads with the new row at statusActive, and the dashboard'sICT Assetscount rises. - To remove an asset, select the delete action on its row and confirm the prompt "Delete the ICT asset … ? This removes it from the register."
Register third-party providers (Articles 28–44)
This register tracks the ICT suppliers you depend on and the concentration risk
they carry — the exposure that builds when too much rests on one provider. Open
it from the
Third-Party Providers card.
The columns are Name, Type, Critical,
Headquarters, Contract End,
Substitutability and Actions; a contract ending within
90 days is flagged in its cell. The header offers Export CSV (with
dora:report) and Add Provider (with
dora:update). Rows carry view, edit and delete actions, the last
two for writers only.
-
Select
Add Provider. TheAdd Providerdialog opens. -
Enter the
Provider Name, then its identifiers: theLEI(the 20-character Legal Entity Identifier) where it has one, and theEUID(the European Unique Identifier) only when it has no LEI — both may be recorded. Aegis checks each as you save and shows an inline error for an LEI that is not valid or an EUID that does not start with a two-letter country code. -
Choose the
Provider Type, then tickCritical Providerif the supplier underpins a critical or important function. -
Pick the
Headquarterscountry from the list — it is stored as the two-letter code shown beside each name — set theContract Enddate, and choose theSubstitutability: Easy, Moderate, Difficult or Not Possible, meaning how hard the provider would be to replace. -
Select
Save. The provider joins the table and the dashboard'sThird-Party Providerscount rises. -
Select the view (eye) action on a row to open the provider detail dialog. It
shows the recorded LEI and EUID and includes a
Concentration Risk (DORA Art. 29)section: the overall concentration risk, this provider's risk, the contributing factors and recommendations.
Manage the resilience-testing register (Articles 24–27)
This holds your testing programme, from vulnerability assessments and
penetration tests up to a
TLPT (Threat-Led Penetration Test, the
advanced red-team exercise DORA expects of larger entities). Open it from the
Resilience Tests card. The header carries
Add Test (with dora:update),
Export CSV (with dora:report, downloading
dora-resilience-tests-register.csv) and Refresh.
Twenty tests fit a page, with a running total beneath the table.
-
Read the table:
Name(the test scope, with the test type as a badge beneath it),ICT Asset,Status,Last Run,Next ScheduledandFindings, plusActionsfor writers. Statuses are Planned, In Progress, Completed, Cancelled or Overdue — Overdue is derived, not stored: it is shown when the next due date, or the planned date where there is none, has passed and the test is not yet completed.Next Scheduledshows the date the Overdue badge is derived from. -
Check the
Findingscell for the number of findings, with a separate red count of critical findings where there are any. -
Select
Add Test. TheAdd Resilience Testdialog opens. Enter theTest Scope(required — "e.g. External penetration test of the payment gateway"), choose theTest Type, link anICT Assetor leave itNot linked, pick aStatus(Planned, In Progress or Completed), and set thePlanned DateandNext Due Date. The next due date cannot fall before the planned date. -
Select
Save. A "Resilience test created" message appears, the row joins the table, and the dashboard'sResilience Testscount rises. -
Select the edit (pencil) action on a row to record what happened. The
Edit Resilience Testdialog addsOutcome(Pass, Fail, Partial or Inconclusive),Executed DateandCompleted Date, the findings counts by severity, aRemediation Planwith its due date andRemediation Status, and theCancelledstatus. - To remove a test, select the delete action on its row and confirm the prompt "Delete the resilience test … ? This removes it from the list."
Classify an ICT-related incident (Article 18)
Article 18 decides when an ICT incident counts as major and starts the reporting
clocks. The register at /compliance/dora/incidents lists the
incidents flagged as DORA incidents, with columns for Title,
Severity, Classification, Status, the
three deadlines — Initial (4h), Intermediate (72h) and
Final (1mo), each reading Sent, Due,
Overdue or N/A — and Actions. Under each
title a short banner says which stage is due or overdue, or that all deadlines
were met. Open it from the DORA ICT-Related Incidents card on the
dashboard; a Back to DORA link at the top returns you there.
Incidents enter the register from the incident itself. With DORA switched on,
each incident's detail page in Incidents carries a
DORA incident classification (RTS 2024/1772) section with a
Classify under DORA Art. 18 button (or
Re-classify under DORA Art. 18) for users holding
dora:classify. Inside the register, an incident with no
classification yet also shows a classify action — the warning-triangle button
beside the view action.
-
Select
Classify under DORA Art. 18on the incident, or the classify action in the register. TheDORA Article 18 Classificationdialog opens, with an amber note at the top saying the result is a recommendation only. On a re-classification the form is pre-filled with the criteria already stored on the incident. -
Answer the gate first: tick
Critical or Important Services Affectedif the incident touched one. Without it, the dialog explains, no threshold below can make the incident major. -
Fill in the materiality thresholds that apply —
Data Loss or Integrity Breach,Successful Malicious Access, the affected clients (as a percentage and a number), transactions and transaction value, financial counterparts,Reputational Impact,Critical Service Downtime (hours),Incident Duration (hours),Member States AffectedandEconomic Impact (EUR). UnderContext recorded with the decision, tickRecurring IncidentorSignificant Cyber Threatwhere they apply. -
Select
Classify. Nothing is saved yet: a result panel shows the recommendation —Classification: Major,Significant Cyber ThreatorNot Applicable— whether the critical-services gate was met, how many distinct materiality thresholds were met, and a reminder to assess related incidents if you flagged it as recurring. Changing any field clears the recommendation. -
Select
Confirm Classificationto record it. The panel turns green with "Classification confirmed and recorded on this incident." AMajorresult places the incident in the register and stamps the three deadlines;Significant Cyber Threatplaces it in the register without deadlines;Not Applicableclears any earlier classification and removes it from the register. If someone else changed the incident while you were reviewing, Aegis refuses the confirmation and asks you to run the classification again.
Once confirmed, the incident's DORA section shows the classification badge, the
date, the classification basis — the gate result, the matched criteria and the
recorded rationale — and a link to Open the DORA incident register.
The Article 18 check is a fixed rule test, not AI. Following RTS (EU)
2024/1772, an incident is major only when critical or important services are
affected and either a successful malicious access occurred or at least two
distinct materiality criteria were met — among them more than 10% of
clients, more than 100,000 clients, more than 10% of transactions, more than
two hours of critical-service downtime or 24 hours' duration, two or more
member states, data loss, or more than €100,000 of economic impact. Nothing
is written until you select Confirm Classification, and Aegis
files nothing with a supervisor. Per DORA Article 18 and EU AI Act Article
14, a human must confirm the final classification.
The AI assist
One AI action lives here: AI Register Readiness. Aegis first scores
your Register of Information (Article 28(3)) itself — the profile, the three
counts, and a fixed list of gaps ranked by severity and tied to DORA articles.
Only then does the model narrate that picture: where you stand, plus three to
five next steps drawn from your worst gaps. It never recomputes the score,
reorders the gaps, or invents a provider, an asset or an article.
-
Select
AI Register Readiness. The modal explains what will be read, and notes that the narrative summarises gaps Aegis has already detected. -
Select
Run Register Readiness. Progress lines appear as it reads the register, checks the counts, scores the gaps and drafts the narrative.Run againrepeats it. -
Choose
Save as recordto keep it. The narrative then appears inSaved AI insights, where you can expand, edit or delete it, or turn it into an action item.
The run is billable: it consumes one AI credit and is written to your AI usage
log. The button appears only for users who hold both dora:read and
the permission to run AI actions, which a Viewer does not have. Nothing it
produces changes a record — the output is a read, and the decisions stay with
you.
Tips and limits
- The readiness bar reaches 100% with one record in each register. It is a start-up measure, and the work does not end when it turns green.
- Information sharing, DORA's fifth pillar, has no register of its own here.
-
Each register exports to CSV from its own header, which is how you hand an
auditor a copy of the Register of Information — but the button needs
dora:report, so a Contributor cannot export. -
The classify action inside the incident register appears only for incidents
with no classification yet. To change an existing classification, open the
incident and use
Re-classify under DORA Art. 18. -
The deadlines are computed when you confirm a
Majorclassification. The initial notification is due four hours after classification, but no later than 24 hours from when you became aware of the incident if you classify within that day; the intermediate report is due 72 hours after the initial notification, and the final report one calendar month after the intermediate report. Classify promptly. -
Switching DORA off in
Settings → Frameworkshides the pages but deletes nothing.
Where this connects
For framework coverage in general, see Compliance frameworks and Control mapping. Article 18 classification starts from Incidents and continues in Incident reporting. Provider work overlaps with Vendors, and SaaS applications found by Microsoft Entra ID discovery can be registered here as third-party providers. ICT assets have a wider home in Assets (CMDB), and a mock audit can point to the ICT asset register as evidence. Follow-ups are worked in Action items, AI runs are listed in the AI dashboard, and Roles overview confirms who can reach these pages.