The Trust Center
Publish a public web page that shows customers, auditors and prospects your security and compliance posture — no Aegis account needed to read it.
The Trust Center is the one part of Aegis built to face the outside world. Rather than emailing a static PDF of your certifications, you publish one web page that anybody with the link can open, assembled from your live Aegis records each time it loads. You choose which sections appear, set the branding, write the opening wording, and curate the lists visitors read: your certifications, your sub-processors (the third parties that process data on your behalf), announcements, frequently asked questions, and a short public text for each approved policy. Visitors can click through from the home page to a page per framework and a page per policy.
You configure all of it on one screen at /settings/trust-center.
The public home page is served from your own Aegis address at
/{slug}, with a framework page at
/{slug}/frameworks/… and a policy page at
/{slug}/policies/…, all outside the signed-in application, with no
sign-in and no role check. Trust Center is included in every licence tier, but
the sidebar entry also depends on the TRUST_CENTER module being
provisioned for your tenant; if the entry is missing, it has not been switched
on for you.
Who uses it
An Admin and a
Manager hold the
Edit Trust Center permission: they see Save Changes,
the toggles respond, and the lists show their Add,
Edit, Delete and reorder controls. Turning the page on
and changing its slug is for an Admin only: a Manager sees the note "Only an
administrator can turn the public trust center on or off or change its public
slug. You can edit everything else on this page." and finds those two controls
inert. The same split applies further down: a document's visibility, its
auto-approval switch, the auto-approval domains, the reminder timing, publishing
an NDA version and the request report are Admin-only. A
Contributor and a
Viewer can open the same screen,
but a grey notice tells them access is view-only, there is no
Save Changes button, every branding and content field is inert, and
the lists show neither their Add form nor any row controls. The
published page has no role at all: anyone with the address can read it, and it
is offered to search engines.
What's on this screen
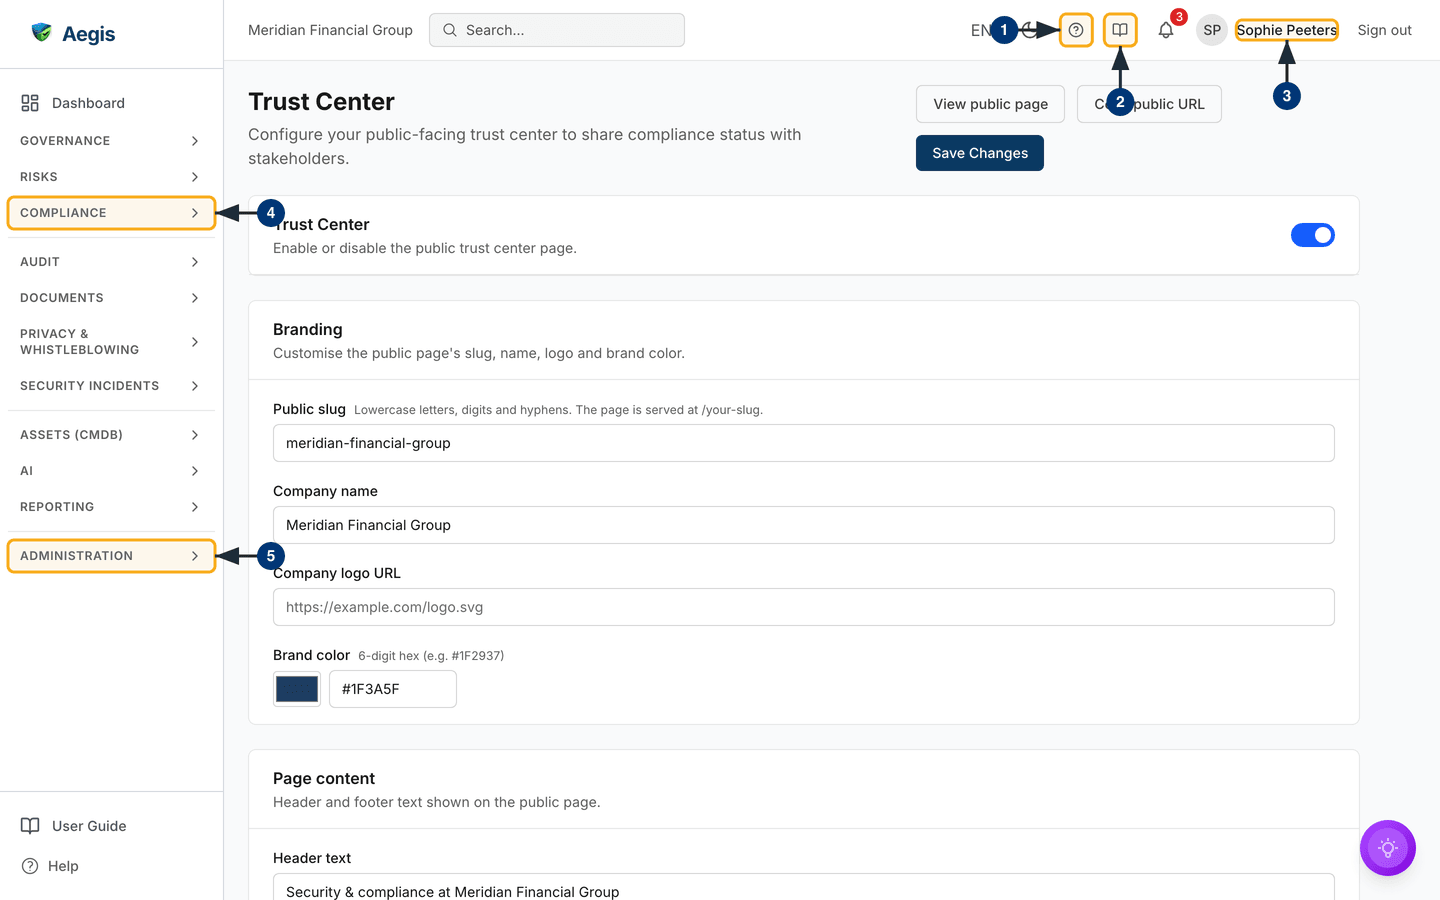
This is a single scrolling column of stacked cards — no table, no filter bar, no
side panel. Top left, the heading Trust Center sits above the line
"Configure your public-facing trust center to share compliance status with
stakeholders." On the right is Save Changes, and nothing you change
in the configuration cards takes effect until you select it.
View public page and Copy public URL appear beside it
once the master toggle is on and the slug box holds a value. The captured screen
shows a tenant that has already published, so all three buttons are there.
The first card is the master switch, titled Trust Center with the
line "Enable or disable the public trust center page." and one toggle on the
right — on in the capture. Branding follows, holding
Public slug (with the hint "Lowercase letters, digits and hyphens.
The page is served at /your-slug."), Company name,
Company logo URL and Brand color — the last a colour
swatch beside a box for a six-digit hex value. On the captured screen the slug
and company name are filled in, the logo box is empty (the faint
https://example.com/logo.svg is placeholder text) and a dark blue
brand colour is set. Then Page content with its
Header text and Footer text boxes.
Below the fold the cards continue in this order:
-
While the master toggle is off, an amber notice says the Trust Center is
disabled and that none of the sections are visible; the six section toggles
below it are dimmed and cannot be changed. Once the toggle is on and saved,
the notice is replaced by the
What the public page shows nowcard. -
Six toggle cards, all on by default —
Show policies,Show frameworks,Show certifications,Show sub-processors,Show announcementsandShow FAQ. -
The managed lists:
Certifications,Sub-processors,Announcements,FAQandPublic policy texts. -
The settings for documents shared on request:
Document access,Auto-approval domainsandReminders and escalation. -
NDA template, with the versions of your non-disclosure agreement. -
Last, an
Access requestscard withOpen access requests, shown only to roles that can edit the Trust Center.
The top bar and sidebar around the page are the same as on every screen:
- The "?" button in the top bar opens the help panel, with short topics for the screen you are on and a search.
- The book button next to it opens this User Guide inside Aegis, at the chapter for the screen you were on.
- Your name sits towards the right of the top bar. Check it before you edit: a Contributor or Viewer account loads this screen read-only, and a Manager cannot publish.
-
Compliancein the left sidebar holdsPoliciesand the framework work, which feed theShow policiesandShow frameworkssections of the public page. -
Administrationis where this screen lives. Expand it and chooseTrust Center; the configuration loads in its saved state. On a tenant that has never published, that means the master toggle off, an empty slug, and the six section toggles on but dimmed.
Publishing for the first time
Work down the page — address and branding, then wording, then sections — and turn it on last.
-
In
Branding, type aPublic slug. This becomes the public address,/{slug}. Use 3 to 63 characters of lowercase letters, digits and single hyphens, starting and ending with a letter or digit. Paths Aegis already uses —policies,settings,gdpr— are refused as reserved. Stay inside that shape: the save accepts a slightly wider one than the public reader does, so a slug outside it saves cleanly and then returns "not found" to visitors. -
Fill in
Company name; it becomes the large heading on the public page. ACompany logo URLmust beginhttps://— anhttp://address is rejected with "Logo URL must use https://". SetBrand colorfrom the swatch or by typing a hex value; it colours the thick rule under the header band.Company name,Header textandFooter textare plain text: a value with HTML tags or other markup is refused on save with "Use plain text only: remove the HTML tags or other markup." under the field. -
In
Page content, write theHeader textthat greets visitors. It appears under the company name and theTrust Centerline, and doubles as the page description shown when the link is shared, so keep it to a couple of plain sentences. -
Scroll back up and turn on the master
Trust Centertoggle. Nothing is published yet, but the amber notice disappears and the six section toggles below become active. -
Set each of the six section toggles to match what you are willing to
publish. All six start on —
Show sub-processorsincluded — so review that one before you go live. -
Select
Save Changes. "Trust Center settings saved" confirms it, the change is recorded in the audit log as a settings update, and only now does the address resolve.View public pageandCopy public URLalready showed in the header once the toggle was on and the slug filled in, but the address answers "not found" until you save. Open the page in a private window to see it as a visitor does.
The master toggle is the only gate between your settings and the live page. To check your work, enable it, save, look at the page, then switch it off again if you are not ready. Switching off keeps every field, toggle and list entry, so re-enabling restores the page as it was.
What each section publishes
Each "Show" toggle maps to one block, built from live records when a visitor
loads the page. Above the blocks sits a row of four counts, and at the foot, the
time the published data last changed. Each count belongs to one section:
switching a section off removes its count from the page rather than showing 0.
If no section has anything to show, the page reads
Nothing has been published on this Trust Center yet.
| Toggle | What a visitor sees |
|---|---|
Show policies |
Approved policy titles with an effective date, a version badge, the
frameworks each one covers and, when you have written one, its
public summary. Each title opens the policy's own page. Six rows
show first, with Show all for the rest, and
Filter by framework narrows the list. Drafts and
policies in review never appear, and body text is never published.
Maintained in Policies.
|
Show frameworks |
Each enabled framework with one bar split into three bands, each
with its percentage as text: Evidenced (controls marked
Compliant that have at least one linked evidence item that is not
deleted and not past its valid-until date),
Self-assessed only (marked Compliant, no current
evidence linked) and Not implemented (every other
status, even with evidence linked). The headline number is the
evidenced share. Percentages are rounded to whole numbers, so a
small band can show 0% while a few controls are in it. None of this
is an audit result. Control names, statuses and evidence stay
private. Maintained in
Compliance frameworks;
attach and renew evidence in Evidence to
move controls into the evidenced band. Each framework name opens the
framework's own page.
|
Show certifications |
A card for each entry in the Certifications list
further down this screen, in the order you arrange them, and only
those ticked as visible: name, issuing body, issue and expiry date,
and View certificate when it has a document link.
|
Show sub-processors |
The Sub-processors list as a table of
Name, Purpose, Location and
DPA status, again only those ticked as visible. An
empty field shows as a dash, and the DPA column is dropped on narrow
screens. Six rows show first, with Show all.
|
Show announcements |
The visible announcements whose publish date has passed, newest first, at the top of the page, each with its date, title and text. |
Show FAQ |
The visible questions at the foot of the page, in your order. A visitor selects a question to open its answer. |
If a section is on but has nothing to show, the block is left out of the public page rather than published empty.
To see what visitors get without opening the public page, look at the
What the public page shows now card on this screen. It appears once
the Trust Center is switched on and covers four sections — policies, frameworks,
certifications and sub-processors — each with
Hidden from the public page, the number listed, or why nothing is
listed: for example, that policies appear only once they are approved, or that
no frameworks are enabled in your licence. An empty section shows its reason in
amber. Announcements and FAQ are not counted there. The card reflects the saved
settings and the current data, so save first.
Adding a certification
The Certifications card near the foot of the screen is a small
editor of its own. Before you add anything it reads "No certifications yet. Add
one below."
-
Use the
Add certificationform at the bottom of the card.Nameis the only required field, marked with an asterisk; selectingAddwithout it shows "Name is required". -
Add the
Issuing body, aCertificate dateand anExpiry datefrom the date pickers, and aDocument URLif the certificate is hosted somewhere public. An expiry date before the certificate date is refused with "Expiry date must be after the certificate date". -
If the certificate attests one framework, choose it in
Framework attested. The certificate then also shows on that framework's public page and on the page of every policy that covers the framework. -
Leave
Visible on public pageticked to publish the entry, or clear it to keep the record while hiding it — a hidden entry is markedHiddenin the list. For your own certificate that should never be public, tickOwn certificate, track privately (never public)instead: the entry is markedPrivate, never appears on the public page, and its expiry date feeds the certification timeline on a framework hub such as Healthcare (NEN 7510), matched on the framework name in the certificate'sName. -
Select
Add. "Certification added" confirms it and the entry appears in the list above, live on the next public page load: this list saves on its own and does not wait forSave Changes. -
Use the up and down arrows to change the order visitors see,
Editto correct an entry, orDeleteto remove it. Delete asks you to confirm first.
Listing sub-processors
The Sub-processors card works the same way, and an unused list
reads "No sub-processors yet. Add one below." A published sub-processor list is
a common contractual commitment, so keep it current.
-
In the
Add sub-processorform, enter theName(required), theLocationwhere processing happens, and thePurpose. -
Enter the
DPA status— free text, so write what is true, such assigned,pendingorSCCs. -
Set
Visible on public pageand selectAdd. The entry joins the list and the public table, and the arrows reorder it.
The sub-processors published on the Trust Center are the entries you type on this screen. Adding a processor in Vendors does not add it here, and retiring one there does not remove it. When your vendor arrangements change, update this list too.
Announcements and FAQ
The Announcements and FAQ cards follow the
sub-processors. Both work like the lists above: each row saves on its own, the
arrows reorder it, and clearing Visible on public page keeps a row
without publishing it. Each card has an Add announcement or
Add question form at its foot; an unused list reads "No
announcements yet." or "No questions yet." The text is plain: links and markup
are refused, and the message names the field that was refused. You write it
once, in one language; the headings and buttons around it follow each visitor's
language.
-
For an announcement, enter the
Title(up to 200 characters), theBody(up to 2000) and aPublish date, then selectAdd. Title and body are required. It appears at the top of the public page once that date has passed, so a future date schedules it. -
For a question, enter the
Question(up to 300 characters) and a shortAnswer(up to 1000), then selectAdd. Questions appear in the order of the list.
Public policy texts
The last card, Public policy texts, lists every approved policy
with two optional fields that appear on its public page. Select
Edit on a policy to change them.
-
Public summaryis a plain-text summary of up to 1000 characters, written for visitors. Aegis never fills it from the policy text, and with the field empty the public page shows no summary at all. -
Managed by (team name)takes a team name of up to 120 characters, such asSecurity Office. It is never taken from the policy owner. With the field empty the "Managed by" row is left out. - Select
Save; "Public text saved" confirms it.
Never put internal details, people's names or e-mail addresses in a public summary or team name. Editing these texts needs the Trust Center permission, not the policy permission, so someone who can edit a policy cannot publish text about it.
The framework and policy pages
Each framework name on the public page opens a page for that framework, and each policy title opens a page for that policy. Both start with a breadcrumb back to the home page.
-
The framework page repeats the three evidence bands with their legend, shows
the certificates linked to the framework, and lists the approved policies
that cover it under
Policies covering this framework. A policy is listed when it is linked to at least one of the framework's controls (Link controlon the policy). Each policy shows its version and the clauses it addresses as small chips, such asA.5.1: the control reference and article only, never the control's name. -
The policy page shows the title, version, effective and review date,
"Managed by" and the public summary, then
Linked norms(each framework with its clause chips) and the related certificates. A row without a value is left out.
A framework page returns "not found" when frameworks are hidden or the framework is no longer enabled for you. A policy page returns "not found" when policies are hidden or the policy is no longer approved. On a phone the cards stack in one column and nothing scrolls sideways.
No public page, and nothing the browser downloads for one, contains a policy's text, its owner or anyone's e-mail address, a control's name, description or status, or anything about your evidence. An automated end-to-end test seeds all of these and fails the build if one of them reaches a public page.
Document access requests
Some documents should not be public, but you still want customers to be able to
ask for them. Set such a policy, certificate or report to
On request under Document access on the Trust Center
settings screen. Visitors then see a Request access button next to
it; a Public document shows no button, and a
Hidden one does not appear on the public pages at all. Reports
appear in their own Reports section with their title and summary.
Setting up Document access
The Document access card lists every approved policy, every public
certificate and every report, each with its type, Visibility,
Approver, Reserve approver,
Auto-approval and Public summary. With none of these
yet it reads "No approved policies, public certificates or reports yet."
-
Select
Editon a row. The row opens with its settings. Choose theVisibility:Public,On requestorHidden. Only an Admin can change it; a Manager sees "Only an administrator can change the visibility: it decides what visitors can reach." -
Choose the
Approver. A policy defaults toPolicy owner (default); a certificate or report on request must have one, or the save is refused with "A certificate or report on request needs an approver." -
Choose the
Reserve approver— usually the compliance officer, who receives escalated requests and every request from a webmail address. Every document on request needs one. -
An Admin can switch on
Auto-approve allow-listed domainsfor the document (see below). SelectSave; "Document settings saved." confirms it. -
To offer a report, select
Add reportat the top of the card and enter itsTitle,Public summaryandOwner, thenSave. A policy's summary is not edited here: it comes fromPublic policy texts.
What a requester eventually downloads differs by type. A policy is served as a PDF rendered from its last approved version, never a draft. A certificate or report is served from an uploaded PDF, which is virus-scanned and stored encrypted; a file is offered only after a clean scan. The settings screen has no upload control for that file in this release — ask your administrator or Euraika support how files are uploaded for your tenant.
The NDA template
Approved documents are released only after the requester accepts your
non-disclosure agreement, so publish one before you put anything on request: a
person cannot approve a request, and auto-approval does not apply, while no NDA
is published. The NDA template card holds the versions. Every role
can read them; a Contributor or Viewer cannot change them.
-
With no NDA yet the card reads "No NDA yet. Create a draft to write the
first version." Select
Create draft; a draft version opens with starter text. -
Write the agreement in
NDA text, in plain text or Markdown. HTML markup is refused, and so are links in angle brackets — write a web address as plain text. APreviewshows the result and a counter shows the length. -
Select
Save draft("NDA draft saved."), thenPublish. Only an Admin can publish; a Manager can write and save the draft.Publishstays unavailable while the draft has unsaved changes. -
A published version is read-only. To change the wording, select
New version(offered while no draft is open), edit the new draft and publish it. Each version is listed with its status —Draft,PublishedorArchived— and its date.
How a request is handled
Once a document is on request and an NDA is published, a request runs like this:
-
The visitor selects
Request access, ticks every document they need, and fills in first name, last name, work e-mail, company and the reason, then agrees to the privacy text. A personal mailbox such as Gmail is accepted, but the visitor is told it will be reviewed manually, and the request goes to the reserve approver instead of the owner. - Aegis e-mails the visitor a confirmation link, valid for 48 hours. Nobody in your organisation hears of the request until the visitor confirms; an unconfirmed request expires.
- After confirmation, every approver gets one e-mail that lists only their own documents: the policy owner (or the approver set for the document), and for certificates and reports the approver you assigned. The mail shows the requester, company, reason and three checks: whether the e-mail address was confirmed, whether it is a work domain or a personal mailbox, and whether an NDA with this requester is already on file.
-
The
Approve,RejectandView in Aegisbuttons in the mail open the request in Aegis. You decide only there, signed in: a forwarded mail grants nothing. Signed out, the link takes you to sign-in and back to the request. You see only the documents you may decide; chooseApproveorRejectper document, give a reason for a rejection (the requester sees it) and selectSubmit decision. - The requester gets an e-mail with the outcome. For approved documents it carries a link to the non-disclosure agreement: the requester types their name, ticks the box and accepts the published NDA version, and the access becomes active for 12 months.
-
The requester downloads the documents from
My documentson your Trust Center. They enter their work e-mail and receive a sign-in link that works once and expires after 30 minutes. The list shows each document, its current version, the access status (Active,Expires soon,ExpiredorRevoked) and when access ends. Every downloaded PDF carries a watermark with the requester's name, company, e-mail, the date and "CONFIDENTIAL", and every download is logged.
Thirty days before access ends, the requester gets one reminder e-mail. When the term ends the access expires; to keep it, they request the documents again.
No answer is never an approval. When nobody decides, the owner gets a reminder
and, later, the reserve approver (usually the compliance officer) gets the
request. The two moments are set in working days under
Reminders and escalation on the Trust Center settings screen, and
default to 2 working days for the reminder and 3 for the escalation. The
reminder takes 1 to 10 days, the escalation at most 15 and always after the
reminder. Only an Admin can change them. Weekends do not count. Each reminder
and escalation goes out once.
Automatic approval for trusted domains
You can let requests from domains you already trust skip the manual decision.
Under
Auto-approval domains on the Trust Center settings screen, add the
e-mail domains of organisations you work with (for example
partner.com). Free webmail domains such as Gmail cannot be added,
and a domain matches only itself — a sub-domain has to be listed on its own.
Removing a domain asks you to confirm first. Switching this on is an
administrator-only change, like publishing the Trust Center.
Auto-approval is off by default: with no domains listed, every request is
decided by a person. A request is approved automatically only when all of these
hold — the requester used a work e-mail (not a personal mailbox), that domain is
on the list, every document they asked for has
Auto-approve allow-listed domains switched on under
Document access, and a published NDA is in place. The approval then
happens the moment the requester confirms their e-mail: no owner is e-mailed,
the requester goes straight to the NDA, and access becomes active only once they
have signed it — the NDA step is never skipped. The audit trail marks each such
grant AUTO_ALLOWLIST together with the domain that matched, so an
automatic approval is always distinguishable from a person's decision. A request
that does not meet every condition — a personal mailbox, a domain that is not
listed, a document without the toggle — goes to the owner as usual.
The Access requests screen
Select Open access requests at the bottom of the Trust Center
settings screen, or go to /settings/trust-center/access-requests.
You need permission to edit the Trust Center. The list shows
Requester, Documents, Request status,
Requested on and Actions, a page at a time with
Previous and Next. The tabs filter by status:
All, Awaiting confirmation,
Awaiting owner, Escalated,
Approved, awaiting NDA, Active, Rejected,
Expired and Revoked. A rejected request stays listed
under its tab. Per request you can open the detail page, send the approvers a
Remind while it waits for a decision, Revoke granted
access with a reason, and open its Audit trail. Every decision,
reminder, escalation and revocation is in the audit log with who, when and why.
The detail page shows the requester, company, reason and the three checks. If
you are one of several approvers, after you submit it says "Your decision is
recorded. The request stays open until the other approvers have decided." Once
access is granted, each document shows when the NDA was signed and which
version, when access ends (or when and why it was revoked), and the last
download. You can revoke a single document — the requester keeps access to the
others — and open its Download history. Once a requester's details
have been removed, the domain and NDA checks are no longer shown.
The request report
Administrators see an extra Report tab on the Access requests
screen (at /settings/trust-center/access-requests/report). It shows
aggregate figures over a date range you choose, defaulting to the last 90 days:
the number of requests and how they are split by status, the median and
90th-percentile time from e-mail confirmation to the last decision, the share of
confirmed requests that were escalated, the share of decided requests that the
allow-list approved automatically, the requests per week, and the most requested
documents. The report is for administrators only and never shows requester
details — no name, e-mail or company, only counts, rates, timings and document
titles. Managers and other roles can read and decide requests but do not see the
report.
The public pages, the request dialog and the confirmation and NDA pages never show who decides: no owner, approver or reserve e-mail address and no name. The requester's details are removed 90 days after a request is rejected, expires or is revoked; the request and its decision record stay.
Day-to-day changes
-
To take the page offline, turn the master
Trust Centertoggle off and selectSave Changes. The public address returns "not found" straight away and your settings are kept. -
To hand the address to a customer or an auditor, use
Copy public URLin the header. It copies the full web address and confirms with "Public URL copied". -
After a certification renewal, edit the entry in the
Certificationslist and refresh theHeader textif it quotes a date. Both reach visitors on the next page load.
The slug is the public address. Change it after sharing the page and every existing link and bookmark stops working. It must also be unique: saving one already in use is refused with "That URL slug is already in use. Choose another.". Settle on it before you publish.
Tips and limits
-
Footer textis shown at the bottom of the public page, directly above the "Powered by Aegis" line. It is printed as plain text with your line breaks kept; links and formatting are not applied. Leave the box empty and nothing is shown. It suits a data protection contact or a scope note. - The public pages are rate-limited per network. A visitor who loads them too often sees "Too many requests" with a request to wait a minute and reload, rather than a "not found" page.
- Certifications are free text, so you can list any attestation you genuinely hold — but that does not mean Aegis tracks the scheme as a framework. SOC 2, for example, is a roadmap item rather than shipped, so a SOC 2 entry publishes as a certification card and nothing more.
- The timestamp at the foot of the public page is the time the published data last changed, not the time of the visit. A custom domain, or keeping the page out of search results, is a matter for Euraika support rather than a setting here.
- Every save is written to the audit log as a settings update, so you can show an auditor when the published posture last changed. See The audit log.
- A Trust Center shows your posture at a point in time. It does not make you compliant, and it is only as accurate as the records behind it — review it on a schedule, not only when a customer asks.
Where this connects
The policy and framework sections draw on Policies and Compliance frameworks. The sub-processor list should agree with Vendors and the processing records in GDPR; certificates you hold as files belong in Evidence. Other administration screens are covered in Settings, and who may edit what is set out in What each role can do.