Compliance frameworks
The Compliance area puts every framework your organisation answers to on one screen, then lets you open any single control to see what still stands between it and coverage.
A framework is a published set of requirements you measure yourself against, such as DORA, GDPR or ISO 22301. Each framework breaks into controls. You link policies, procedures, risks and evidence (the proof a control works) to those controls, and Aegis reads only those links. One rule decides the headline number: a control counts as covered when at least one linked evidence item is approved and still inside its valid-until date. A control with only a policy, a procedure or a risk linked is partial, not covered. Coverage records that approved, current evidence is present; Aegis does not judge whether that evidence's content actually meets the requirement. That judgement stays with your reviewers and your auditor.
Who uses it
- Viewer reads the overview, every control and the DORA and EU AI Act pages, and can export. The AI buttons are not shown to a Viewer.
- Contributor also sees the AI buttons on the overview, DORA and EU AI Act pages and can configure the DORA profile, but cannot change a control or request an AI implementation proposal for one. The overview, the mandatory clause, DORA and EU AI Act screenshots were taken as a Contributor; the Statement of Applicability decision as a Manager; the framework page and its export as an Admin.
- Manager and Admin can change controls: the implementation status, the Statement of Applicability decision, parameters, requirements and AI proposals.
- Frameworks such as DORA, the EU AI Act and NEN 7510 are pay-per-framework. Without that framework's licence, its page shows a short "not available" notice instead.
What's on this screen
Open Control Measures (under Compliance) in the left menu to reach
/compliance. This is the controls list; typing
/controls also lands here. The header reads
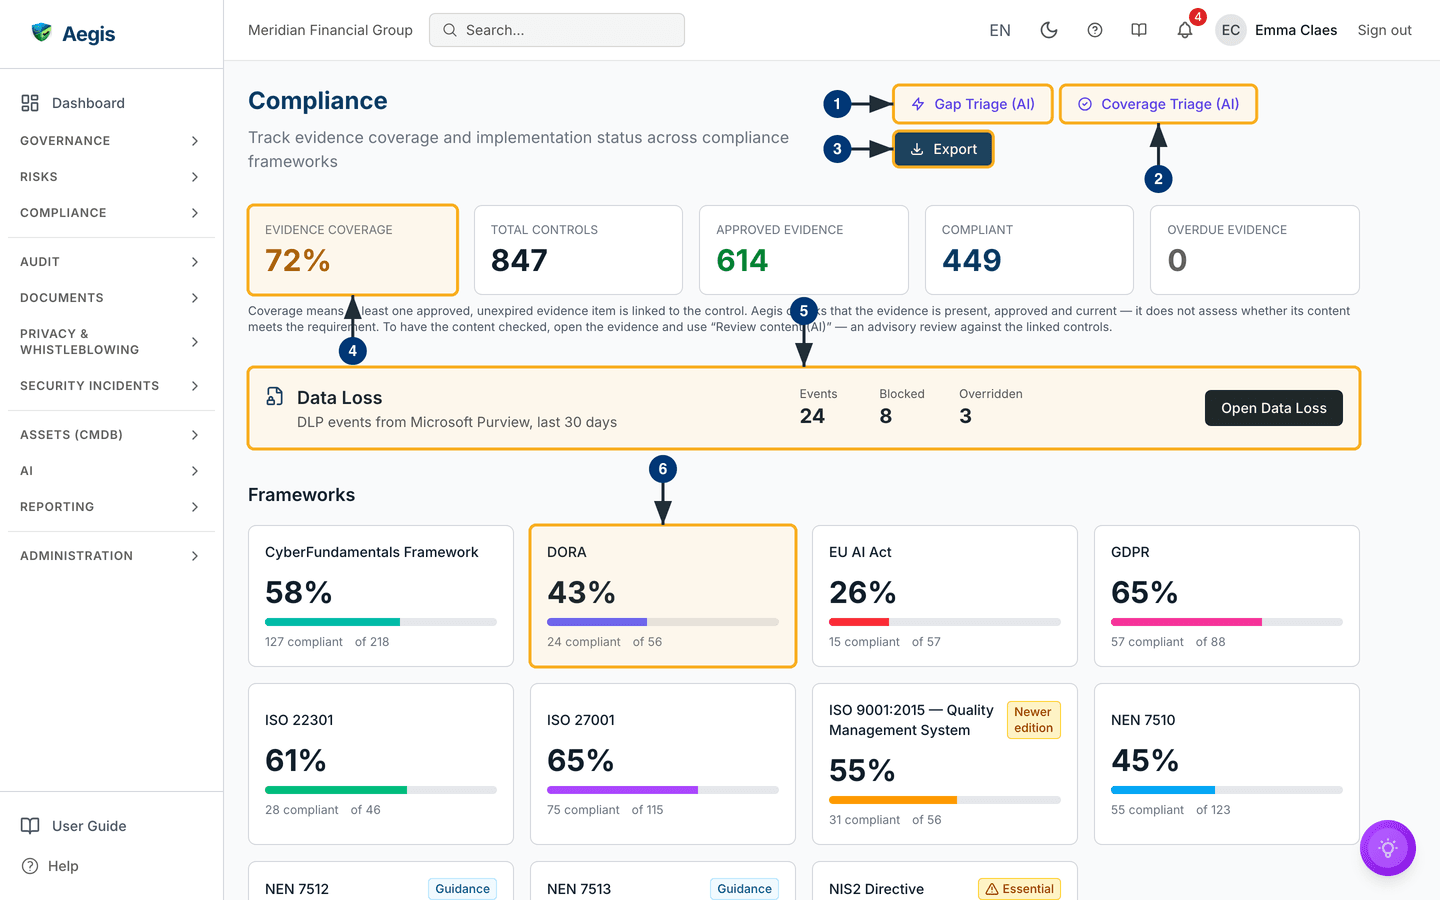
Compliance above the line "Track evidence coverage and
implementation status across compliance frameworks". Three buttons sit on the
right: Gap Triage (AI), Coverage Triage (AI) and the
dark Export button.
Below the header are five figures: Evidence Coverage,
Total Controls, Approved Evidence,
Compliant and Overdue Evidence. They count only
frameworks that are both enabled and applicable. The captured screen shows 72%
coverage across 847 controls, with 449 of them Compliant and none
overdue. Coverage shows green from 80%, yellow from 60% and orange below. A note
under the figures repeats how coverage is computed: at least one approved,
unexpired evidence item is linked, and the content of that evidence is not
assessed. It also points you to Review content (AI) on an evidence
item when you want that content checked, as an advisory review.
Next comes the Data Loss card: Events,
Blocked and Overridden counts for DLP (data loss
prevention) events from Microsoft Purview over the last 30 days, with an
Open Data Loss button. The card appears only when the Data Loss
module is switched on, your licence includes it and your role may read it;
otherwise the page goes straight to the frameworks.
Under Frameworks is an alphabetical grid of cards, four to a row.
Each gives the framework name, its percentage, a progress bar and a line such as
"24 compliant of 56". Three badges can appear on a card. A yellow
Newer edition badge (on ISO 9001:2015 in the capture) means the
publisher has superseded the edition Aegis ships; hover over it to see which
edition. A blue Guidance badge (on NEN 7512 and NEN 7513 in the
capture) marks implementation guidance that is not certifiable on its own; hover
to see the standard you certify against. The NIS2 card shows your entity class,
such as Essential, taken from your organisation profile. A
framework your organisation profile marks as not applicable stays on the grid
with a dashed border, a Not applicable to your organization label
and — in place of a percentage. A framework that is switched off
reads Disabled.
Below the captured area come Control Requirements (the filterable
controls table), Saved AI insights and Action items.
Working from the overview
-
Select
Gap Triage (AI). TheControl Gap Smart Triagewindow opens and waits forRun Gap Triage. It ranks open gaps into a 90-day sprint and a 12-month horizon. -
Select
Coverage Triage (AI). Its window looks at controls with nothing linked at all and suggests where to start. -
Select
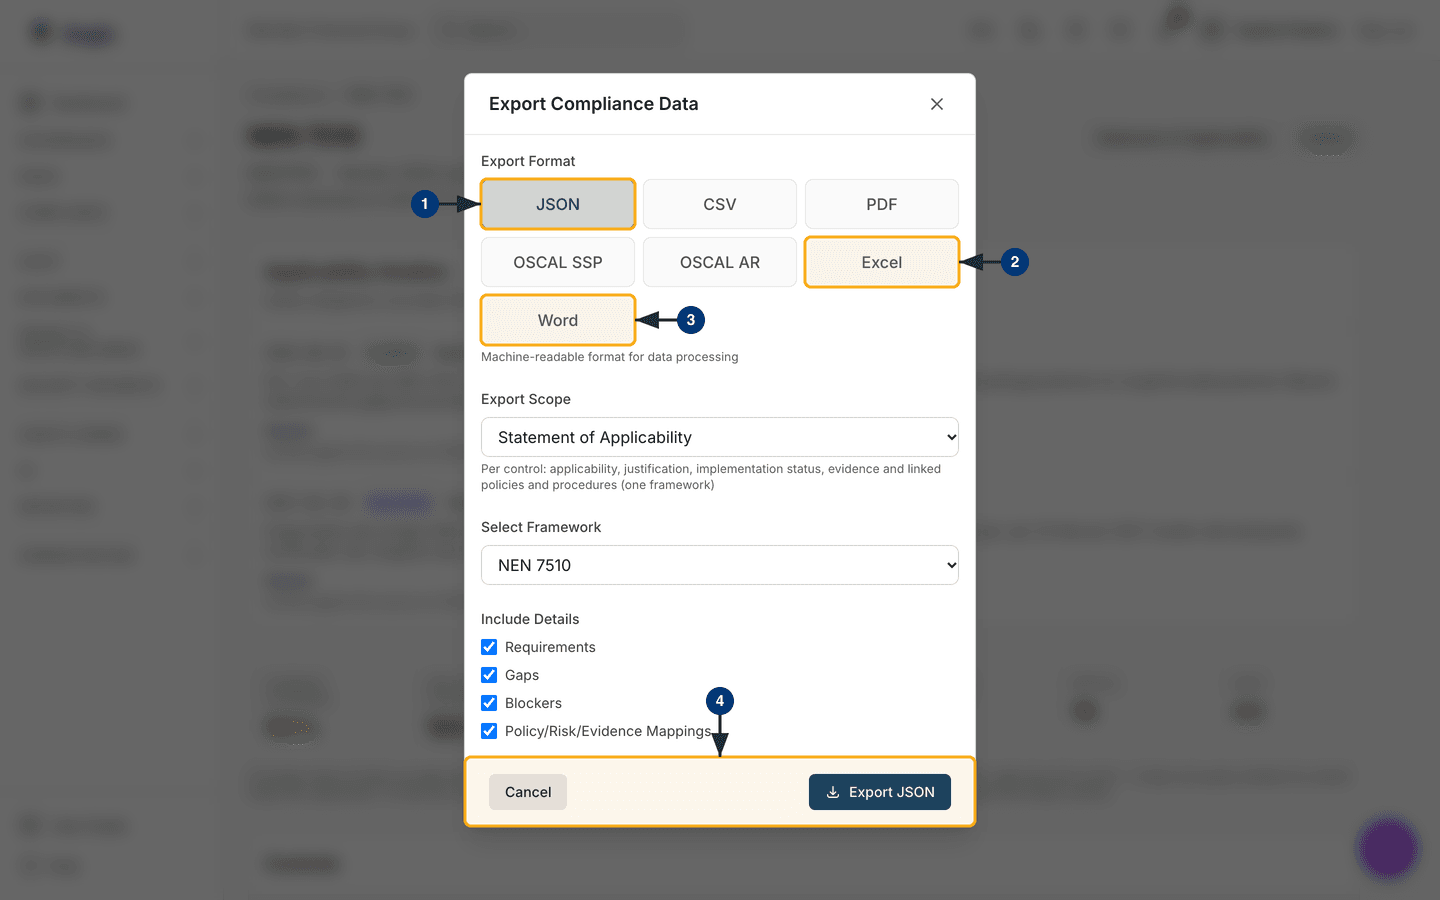
Export. TheExport Compliance Datawindow asks for a format (JSON,CSV,PDF,OSCAL SSPorOSCAL AR) and a scope (Executive Summary,All Frameworks,Single FrameworkorStatement of Applicability). Confirm, and the file downloads. The Statement of Applicability also has its own button on the framework page, described below. -
Read
Evidence Coverage: the share of controls with approved, current evidence.Compliant, by contrast, counts controls whose own status isCompliant. -
Where the
Data Losscard is shown, selectOpen Data Loss. The Data Loss module opens at/compliance/data-losswith the events behind the three counts. -
Select a card, for example
DORA. The card gains a highlighted border, the heading changes toFrameworks (click to clear filter), and the controls table below shows only DORA controls. Select the card again to clear the filter.
Opening a control
Scroll to Control Requirements, narrow the table with the search
box and filters, then select a row. A window opens, headed with the control's
reference and title, with the framework and a status badge beneath. Its
Applicability panel records the
Statement of Applicability (SoA: the
per-control record of whether and how a control applies to you) decision. A
Manager or Admin can change it; for a Contributor or Viewer the options are
read-only and there is no save button.
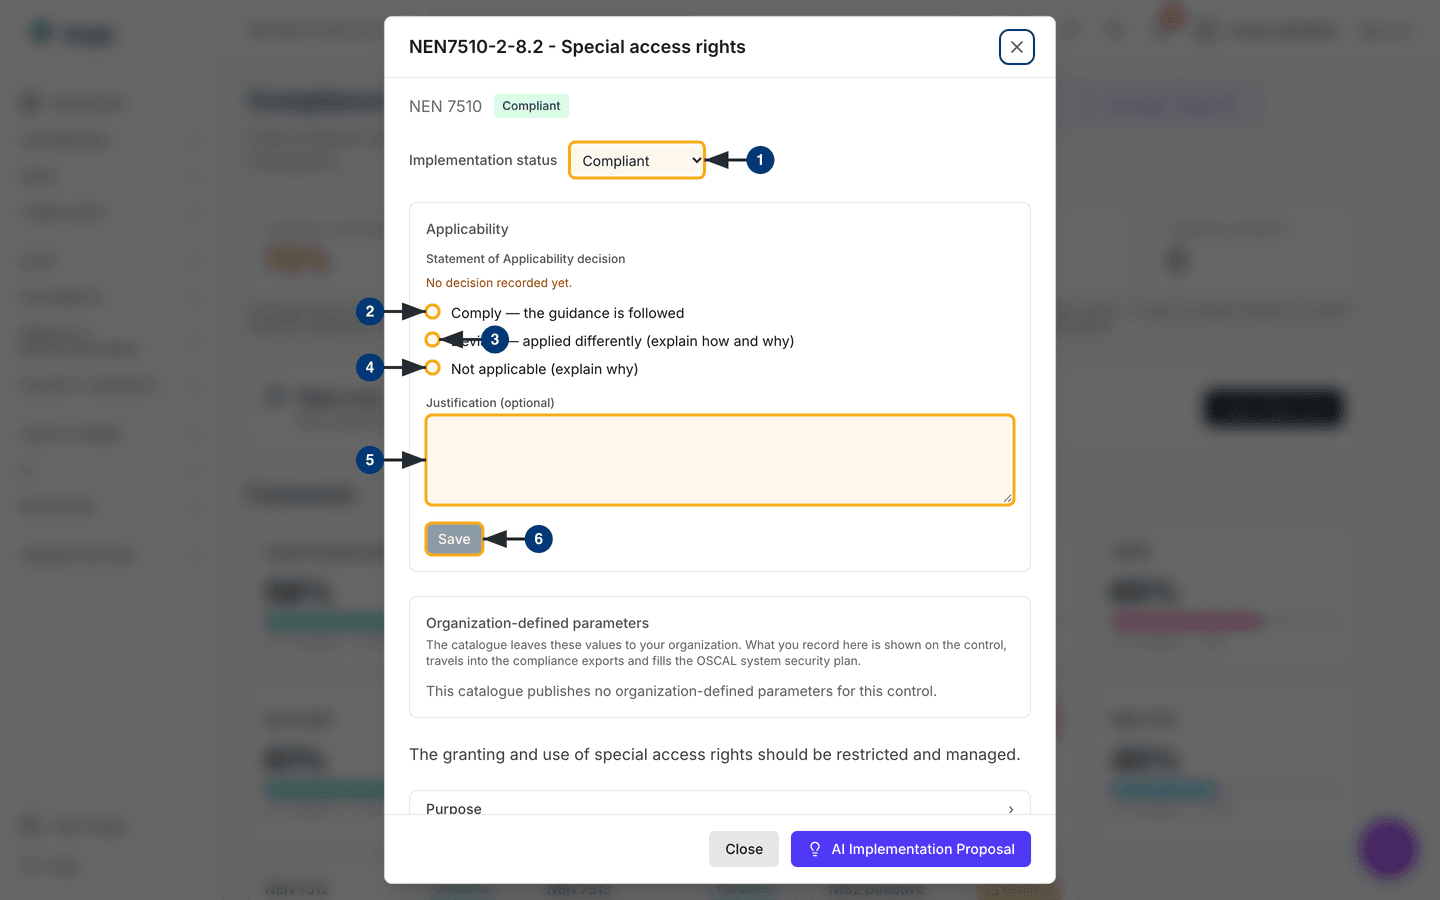
The first capture shows NEN 7510-2 8.2, Special access rights,
opened as a Manager. Below the panels sit the control's text and, where the
catalogue publishes them, collapsed Purpose,
Guidance and Other information sections you can
expand. The footer holds Close and, for a Manager or Admin,
AI Implementation Proposal; a Contributor sees only
Close.
-
Set
Implementation status. Only a Manager or Admin sees this list. PickNot Started,In Progress,CompliantorNon-Compliant, and the status badge above updates.Compliantis greyed out while something stands in its way, with the reason beside the list: unresolved gaps, incomplete requirements, no linked evidence, only expired evidence, or evidence still awaiting its four-eyes approval. While a control is not applicable, its status is frozen. -
Under
Statement of Applicability decision, which readsNo decision recorded yet.until someone saves one, chooseComply — the guidance is followedwhen you apply the control as the framework describes it. A justification is optional. -
Choose
Deviate — applied differently (explain how and why)when you meet the aim another way. NEN 7510 works on comply-or-explain, so the explanation is required: the field label turns toJustification (required)and saving waits until you have written one. -
Choose
Not applicable (explain why)to take the control out of coverage. It also needs a justification. - Write the reasoning in the justification field.
-
Select
Save. It is greyed out until something has changed. The decision, who made it and when then travel into the Statement of Applicability export.
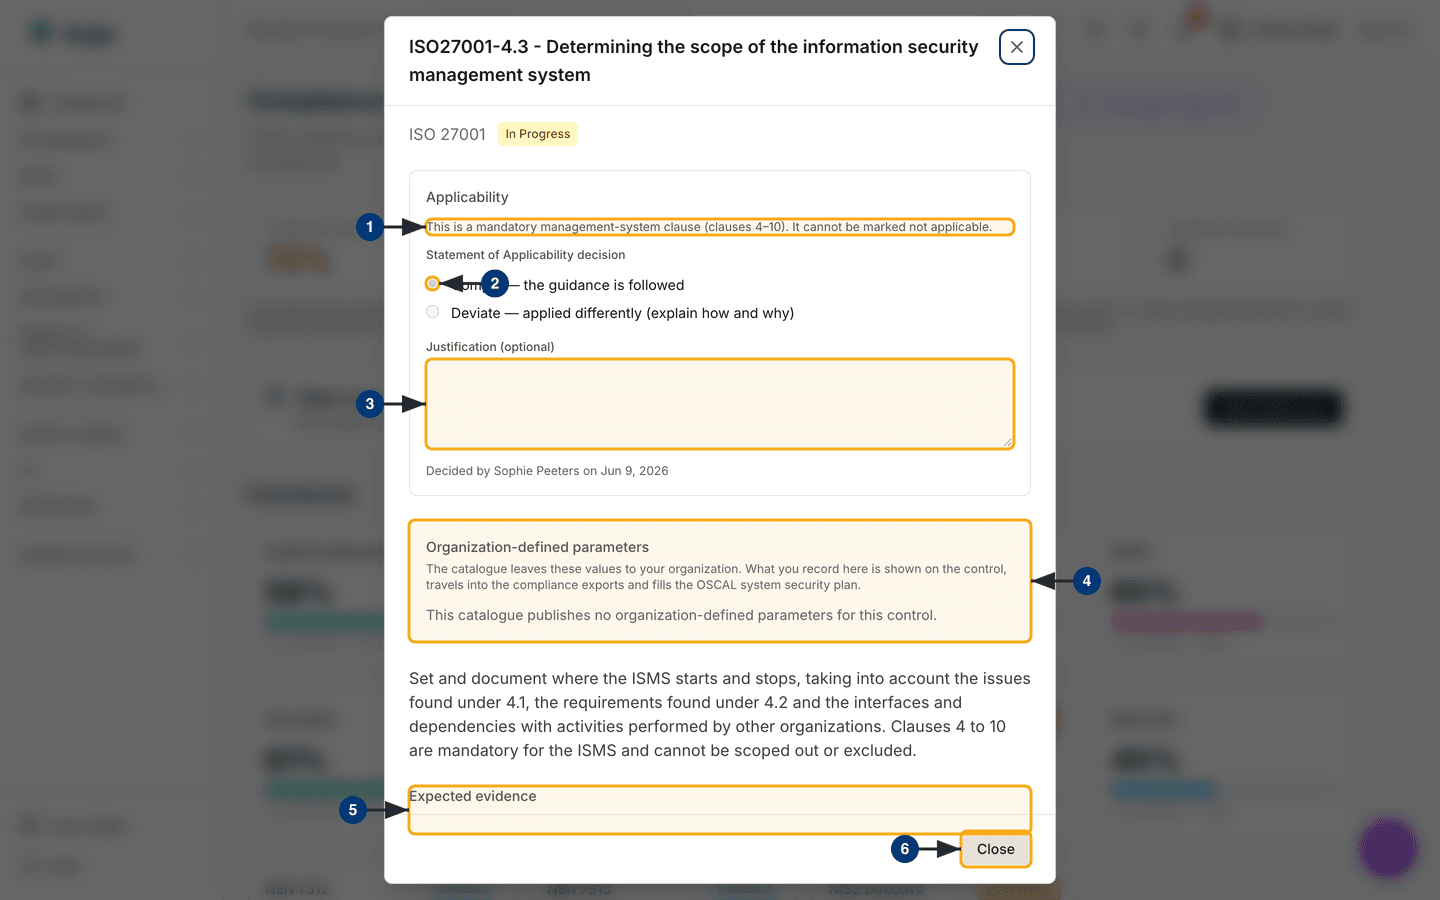
Some controls can never be excluded. ISO management-system clauses 4 to 10 are
mandatory, and so are CyFun key measures; for those the panel offers only
Comply and Deviate. The second capture shows ISO 27001
clause 4.3 as a Contributor, so the Implementation status list is
absent and only the In Progress badge shows the status.
- Read the note: “This is a mandatory management-system clause (clauses 4–10). It cannot be marked not applicable.”
-
Under
Statement of Applicability decisiononly the comply and deviate options appear, read-only for a Contributor. Once a decision is saved, the panel names who made it and when; the captured screen reads "Decided by Sophie Peeters on Jun 9, 2026". -
Justification (optional)is read-only too, so this capture has no save button. -
Check
Organization-defined parameters: values the framework leaves to you, which flow into the exports and the OSCAL system security plan. Here the catalogue defines none. -
Read
Expected evidence, below the control text: what the catalogue says an assessor should see for this control. It appears only where the catalogue publishes it. Further down,Owner groupshows who owns the control, with aNo owner assignedlabel when nobody does yet. -
Select
Close. The window closes and the table row reflects any saved change.
A framework's own page and its Statement of Applicability
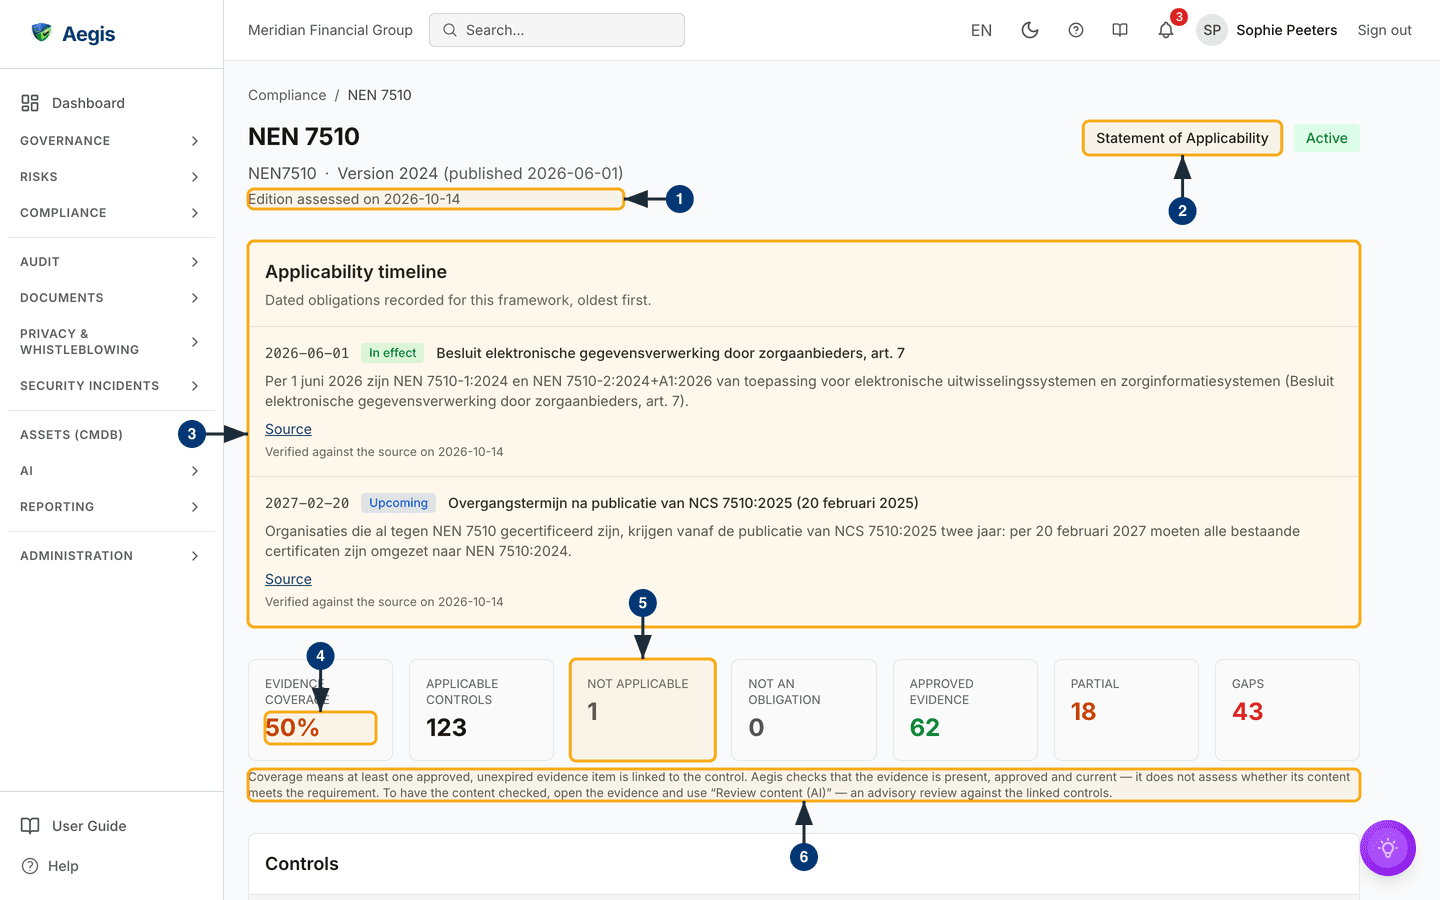
Select a framework card's name, or open
/compliance/<framework>, for example
/compliance/NEN7510. A breadcrumb leads back to
Compliance. The page shows the framework's key, version and
publication date, and an Active badge beside the export button
while the framework is switched on.
- Read the line under the version. It gives the date the framework applies from, where that differs from publication, and the date its edition was last assessed; the captured screen reads "Edition assessed on 2026-10-14".
-
Select
Statement of Applicabilityat the top-right. The export window opens with that scope and this framework already chosen. -
Read the
Applicability timeline, where the framework has one: dated obligations, oldest first, each markedIn effectorUpcoming, with aSourcelink and the date it was last verified against that source. -
Scan the figures:
Evidence coverage,Applicable controls,Not applicable,Not an obligation,Approved evidence,PartialandGaps. -
Not applicablecounts controls you have excluded through the SoA decision.Not an obligationcounts controls the catalogue itself marks as awareness or good practice rather than a requirement. Neither counts towards the coverage percentage. - Read the note under the figures. Coverage means at least one approved, unexpired evidence item is linked; Aegis checks presence and currency, not whether the content meets the requirement.
If any control has overdue evidence, an orange banner under the note counts them
and asks you to renew or replace the expired evidence. The
Controls table follows, with the columns Ref,
Title, Status, Mappings and
Evidence (Yes, Overdue or
No). Further down is a Gaps list of controls with no
policy, risk or evidence mapped at all.
In the export window, check Export Scope and
Select Framework first. Per control, the SoA lists the decision,
justification, implementation status, evidence and the linked policies and
procedures, with who decided and when. Under Include Details, one
box (Policy/Risk/Evidence Mappings) starts ticked. Untick it to
leave the names of the linked policies, procedures and evidence out of the file;
the evidence count stays.
-
Note the format: the window opens on
JSON, and a line under the format grid describes whichever format is selected. -
Choose
Excelfor a branded workbook of the Statement of Applicability. -
Choose
Wordfor the same content as a branded document. Both formats appear only while the scope isStatement of Applicability; pick another scope and the window falls back toJSON. -
Select the export button in the footer, which names the format (for example
Export JSON). The file downloads.Cancelcloses the window without exporting.
An administrator can switch a framework off in
Settings → Frameworks. Its pages then show a card reading “… is
switched off” instead of their content, its API calls are refused and its
reminders stop. The data is kept and returns when the framework is switched
on again. This applies to every framework page, including DORA, the EU AI
Act, ISO 42001, CyFun, ESRS and the NEN 7510 hub. An Admin sees the link
Open Settings → Frameworks on the card. A framework outside
your licence shows a different card, “… Not Available”.
Moving a control forward
This needs Manager rights. Further
down the same control window are Implementation progress, a
Maturity panel where the framework defines a maturity scale, and
the requirements, each with a status of Not Started,
In Progress or Complete.
-
Aegis derives the control's status from its requirements. All requirements
Completeand no open gap givesCompliant; allCompletewith a gap open givesNon-Compliant; anyIn ProgressgivesIn Progress. A Manager can also set the status directly withImplementation status, within the limits described above. -
If the status changes and the control has equivalents elsewhere, a
Sync status across frameworkswindow asks whether to carry it across. You decide. -
AI Implementation Proposalin the footer drafts a plan. Nothing is applied until you apply it.
The DORA page
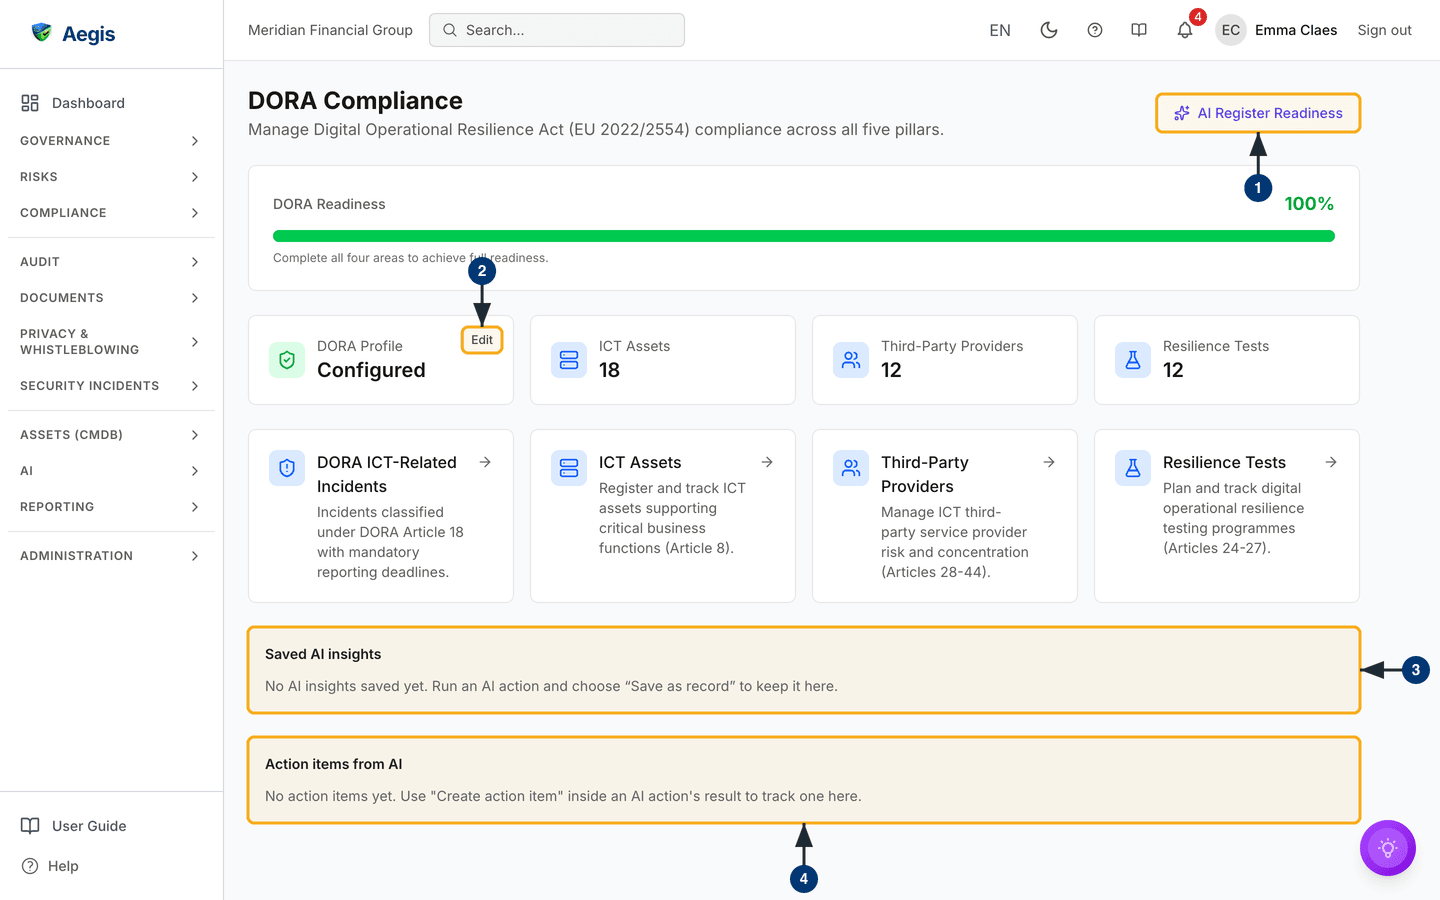
DORA (the EU's Digital Operational Resilience Act) has its own page at
/compliance/dora. A DORA Readiness bar under the
header shows how many of four areas are complete, with the note "Complete all
four areas to achieve full readiness"; the captured screen reads 100%. Four
figure cards follow: DORA Profile (Configured, with
Edit), ICT Assets,
Third-Party Providers and Resilience Tests. Below
them, navigation cards open DORA ICT-Related Incidents (Article
18), ICT Assets (Article 8),
Third-Party Providers (Articles 28–44) and
Resilience Tests (Articles 24–27).
-
Select
AI Register Readiness. Aegis scores your Register of Information against DORA Article 28(3) and lists gaps and next steps. You decide which to act on. -
Select
Editon theDORA Profilecard. The profile window opens; only entity type is required. Save, and the readiness bar updates. With no profile yet, the button readsConfigure. -
Read
Saved AI insights. In the capture it is empty: "No AI insights saved yet. Run an AI action and choose 'Save as record' to keep it here." Once you keep a run, each insight shows the date it was saved and a provenance badge;Show moreexpands the full text,Create action itemturns a recommendation into tracked work, andEditandDeleteamend or remove it. -
Read
Action itemsat the foot of the page. It stays empty until you useCreate action iteminside an AI result.
Saved insights record what was true when the run happened. An insight saved
before you configured the profile or filled the register can still say the
register is incomplete. Run
AI Register Readiness again after you change the register, and
delete insights that no longer apply. A Legacy record badge
means the insight was saved before AI runs were recorded, so its origin
cannot be verified.
The EU AI Act page
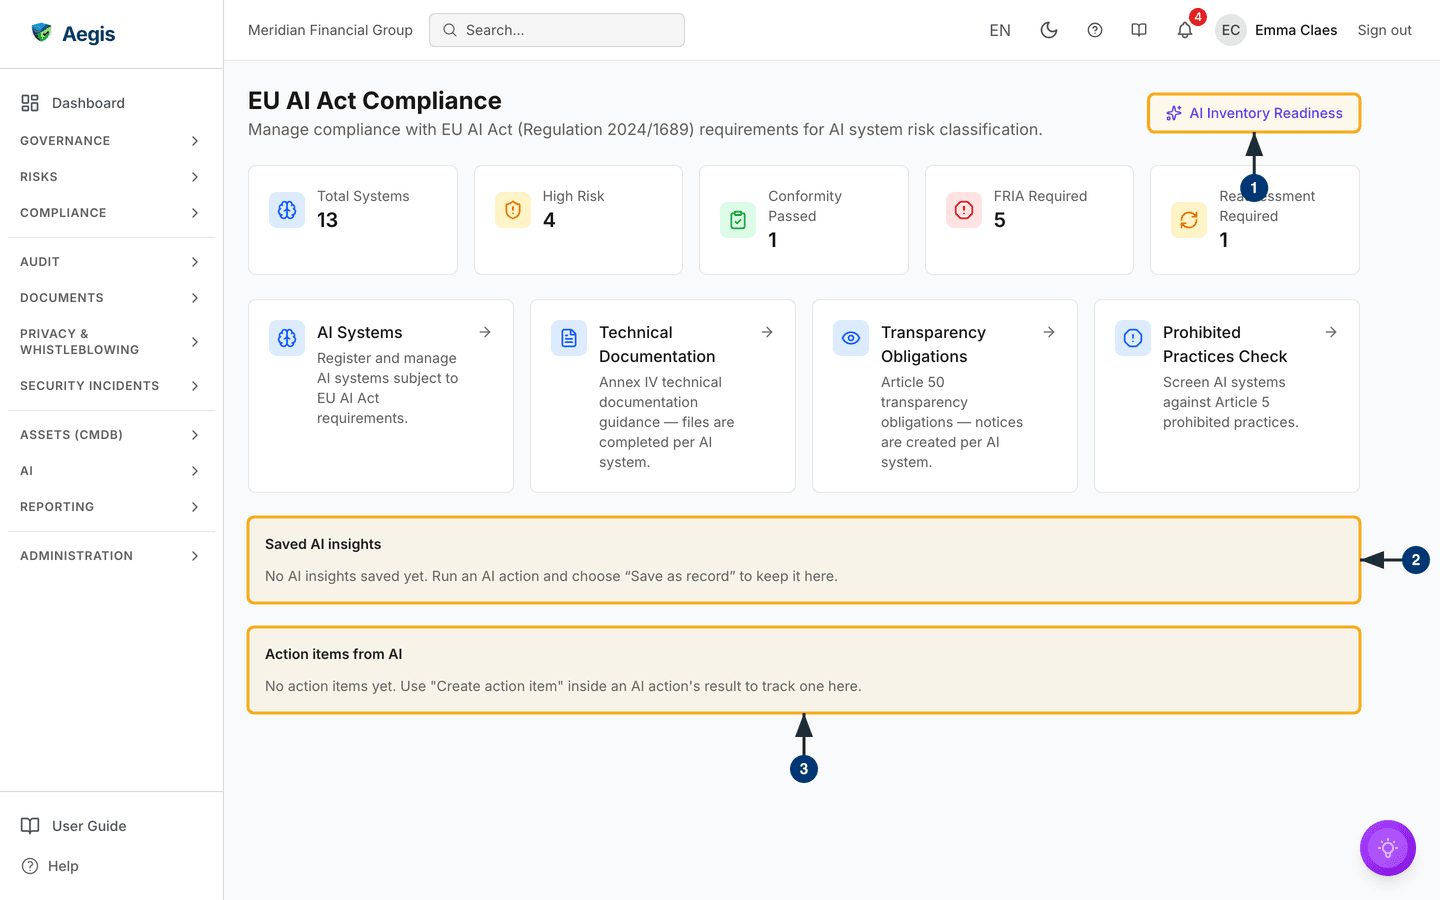
/compliance/eu-ai-act is the entry point for the EU AI Act
(Regulation 2024/1689). Five figures follow the header:
Total Systems, High Risk,
Conformity Passed, FRIA Required (FRIA is a
fundamental-rights impact assessment) and Reassessment Required.
The captured screen shows 13 systems, 4 of them high risk. Four navigation cards
lead to AI Systems, Technical Documentation (Annex
IV), Transparency Obligations (Article 50) and
Prohibited Practices Check (Article 5).
-
Select
AI Inventory Readiness. Aegis scores your registered AI systems on prohibited practices, classification, FRIA, conformity and registration, tying each gap to an article. With an empty inventory it says so and does not invent systems, so register them first throughAI Systems. -
Read
Saved AI insights. Until you keep a run, it says "No AI insights saved yet. Run an AI action and choose 'Save as record' to keep it here." -
Read
Action items. It stays empty until you useCreate action iteminside an AI result, exactly as on the DORA page.
The AI assist
All five AI actions in this area read what is recorded, write a briefing, and
leave the decision to a person. None changes a control, status or mapping by
itself. The gap triage ranking comes from fixed rules, not from AI. Keep any run
with Save as record. Every AI action is logged and uses your
organisation's AI credits. To have an evidence document's content checked
against its controls, use Review content (AI) on the evidence item;
that review is advisory and does not change coverage.
Tips and limits
-
Coverage and status differ. A control can be covered and still read
Not Started. The captured screen shows 72% coverage while 449 of 847 controls areCompliant. -
Covered is not the same as assessed. A control shows
Evidence approvedas soon as one approved, unexpired evidence item is linked — whatever that document says. Open the evidence and check its content before you rely on the figure in an audit. -
Evidence counts towards coverage only once it is approved. An uploaded item
still awaiting review leaves the control partial, and keeps
Compliantout of reach in theImplementation statuslist. -
Overdue Evidencecan rise without anyone touching the system, as valid-until dates pass. Check it regularly. -
A dashed card showing
—means your organisation profile marks that framework as not applicable. Correct the sector or entity type in Settings. -
A
Guidancecatalogue keeps its percentage and its Statement of Applicability, but that SoA documents implementation guidance; certification is against the standard the badge names. - You cannot create custom control sets; the shipped sets follow the published texts.
- The ISO 42001 pages are early. Where the control set has not been seeded, the page shows a placeholder instead of a control list, and the governance screens around it are still being built. SOC 2 is on the roadmap, not shipped, and does not appear in the grid.
- If framework data cannot be loaded, the page still opens, with an amber banner and an empty framework list. Refresh first. If the banner stays, contact support.
Where this connects
Close gaps by linking work from Policies, Procedures and Evidence, and by recording treatment in Risks. Control Mapping, CyFun Maturity and Mock Audit cover the related sub-pages. DORA Compliance, EU AI Act and Healthcare (NEN 7510) go deeper into their framework pages. Data Loss covers the module behind the overview card. Audit readiness turns this picture into a checklist, and the work you take on is tracked in Action items.