What each role can do
Every person who signs in to Aegis holds exactly one of four roles, and that role decides what they can read, change, approve and administer across the whole application.
A role (a named bundle of powers attached to an account) is the most consequential setting on a person's record. Aegis ships with four, and they form a ladder from read-only to full administration. A person holds one role at a time on your tenant (your organisation's own private Aegis instance), and only an Admin can change it.
The four roles
From the bottom of the ladder to the top: Viewer < Contributor < Manager < Admin.
- Viewer — the observer: auditors and executive sponsors. Reads policies, risks, evidence, framework progress and board reports, and can export a report. Creates nothing.
- Contributor — the day-to-day worker: drafts policies and procedures, creates and scores risks, uploads evidence, logs incidents and responds to data-subject requests. Cannot approve anything, and cannot delete policies, risks, vendors, incidents or evidence.
- Manager — the functional owner: everything a Contributor does, plus approving policies and procedures, deleting records (evidence excepted — that stays with an Admin), configuring connectors, handling whistleblowing cases, editing the public Trust Center and using the regulatory reporting view.
- Admin — the workspace administrator: everything a Manager does, plus users and roles, the licence, single sign-on, API keys, webhooks and the auto-incident rules. Internally an Admin holds a wildcard grant, which is why no administrative screen is ever hidden from one.
In the normal configuration Aegis is invitation-only: there is no self-registration, so every new person starts from an Admin's invitation.
Which role fits my job title?
The four role names describe powers, not jobs, so people reasonably ask which one they should hold. The table below maps common job titles to the role that usually fits, and to what to ask your Admin for when you request an account. It is a starting point, not a rule — your organisation decides, and a person's real duties matter more than their title.
| Your job | Typical Aegis role | What to ask your Admin for |
|---|---|---|
| Ordinary employee (no compliance duties) | Viewer, or often no account at all | An account only if you must acknowledge policies in Aegis — see the employee scenario |
| HR officer | Contributor | Access to the HR register and training records; Manager instead if you will log data-subject requests yourself — see the HR scenario |
| Office manager | Contributor | Create rights for the records you keep — vendors, evidence, incidents |
| Quality manager | Manager | Approval rights for policies and procedures, and audit access |
| Compliance officer / CISO | Manager | The full working set: approve, delete, connectors, whistleblowing cases |
| DPO / privacy lead | Manager | The GDPR area, including creating and closing data-subject requests |
| Director / board member | Viewer | Read access and report export — board packs and dashboards are readable as-is |
| IT administrator | Admin | Users and roles, single sign-on, API keys, webhooks and system settings |
| External auditor | Viewer | A time-limited account for reading evidence, exports and the audit trail |
What's on this screen
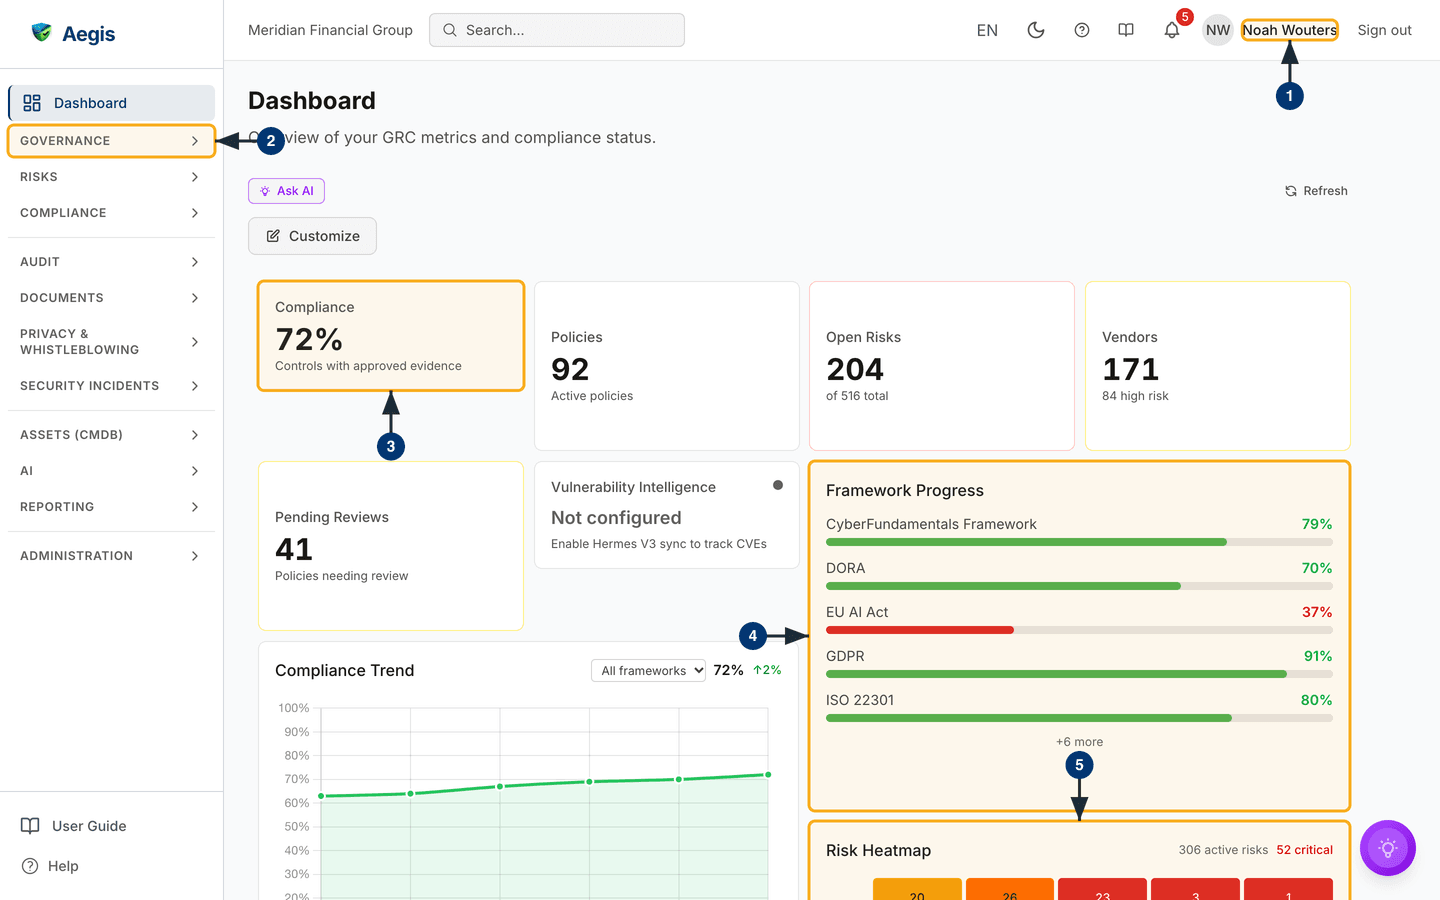
The quickest way to understand a role is to sit in front of the screen as that
role. The figure below is /dashboard signed in as a Viewer — on the
captured screen, Noah Wouters, whose name sits top-right beside
Sign out. The top bar also carries your organisation's name, the
global search box, the EN language switch, the theme toggle, the
help icon, the user-guide icon and the notification bell. Down the left runs the
grouped sidebar, with User Guide and Help at its foot.
Across the top of the content sit Ask AI,
Customize and Refresh, then the headline cards —
Compliance, Policies, Open Risks,
Vendors, Pending Reviews and
Vulnerability Intelligence — followed by
Framework Progress, Compliance Trend and
Risk Heatmap (see The dashboard for
the full page). What the role changes is mostly not the layout but which
controls are offered and which accept a change — and, one level down in the
sidebar, which entries appear at all.
Two dashboard controls a Contributor sees are missing here.
What needs my attention? and the small ? that explains
each headline number are AI actions, and a Viewer does not hold
ai:execute (the right to run a billable AI action), so Aegis hides
them rather than offer a button the server would refuse. Ask AI,
the assistant's chat, stays available. A Getting Started banner
also appears above the toolbar while your tenant's setup checklist is incomplete
and nobody has dismissed it; on the captured tenant it does not show.
- Check who you are signed in as, top-right. The role behind that name is what every permission check reads, on every request.
-
Open the sidebar groups —
Governance,Risks,Compliance,Audit,Documents,Privacy & Whistleblowing,Security Incidents,Assets (CMDB),AI,ReportingandAdministration. Every group heading renders for a Viewer; the filtering happens one level down, where role-gated entries such asRisk Appetite,AI Dashboard,ConnectorsandAPI Keysare dropped from the list. -
Read the headline cards — on the captured screen
Compliancereads72%,Policies92active andOpen Risks204of516. Each figure is computed live from the records a Viewer can read, and each card is a shortcut into its module, which opens read-only for a Viewer. SelectCustomizeto rearrange the cards: the layout is saved as your own preference, so even a Viewer can change it without touching anyone else's dashboard. -
Read
Framework Progress, one bar per framework your tenant tracks with its percentage, and a+N moreline when there are more frameworks than the card shows (+6 moreon the captured screen). -
Select a cell in the
Risk Heatmap. It opens the risk register filtered to the open risks with that likelihood and impact, read-only for a Viewer.
The same list, one role apart
The read-only pattern repeats on every module. Here is the
Policies list as the same Viewer. Where a
Contributor sees a Create Policy button and the
Review Triage (AI) button, the Viewer's header offers only the
List / Grouped view toggle. Below that sits a full
reading surface: the All Statuses, All Levels and
All AI analyses filters, a Search policies… box with
its Search button, and a table of Title,
Status, Level, Owner,
Version, Controls, Effective Date,
Review Date, AI analysis, Updated and
Actions.
-
Switch between
ListandGroupedto see a flat table or policies clustered by level. The missing create button beside this toggle is the first visible difference from a Contributor's screen. -
Narrow the table with
All Levels(andAll Statusesto its left). The list reloads against the chosen filter; filtering is a reading aid and is open to every role. -
Use
All AI analysesand pickAI analysis: queued or runningto show only policies whose AI analysis is still in progress. A Viewer can see the state of an analysis in theAI analysiscolumn but cannot start one. -
Type a title into
Search policies…and selectSearch. The table reloads with the matches — search changes what you see, never the records. -
Tick a row's checkbox. A bulk-action bar appears, and for a Viewer it offers
only
Export, because the Viewer holdsreport:exportbut neitherpolicy:update(needed forChange Status) norpolicy:delete. - Select the eye icon to open the policy read-only. It is the only row action a Viewer has: the pencil a Contributor sees beside it is not rendered at all, so the Viewer is never sent to an editor they could not save.
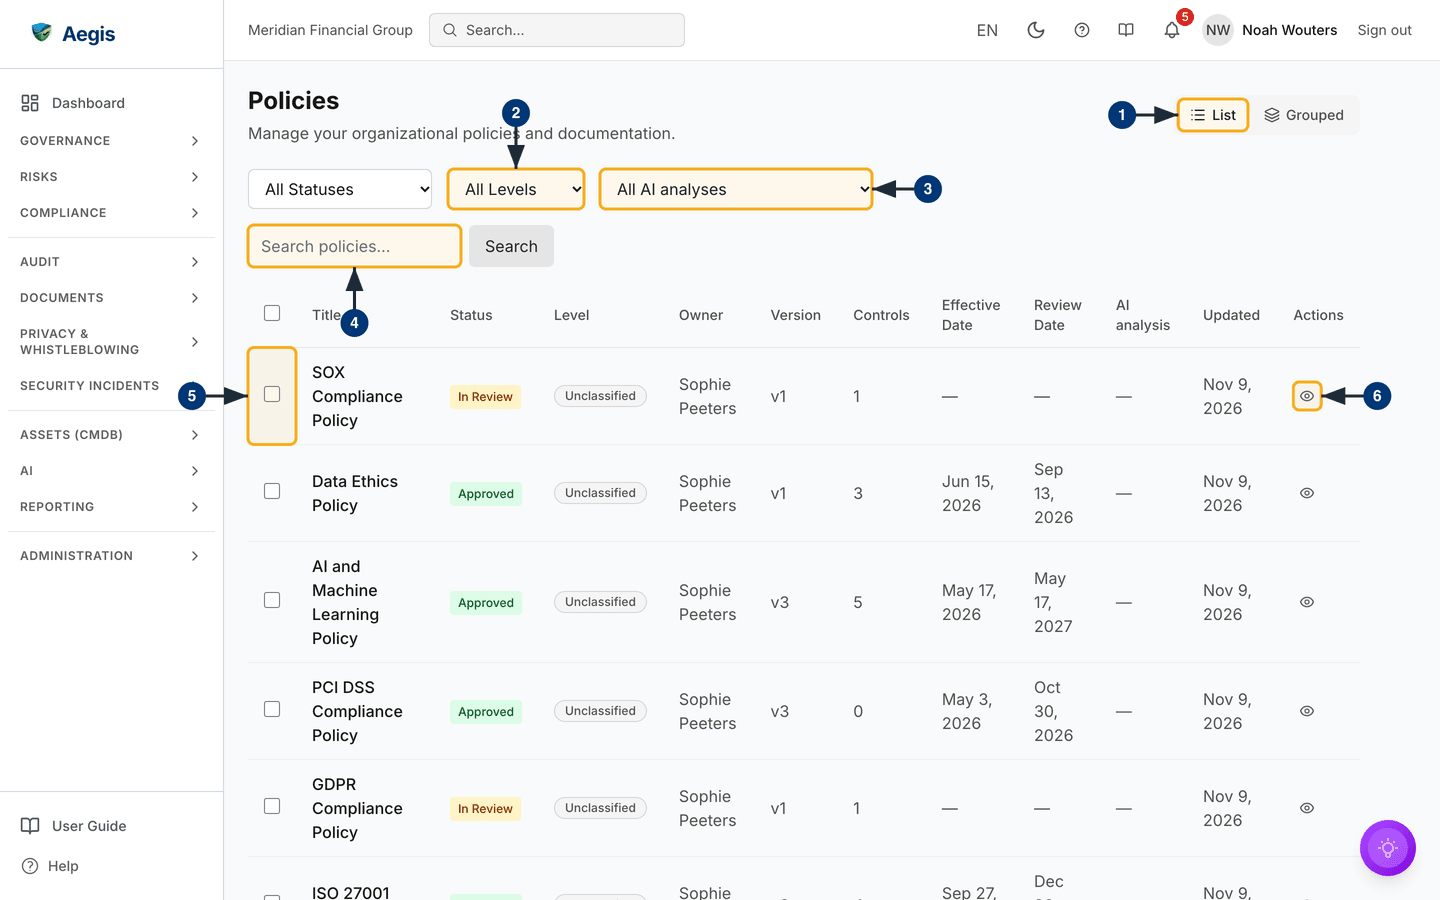
This capture settles one common question: the role controls which actions
succeed, not which rows appear. The Viewer sees policies still
In Review — such as SOX Compliance Policy on the
captured screen — alongside Approved
ones, and cannot change any of them.
The capability matrix
Underneath the four roles sit fine-grained
permissions — the individual checks Aegis
runs before accepting a change, each named in a
resource:action pattern. Each role is a fixed bundle of these
checks. An action your bundle lacks is refused with a
403 Forbidden; the message is short (Forbidden or
Insufficient permissions) and does not name the missing permission,
so use the table below to work out which role would have held it. Browsing to a
page you may not open sends you to /unauthorized instead. A ✓ below
means the role can do it.
| Action | Viewer | Contributor | Manager | Admin |
|---|---|---|---|---|
| Read policies, risks, vendors, evidence, incidents | ✓ | ✓ | ✓ | ✓ |
Export a report (report:export) |
✓ | ✓ | ✓ | |
Create and edit records (policy:create,
risk:update, …)
|
✓ | ✓ | ✓ | |
Run AI actions such as What needs my attention? and AI
analyses (ai:execute) — the Ask AI chat is
open to every role
|
✓ | ✓ | ✓ | |
Respond to data-subject requests (gdpr:dsr:respond)
|
✓ | ✓ | ✓ | |
Approve policies and procedures (policy:approve) |
✓ | ✓ | ||
| Delete policies, risks, vendors, incidents | ✓ | ✓ | ||
Delete evidence collection rules (evidence:delete) —
evidence items themselves cannot be deleted by any role
|
✓ | |||
Configure connectors (connector:*) |
✓ | ✓ | ||
Handle whistleblowing cases (whistleblow:*) |
✓ | ✓ | ||
| Write board reports, edit the Trust Center | ✓ | ✓ | ||
Regulatory incident reporting (/incidents/reporting)
|
✓ | ✓ | ||
| Users, roles, licence, SSO, API keys, webhooks | ✓ |
A number of sidebar entries never render below their minimum role, so the
page is not only refused — it is not offered. Roadmap,
Security Awareness, Risk Methodologies,
Risk Templates, Risk Appetite,
Control Mapping, CyFun Maturity,
ISO 42001, the CMDB lists (CMDB,
Software, Information Assets,
External Services), AI Dashboard,
AI Agents and Analytics require
Contributor.
Connectors, incident Reporting,
Whistleblowing and HR Connections require
Manager.
Auto-Incident Rules, API Keys,
Webhooks, License, Document Template,
Document settings and
Security & AI Controls require
Admin. Your licence and the
modules your operator has enabled can hide further entries for every role.
Reading ordinary records — including Board Reports,
Benchmarking, Mock Audit and the
Trust Center — is open to every role, which is why the Viewer
above still saw policies that are only in review.
Change someone's role
User and role management lives on the Settings page
as a tab, not at its own address: /settings/users redirects to the
canonical /settings?tab=users. Of the nine tabs on that page —
Account, Organization, Users,
Roles, Permission Groups, Integrations,
System, Frameworks and Diagnostics — the
administrative ones render only for an
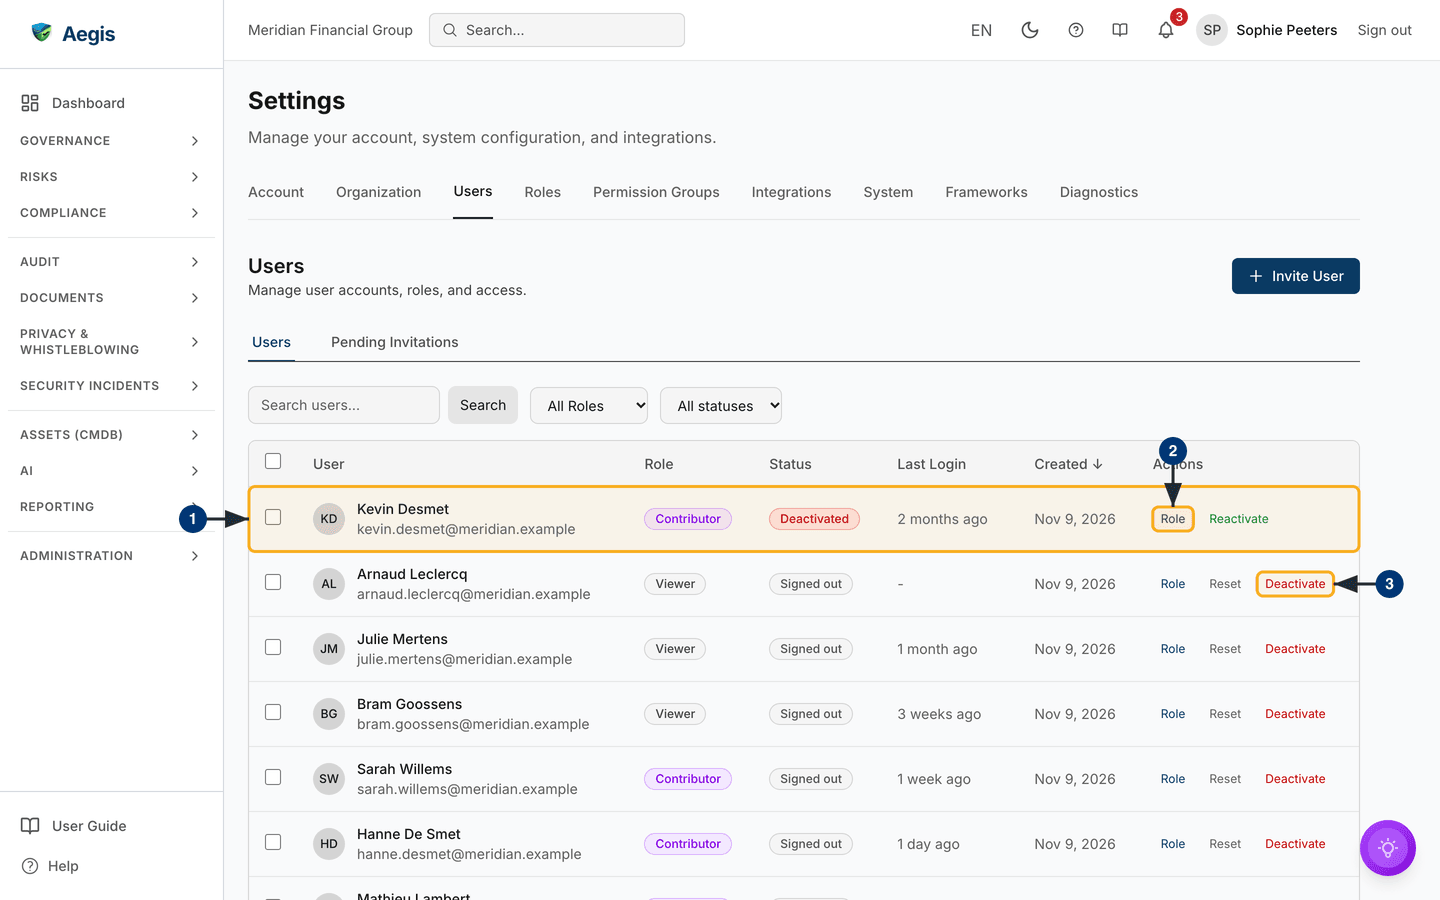
Admin. The capture below is the
Users tab as an Admin (Sophie Peeters on the captured
screen): an Invite User button, Users and
Pending Invitations sub-tabs, a Search users… box with
its Search button, All Roles and
All statuses filters, and a table of User,
Role, Status, Last Login,
Created and Actions.
-
Find the person's row. Each shows their name and email, a role badge, a
status, the last sign-in and the creation date. The status describes the
session, not the account:
Signed inmeans the person holds a live session,Signed outmeans they do not, and onlyDeactivatedmeans the account itself is blocked. Narrow a long list with the search box or the two filters, and select theUser,RoleorCreatedheading to sort by it; the table pages at 20 rows. -
Select
Roleon that row. A dialog opens listing the four built-in roles, each with a one-line description of what it grants; pick one and confirm, and the badge in theRolecolumn updates. The change applies from the person's next request — no sign-out needed, because the role is re-read on every check — and lands in the audit log with the previous role, the new role, who changed it and when. -
To remove access, select
Deactivate. The account can no longer sign in, its open sessions are revoked at once, and the person's records and audit history stay intact; the row then offersReactivateinstead, as the first row on the captured screen does.Resetbeside it sends a password-reset email; it needs email (SMTP) configured, and it is not offered on a deactivated account.
To act on several people at once, tick their checkboxes (or the one in the
heading for the whole page). A bulk bar appears with Change Role,
Deactivate, Delete and Clear; each action
asks you to confirm first. Delete here deactivates the accounts and
signs them out of every session — it does not erase their records.
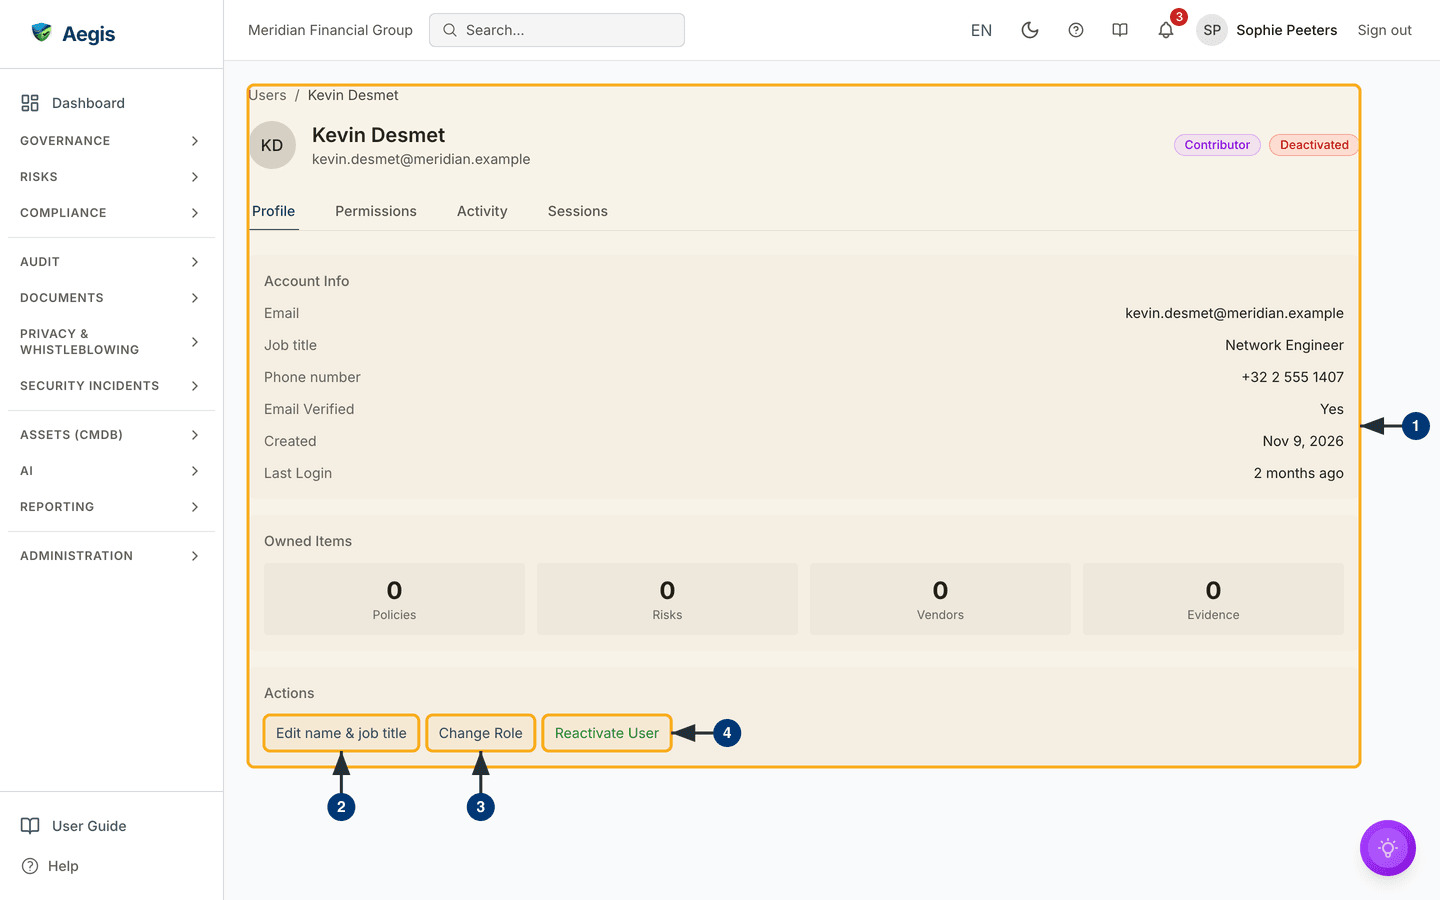
Open a person's detail page
Selecting anywhere on a user's row (other than an action link) opens their
detail page at
/settings/users/<id> — a full page you can bookmark and
reload. The capture below is a deactivated Contributor's: a breadcrumb (Users / Kevin Desmet
on the captured screen), the name and email beside the avatar with the role and
status badges on the right, and four tabs — Profile,
Permissions, Activity and Sessions. The
Profile tab shows an Account Info card (email, job
title, phone number, whether the email is verified, created date, last sign-in),
an Owned Items card counting the policies, risks, vendors and
evidence the person owns, and an Actions card.
-
Review the profile before you change anything: the badges top-right show the
current role and status (
ContributorandDeactivatedon the captured screen), andOwned Itemstells you how much work is attributed to this person — here0in every count. ThePermissionstab shows their role and the permission groups they belong to;ActivityandSessionsshow what they have done and where they are signed in. -
Select
Edit name & job title, the first button underActions. AnEdit profileform opens at the top of theProfiletab — see Correct someone's name or job title below. -
Select
Change Role. The same role chooser as on the list opens; pick a role and confirm, and the badge in the header updates. -
For a deactivated account, select
Reactivate Userto let the person sign in again. On an account that is not deactivated this place holdsReset Password, which sends a password-reset email (the same action asReseton the list), andDeactivate User, which blocks sign-in and revokes open sessions exactly as on the list.
To add a person, select Invite User, enter their email address and
choose a role; the account waits under Pending Invitations until
they accept and set a password. The Roles tab beside it is a
read-only reference — the four roles are defined in code, not in the database,
so there is nothing to edit there — and Permission Groups holds the
optional extra layer described under Tips and limits below.
Aegis blocks the two moves that would lock you out from inside the application: you cannot change your own role, and you cannot deactivate your own account — your own row's selection checkbox is disabled for the same reason. It cannot protect you from what happens outside the application. If your only Admin leaves or loses access, nobody can manage users, roles or settings. Keep a second active Admin, and contact Euraika support if you do lose Admin access.
Correct someone's name or job title
An administrator can fix a misspelt name or set a job title for someone else.
Edit name & job title sits first in the
Actions card, for anyone holding user:update — in
practice an Admin. Select it and an Edit profile form opens at the
top of the Profile tab with Display name (up to 255
characters) and Job title (up to 100; leave it empty to clear it).
Select Save, and User profile saved confirms it;
Cancel closes the form unchanged. The audit log records the old and
new name, and notes that the job title changed without storing it. For someone
who signs in through single sign-on or was created by the directory connector,
the name field is read-only with
Managed by your organisation's directory: change the name in the
identity provider instead. People edit their own details on their
profile page.
Map roles from your identity provider
If your organisation uses single sign-on (SSO — signing in with your existing
work account; see
Signing in), people can inherit an Aegis role from
their identity-provider group instead of being set one at a time. An Admin
configures this at Settings → Integrations → Single Sign-On (SSO);
any other role is sent to the access-denied page. Single sign-on is part of the
Enterprise licence: on a lower tier the page shows an upgrade prompt in place of
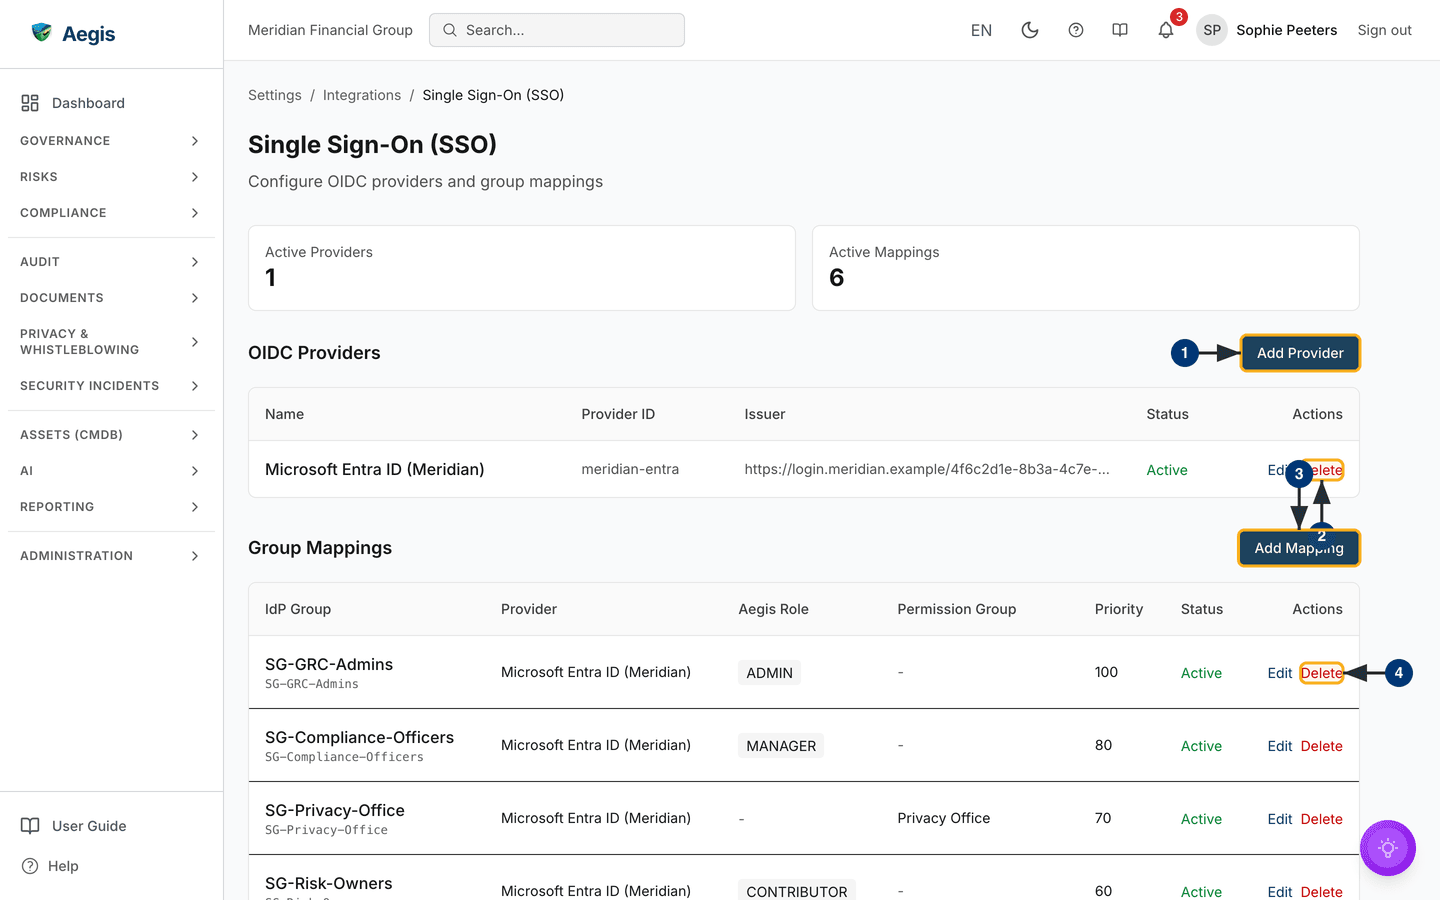
the tables below. The screen opens with two counters,
Active Providers and Active Mappings (1
and 6 on the captured screen), each counting exactly what its table
lists. Then comes the OIDC Providers table — Name,
Provider ID, Issuer, Status,
Actions — holding one Microsoft Entra ID provider on the captured
tenant, and the Group Mappings table — IdP Group,
Provider, Aegis Role, Permission Group,
Priority, Status, Actions. The captured
mappings send an administrators' group to ADMIN, a compliance
officers' group to MANAGER and a risk owners' group to
CONTRIBUTOR, while a privacy office group adds only a permission
group and no role.
-
Select
Add Providerto register an identity provider. TheAdd OIDC Providerdialog opens over the page — the next figure walks through it. -
Use
Deletein the provider row'sActionscolumn to remove a provider. Aegis asks you to confirm; the provider's own group mappings leave the table with it, and the sign-in route goes too, so people who used it must then sign in through another provider or a password account.Editbeside it reopens the same form on the existing provider instead. -
Select
Add Mappingto link one identity-provider group to an Aegis role, a permission group, or both. Enter the group exactly as it appears in the token's groups claim (for Entra ID, normally the group's object ID); when a Microsoft Entra ID connector is connected, the form also lets you search groups by name. The mapping appears in theGroup Mappingstable with its provider, role, priority and status. When someone belongs to more than one mapped group, the most privileged matched role wins. The form's help text says a higher priority takes precedence, but the role resolver picks the highest role whatever the priority, so do not rely on priority to give someone a lower role. -
Use
Deleteon a mapping row to remove it, after a confirmation (Editbeside it changes the role or priority instead). From the next sign-in, members of that group no longer inherit the mapped role; the role they already hold stays until an Admin changes it.
Add an OIDC provider
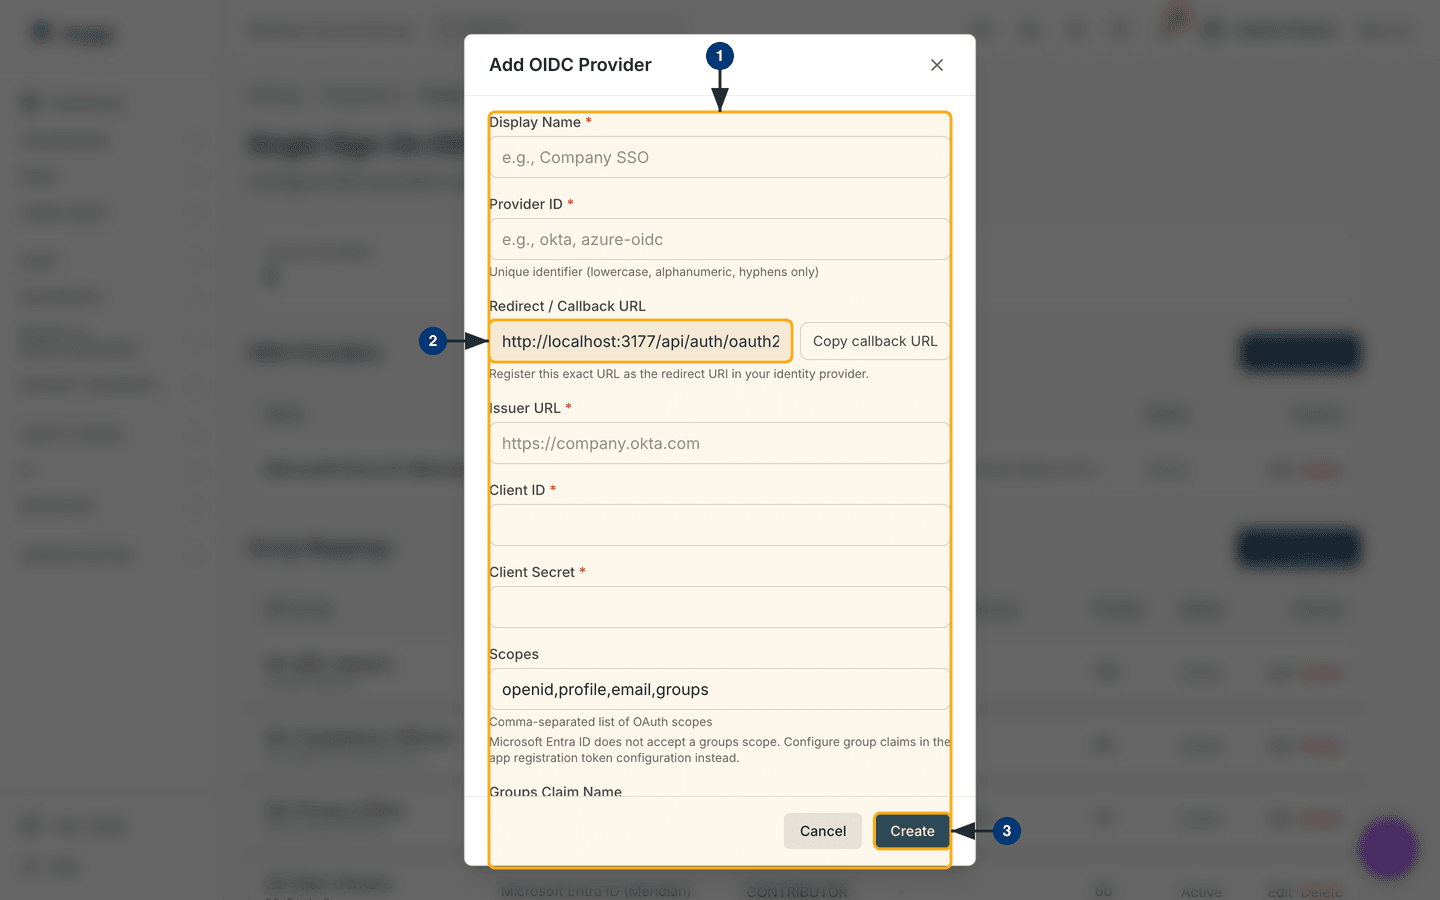
Add Provider opens a dialog with, in order,
Display Name, Provider ID (lowercase letters, numbers
and hyphens only), the read-only Redirect / Callback URL,
Issuer URL, Client ID, Client Secret,
Scopes (pre-filled with openid,profile,email,groups)
and Groups Claim Name. Required fields carry a red asterisk.
-
Fill in the form with the values from your identity provider's app
registration. Read the note under
Scopes: Microsoft Entra ID does not accept agroupsscope, so configure group claims in the app registration's token configuration instead. -
Select
Copy callback URLbeside theRedirect / Callback URLfield and register that exact URL as the redirect URI in your identity provider. Sign-in fails if the two differ by a single character. -
Select
Create. The dialog closes, the provider joins theOIDC Providerstable and theActive Providerscounter goes up.Cancel— or the × in the dialog header — discards the form instead.
A page can be hidden for three different reasons, and it is worth checking them in this order: your licence tier (some modules and frameworks are pay-to-unlock), then module enablement (your operator can switch whole modules off for the tenant), then your role. A Viewer on the highest tier with every module enabled still cannot create a policy — that is the role gate, not the licence.
Tips and limits
-
The four roles are fixed. You cannot create custom roles.
The
Permission Groupstab adds named permissions on top of a person's role — the two sets are combined, so a group can only add, never take away. - Role changes are not retroactive. A downgrade applies from the next request; work already authored or approved stays valid and stays attributed to its author.
- Approval routing is configuration, not a hard separation of duties. An approval configuration can name designated approvers by role or by person, and can require more than one approver. Aegis does not by itself stop a Manager approving a policy they drafted, so if you need author and approver to be different people, set the approvers deliberately and check the approval history on the record.
- Deleting evidence is Admin-only. A Manager can delete policies, risks, vendors and incidents, but not evidence — that one sits with Admin.
-
Report export skips Contributor. A Viewer and a Manager can
export a report; a Contributor can create and edit reports but does not hold
report:export, so ask a Manager for the file. - Deactivated accounts still count in the user total. The usage figure Aegis reports counts every account, active or not. Under the 2026 licence catalogue no tier caps the number of users, so this affects the reported number rather than your access.
-
Email addresses are not self-service. There is no
change-email control on the
Userstab; contact Euraika support, who verify identity first.
Where this connects
For the complete per-role list of every action, see the action catalogue. To watch the roles work end to end, follow preparing for an external audit. The read-only surfaces above are covered in The dashboard and Policies; the administrative ones in Settings, Microsoft Entra ID sign-on and API keys. If a role gate surprises you, getting help explains how to reach support.