Incidents
Get a security event on record the moment it is detected, work it from investigation to closure, and keep the regulators' notification clocks in view while you do.
An incident is something that has already happened — not a risk that might. This module records the event, moves it through a defined lifecycle while stamping the time at every step, counts down any notification deadline it triggers, and holds the post-incident write-up so the proof is there when an auditor asks. Every change goes to the audit trail.
This chapter is the screen-by-screen reference. To see a response worked as a story — detection, triage, regulator deadlines and the post-incident review — see the full walkthrough in Scenario: respond to a security incident.
Who uses it
- Viewer reads the register and any incident, and can tick rows to export the selection as a CSV file.
- Contributor can also report an incident, move it through its statuses, add timeline entries, start a response playbook, and close it.
-
Manager can additionally
delete an incident, confirm or dismiss a suspected personal-data breach,
record the GDPR notification, record the reporting decision, and open the
reporting dashboard at
/incidents/reporting; anyone below that role who goes to the address is sent back to the register. -
Admin does all of that, and
alone can open
Auto-Incident Rules— gated on a settings permission a Manager does not hold.
The breach decisions sit with Manager and Admin on purpose: confirming a breach, recording that the authority was notified, or deciding not to report all start or stop the GDPR 72-hour clock, so they are decisions of record rather than routine edits. A Contributor sees the breach alerts but not those buttons.
What's on this screen
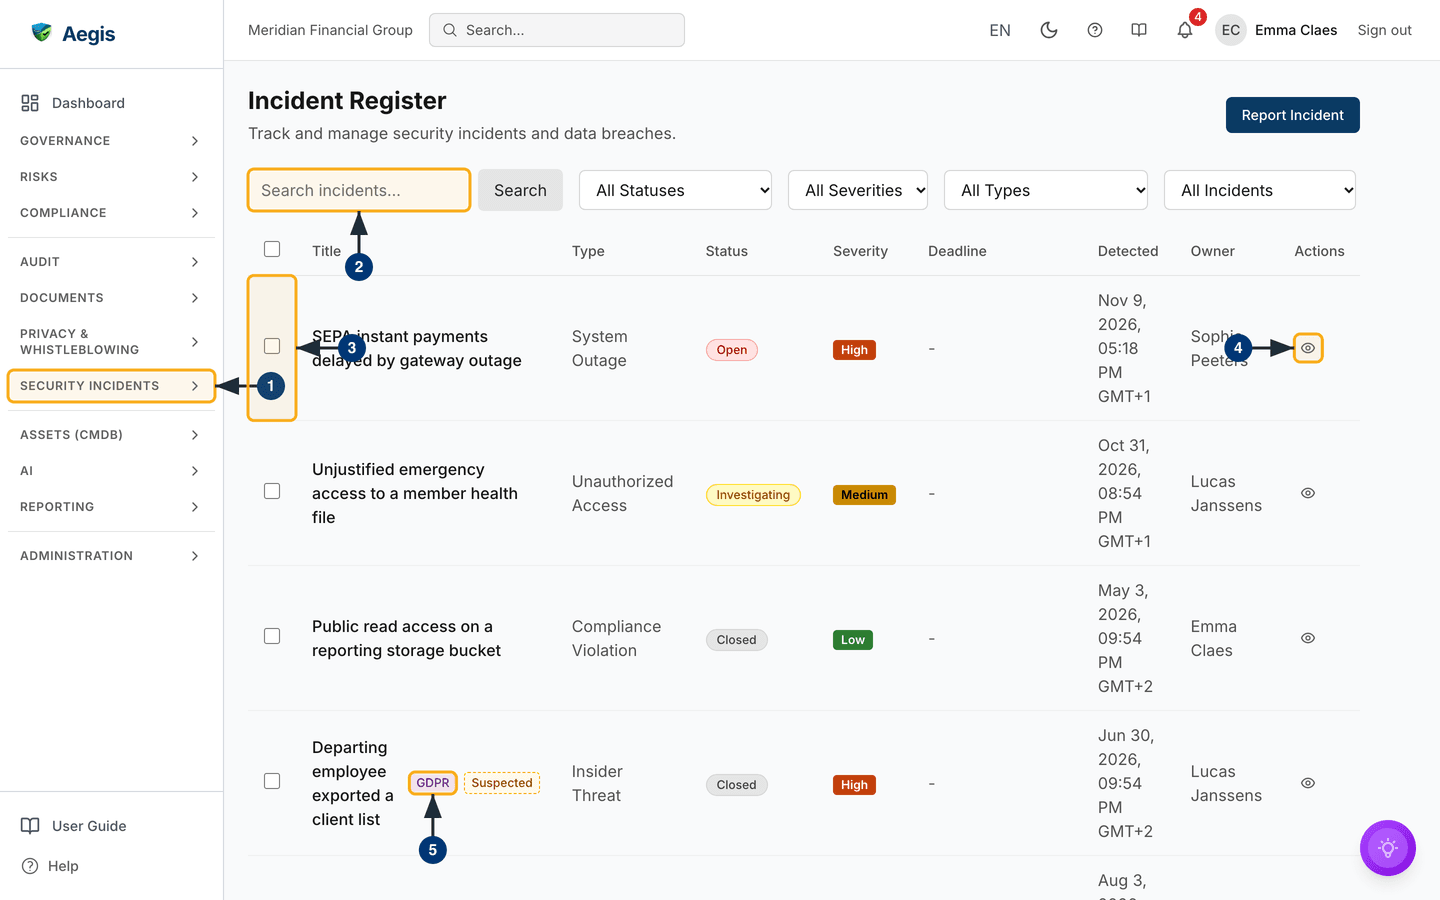
The header reads Incident Register over "Track and manage
security incidents and data breaches", with the dark
Report Incident button on the far right. Beneath it sits the filter
bar: a Search incidents… box with its own
Search button, then All Statuses,
All Severities, All Types and
Any breach status — the last offering
Data Breaches Only or Non-Data Breaches. The status
list also holds Open (not resolved), which shows every incident not
yet resolved or closed; the dashboard's open-incidents tile lands you here with
that filter already set. The filters combine, so each one narrows the list
further.
The table has a tick-box column, then Title, Type,
Status, Severity, Deadline,
Detected, Owner and Actions. Status and
severity are coloured chips, and the detected time is shown in your local time
with its time zone, for example GMT+1. In the captured screen the
rows mix one Open, one Investigating and then
Closed incidents, and every visible row has a dash under
Deadline — no outstanding notification obligation. When an incident
does owe one, the cell shows a chip naming the regime (GDPR,
NIS2 or DORA) with a countdown, or an overdue figure
once the deadline has passed, and a marker such as +2 when further
deadlines sit behind the nearest one. DORA deadlines are left out when DORA is
switched off for your organisation.
A purple GDPR badge beside a title marks a personal-data breach and
turns red as GDPR! once the 72-hour window passes with no
notification recorded. A dashed amber Suspected badge next to it
means the breach was flagged but no Manager has yet confirmed or dismissed it —
the captured screen shows one such row, an insider-threat incident.
Actions holds an eye icon; a bin icon joins it for Manager and
Admin, so this Contributor view shows the eye alone. The page loads 20 rows at a
time.
-
Open the
Security Incidentsgroup in the left menu and chooseIncidents. The register loads with the most recently detected incidents on top. -
Type a word from an incident's title into
Search incidents…and selectSearch. The table reloads showing only matching titles. Narrow further with the four dropdowns; each applies on selection and stacks with the others. -
Tick the box at the start of one or more rows. A bar appears with
Export, which downloads the selected incidents as a CSV file. -
Select the eye icon in
Actions— or the title itself — to open the full incident page, where the AI panels, the significance wizard and the regulatory filings live. Select anywhere else on the row instead and the Incident Details dialog opens over the table. -
Read the badges beside a title.
GDPR(or redGDPR!) marks a personal-data breach;Suspectedmeans that breach still awaits a Manager's decision. Hover over either for its meaning.
Statuses and severity
Aegis offers only the valid next steps from the current status.
| Status | Meaning | Can move to |
|---|---|---|
OPEN |
Recorded; investigation not started. |
INVESTIGATING, CONTAINED,
CLOSED
|
INVESTIGATING |
Being analysed; root cause not yet known. |
CONTAINED, RESOLVED, CLOSED
|
CONTAINED |
Stopped from spreading, not yet resolved. |
RESOLVED, INVESTIGATING,
CLOSED
|
RESOLVED |
Root cause addressed; operations resumed. | CLOSED, INVESTIGATING |
CLOSED |
The record is complete. | Nothing — closure is final. |
Severity runs LOW, MEDIUM, HIGH,
CRITICAL, set on reporting and revisable as the investigation
develops.
Reporting an incident
Reporting now happens on a page of its own, /incidents/new, rather
than in a dialog over the register. The form is still short on purpose: during a
live response you want the event on record in under a minute and the detail
filled in later.
- Before you report, search the register for the event. If a colleague or a connector rule has already recorded it, work that incident instead of opening a duplicate.
-
Select
Report Incident. The Report New Incident page opens, with a breadcrumb back to theIncident Registerabove it. -
When you finish the form (steps below), Aegis takes you straight to the new
incident's own page. Back on the register it appears in this table in
OPENstatus.
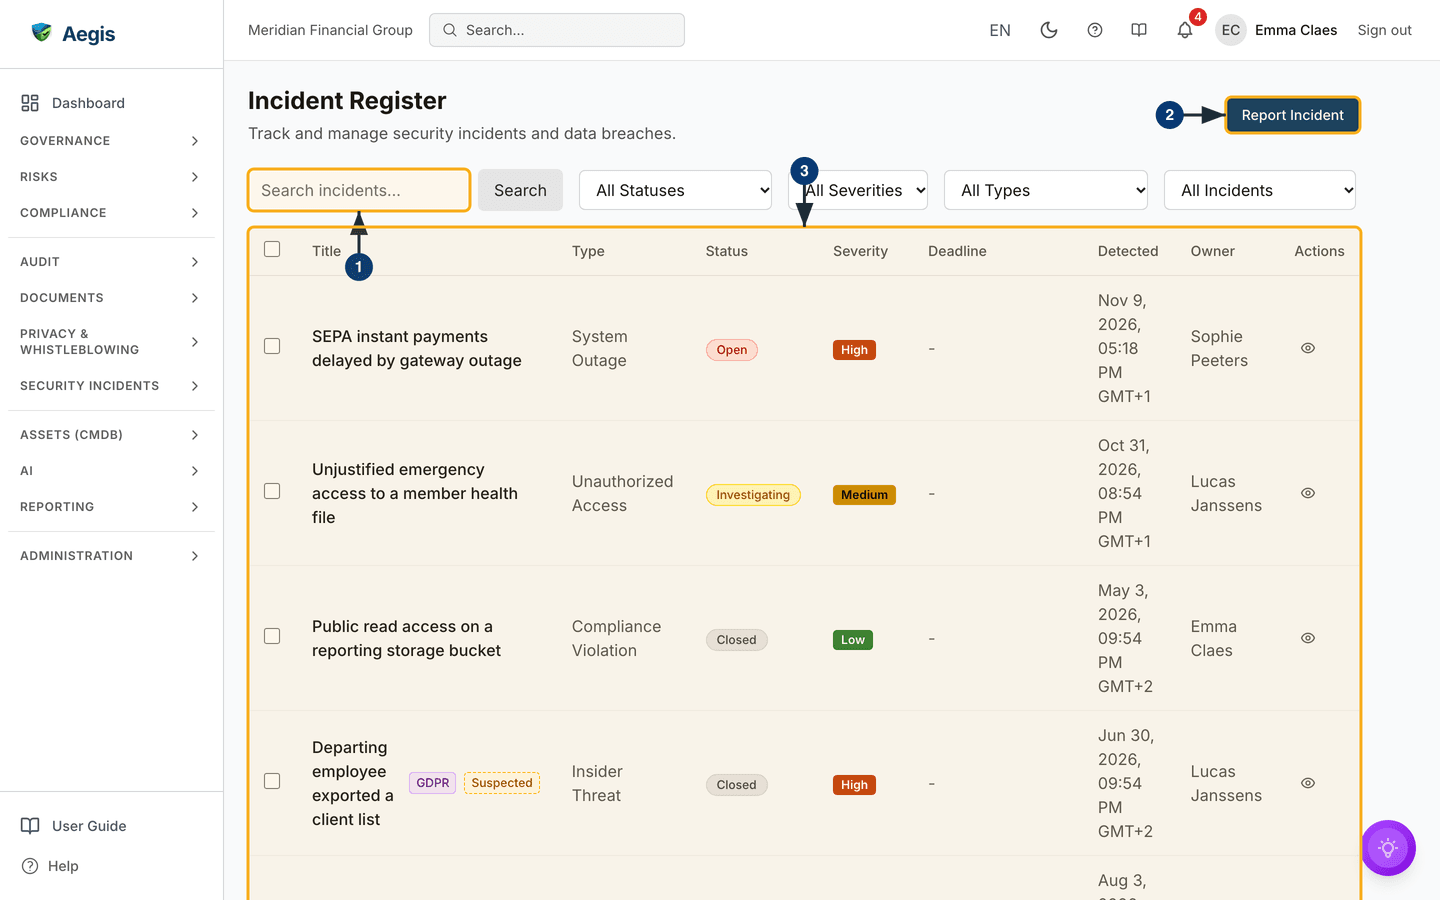
The capture above shows the register at the moment you start; the form itself is
on the next page and is not pictured. It has two cards —
Incident Details and Detection & Impact — then the
breach box and the buttons.
-
Enter an
Incident Title. Required — the form will not submit without it. -
Add a
Description: what happened, how it was discovered, first observations. Optional, and it can wait. -
Choose an
Incident Typeand aSeverity. They open onOtherandMedium - Moderate impact; both are required, so change them if those defaults are wrong. -
Fill
When was the incident detected?. The note beneath says this timestamp drives the GDPR 72-hour calculation, and Aegis rejects a time in the future with "Detection time cannot be in the future". -
Optionally list
Affected Systemsas a comma-separated line. Each entry becomes a tag on the incident. -
If personal data may have been accessed, disclosed or lost, tick
This incident involves a personal data breach. ANumber of Data Subjects Affectedfield appears. The note under the box explains that the incident is recorded as a suspected breach until a Manager confirms it, and that the 72-hour deadline runs provisionally from detection in the meantime. -
Select
Report Incident. The button stays greyed out until the title and detected time are valid. Once selected, a confirmation appears and the new incident's page opens. -
Select
Cancelto discard everything you typed and return to the register.
The GDPR 72-hour window and the three NIS2 stages run from the detected time you enter here, not from the moment you log the incident. If you later learn the event started earlier, correct it.
Review security signals from connectors
Security alerts from a connector do not become incidents on their own. This
covers Microsoft Defender XDR (Defender incidents with their related alerts
already grouped), CrowdStrike Falcon detections, AWS GuardDuty findings, GitHub
secret-scanning alerts and high or critical Palo Alto threat logs. Each sync
puts new alerts in
Security Signals (under Security Incidents in the sidebar) as
pending signals. A person decides every one; nothing is created or discarded
automatically. This keeps a flood of alerts, such as dozens of email alerts from
one phishing campaign, out of the incident register while still keeping each
alert on record.
Each pending signal shows a suggestion with its reason. It is advice, not a
decision:
Dismiss when the source system already resolved, closed or archived
the alert (for example Defender removing a malicious email after delivery),
marked it a false positive or expected activity, or rated it informational;
Merge when an open incident from the same source has the same
title; Keep for anything else.
With AI assistance switched on, Aegis also asks the AI to triage each batch of
new signals after a sync (one AI credit per batch). Its suggestion appears in a
purple box under the rule suggestion, marked as AI-generated, with a short
reason and a confidence percentage. It is advice only: the AI never creates,
merges or dismisses a signal. If AI is off or out of credits, the signals keep
only the rule suggestion. Merge as suggested uses the rule's
incident first and the AI's when the rule has none.
-
Open
Security Signals. The list opens onPending; filter bySuggestionto work through similar alerts together. -
Select one or more signals and choose an action:
Create incidents(one incident per signal),Combine into one incident(one incident from the most severe signal, the others merged into it),Merge as suggestedorDismiss. Dismiss asks for confirmation. -
Check the result message. A signal someone else decided in the meantime is
skipped, never decided twice. Switch the
Statusfilter to see accepted, merged and dismissed signals and open the incident each one belongs to.
Creating or merging adds an entry to the incident's timeline and records the
signal as evidence linked to that incident. Alerts are no longer copied into the
Evidence Locker as they arrive: only a signal someone kept becomes evidence, so
the locker holds triaged alerts rather than every raw one. A dismissed signal
stays on record in Security Signals only. Deciding needs the
permission to edit incidents; creating an incident also needs the permission to
create one.
Reading an incident
The Details grid and the Timeline always appear; the
Description, Affected Systems,
Root Cause, Remediation and
Lessons Learned panels show only once their field holds something.
The incident in the captured screen is open, high severity, with a description
and two affected systems, and dashes under Contained,
Resolved and Closed because it has reached none of
those states yet. Because it is still open, the Update status panel
is offered; on a closed incident that panel disappears — there is nothing left
to change.
- Select a row in the register. The dialog opens at the top of the record — title, status chip, severity chip, then the type and detected line.
- If you opened the wrong row, select the × in the dialog header. Nothing is changed and you are back on the register.
-
Use the
Update statuspanel to move the incident on. It holds one button per valid next step — hereMark Investigating,Mark ContainedandMark Closed, the three moves open fromOPEN. The callout marksMark Closed, which opens a confirmation first (see Closing an incident below). -
Read the
Description, then theDetailsgrid for the owner and five lifecycle timestamps (Detected,Reported,Contained,Resolved,Closed). A dash means the incident never reached that state. Scroll on throughAffected Systems,Root Cause,Remediation,Lessons Learnedand theTimeline, where Contributors and above get anAdd Entrycontrol. A short dialog means a thin record, not a fault. -
Select
Closeat the foot of the dialog. Anything you changed was saved as you went.
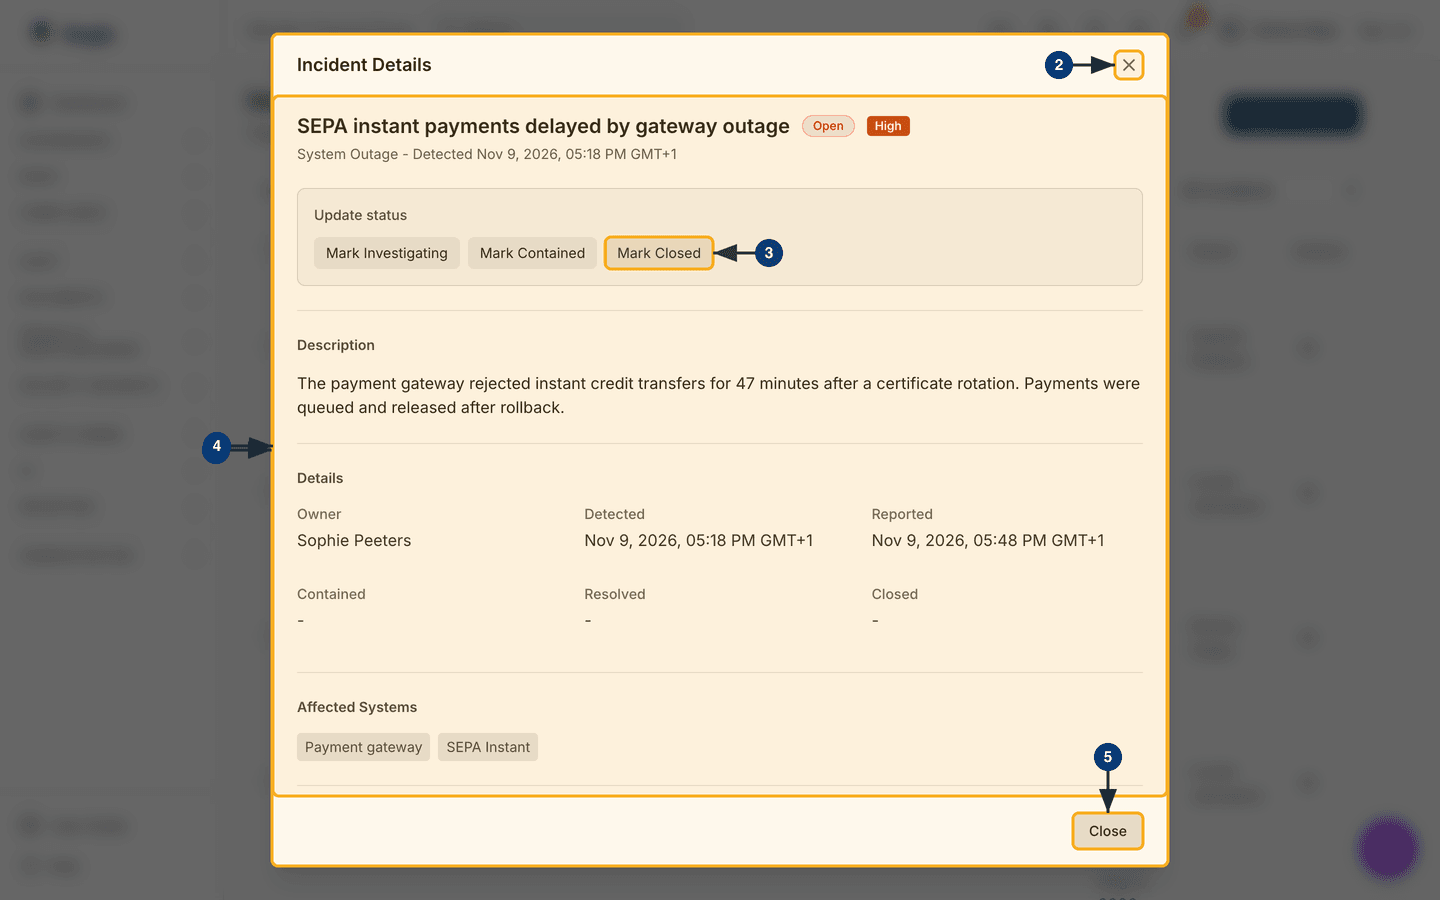
For a personal-data breach the dialog also shows the GDPR alert under the
header, and a Manager or Admin sees a
Record GDPR Notification button there until the notification is
recorded.
Moving an incident through its statuses
While an incident is still open, the Update status panel sits
between the header and the description with one button per valid next step.
Viewers do not see it at all. The same controls sit beside the title on the full
incident page.
-
Select the step you want, for example
Mark Investigating. The status chip changes, the matching timestamp is stamped and the timeline gains an entry. If someone else changed the status a moment before you, Aegis refuses the change and says so rather than silently doing nothing. -
Carry on through
Mark ContainedandMark Resolved. From either you can step back toMark Investigatingif new facts reopen the analysis. -
Select
Add Entryin the timeline to record what you found or did. The entry carries your name and the time.
Closing an incident
Mark Closed is offered from every status before closure, not only
from RESOLVED, and it opens a confirmation dialog rather than
closing on the spot.
-
Select
Mark Closed. The Close Incident dialog names the incident and states that this marks it resolved and will set the closed timestamp. -
Optionally fill
Resolution Summary (Optional), saved as the incident'sRemediation, andLessons Learned (Optional), saved as itsLessons Learned. Text already stored in either field is shown so you can keep or extend it. If someone else changed the incident in the meantime, the dialog says so and keeps your text. -
Select
Close Incident. The status becomesCLOSED, the closure time is recorded and the register refreshes.
Aegis offers no transition out of CLOSED, so a closed incident
cannot be reopened. Check that root cause and remediation are recorded
first; afterwards the only way to add anything is a timeline entry.
The full incident page
The eye icon or the title opens /incidents/<id>. A breadcrumb
leads back to the Incident Register; any GDPR or NIS2 alert banner
sits above the title, and the status buttons sit to its right. The main column
holds the description, affected systems, root cause and remediation, the
timeline, the regulatory filings, the authorities' acknowledgements,
communications and response playbooks. The right-hand column holds the details,
a Jira link panel, the reporting decision, the DORA classification (when DORA is
switched on for your organisation) and the two AI panels. For a personal-data
breach a 72-hour countdown runs across the page under the header.
Response Playbooks lists any remediation playbook started for this
incident, with its status and a percentage complete, each linking through to the
playbook itself. A Contributor or above can pick a
Playbook template — Incident Response is the default —
or type a Custom playbook title, then select
Start playbook. Until one is started the panel reads "No playbook
has been started for this incident yet." See
Playbooks for working the steps.
An incident raised from a Microsoft Purview data-loss alert also carries a
Data Loss badge beside its title and a data-loss panel in the main
column, shown only to people with access to data-loss monitoring.
Regulatory deadlines
Aegis counts every clock from the detected time. Two European regimes drive the
flags you set here; the Deadline column also counts DORA stages,
but only for an incident classified as a major ICT incident.
GDPR (the EU's data-protection law) requires a personal-data breach to be notified to the supervisory authority within 72 hours. Flag the incident as a data breach and an alert shows whether that window is open, closing or overdue.
Confirming or dismissing a suspected breach
A breach flagged when the incident is reported — on the form, from Slack or by a
connector — starts as a
suspected breach (flagged, but not yet
confirmed). The alert reads Suspected data breach with a
Provisional badge, and explains that the 72-hour clock runs from
detection as a precaution until someone decides. A Manager or Admin then
chooses:
-
Confirm breach— records the decision with the decider's name, keeps the 72-hour deadline from detection, and starts the breach notifications and workflows. -
Dismiss— asks for a reason of at least ten characters, then clears the breach flag and its deadline. Dismiss is no longer offered once the authority notification has been recorded: a notified breach is a filed fact.
Once you have notified the authority — inside Aegis or outside it — a Manager or
Admin selects
Record GDPR Notification to stamp the time. That clears the red
GDPR! badge and puts the notification in the audit trail. A
recorded decision not to report also stops the deadline counting as overdue.
NIS2 (the EU cybersecurity law) applies only once an incident has been judged significant. Three stages then run:
| Stage | Deadline |
|---|---|
| Early warning | 24 hours after detection |
| Incident notification | 72 hours after detection |
| Final report | 1 month after the incident notification |
To make that judgement, open the full incident page and select
Assess Significance in the AI Analysis panel — or
Open Full Assessment if a reading is already there. The
NIS2 Significance Assessment wizard opens over the page. Step
1, Automatic Checks, runs four tests against the record — high or
critical severity, the data-breach flag, at least one affected system, a
high-risk incident type — and counts how many are met. Step 2,
AI Assessment, shows the AI reading if one has been run, and offers
Run AI Assessment or Skip to Decision if not. Step 3,
Decision, asks you to choose Mark as Significant,
which activates the deadlines above, or Not Significant, which
records the judgement without them. Neither takes effect until you select
Confirm.
Filing, deciding and telling people
Three further panels sit on the full incident page.
Regulatory Notifications appears once an incident is a data breach
or marked significant, holding the filings it triggers —
GBA — Personal data breach notification (Belgian Data Protection
Authority, GDPR Article 33) and
CCB — NIS2 significant incident report (Centre for Cybersecurity
Belgium). Select Generate draft, review it, then
Mark as filed and enter the reference the authority gave you. For a
Dutch care provider the section also lists Z-CERT and the IGJ calamity duty;
Incident reporting explains when they
appear.
Reporting Decision holds the judgement itself, separate from the
filing: it reads Pending Decision until a Manager or Admin selects
Record Decision and chooses Report or
Do Not Report with a reason. It then shows the decision, who made
it and when — what a regulator asks for when a breach was assessed and not
reported. The Recorded: line gives that moment in your local time
with its time zone, for example GMT+2, as do the GDPR breach
milestones and the recorded authority acknowledgements, so a reader in another
zone does not misread a deadline. Update Decision revises it later.
Communications records what you told people; external messages pass
through Create draft, Approve and Send,
so nothing leaves without a second pair of eyes.
The panel says so itself: drafts are for review only, Aegis transmits nothing to an authority, and the field mappings need sign-off from your data protection officer or legal team. File through the authority's own channel, then record the reference here.
The AI assist
The full incident page carries two AI panels. AI Analysis offers
Run AI Assessment, weighing the incident against the NIS2 criteria
and returning a Likely Significant or
Not Significant reading with a confidence figure, per-criterion
reasoning and the frameworks it thinks apply. Once an incident is marked
significant, the same panel adds a button that drafts each notification stage —
Draft Early Warning, Draft Notification,
Draft Intermediate and Draft Final Report.
AI Triage holds one button, Deep AI Triage, which runs
a longer pass — significance under NIS2, GDPR and DORA, whether this looks like
a personal-data breach, the notification stages and their deadlines, related
risks, affected assets and relevant controls, and prioritised response actions.
The panel says it takes 30 to 90 seconds.
The panel states it plainly, and so do we: these are recommendations drawn from your own records, and a person must confirm them. Neither panel changes a status, marks an incident significant, files a notification or tells anyone. Both need the AI feature enabled for your organisation, and both are write actions — a Viewer can read a finished reading but cannot run one.
Tips and limits
-
The row and the title go to different places. The row opens the dialog; the
title, or the eye in
Actions, opens the full page — the only place with the AI panels, the significance wizard, the regulatory filings, the reporting decision, communications and playbooks. -
A
+2beside a deadline chip means further deadlines sit behind the nearest one. Open the incident to see them all. -
A
Suspectedbadge is a prompt for a Manager, not a fault. Until someone confirms or dismisses the breach, its 72-hour deadline is provisional but still counts down, and still shows as overdue if it passes. - The reporting dashboard lists one row per pending stage, so an incident that is both NIS2 significant and a GDPR breach fills several rows. They are separate obligations, not duplicates.
-
If the AI controls are missing, check the AI feature is enabled for your
organisation and that you hold Contributor or above.
Assess Significanceopens the wizard at every severity and spends no AI credit. The suggestion around it appears only while the incident is high or critical severity, or flagged as a data breach, andReview Significance Decisionreplaces it once the incident is marked significant. - The foot of the register links to a regulatory and an operational runbook. Both open in a new tab and cover the process around the tool, not the tool itself.
Where this connects
Deadlines across every incident are tracked in Incident reporting. Rules that raise incidents from connector events live in Auto-incident rules. For the personal-data side of a breach see GDPR; to fire a notification or task when an incident opens see Workflows, and to work a structured response see Playbooks. A recurring incident often belongs in the risk register too, and every change shows in the audit log. For the journey end to end, follow the incident scenario.