Audits
Plan and run a real compliance audit from end to end — name the engagement, pick the controls it will test, assign a lead auditor, record what the audit found, issue its report, and move it through its lifecycle from planning to closure.
An audit engagement (a planned exercise that
checks whether a set of controls really work) is the live record of an audit you
are running or preparing for. Each engagement carries a name, an optional date
range and report-due date, a lead auditor, and a
scope — the framework controls the audit will
test. Every control in scope becomes one plan item: a single
control under test, with its own tester and status. The engagement therefore
doubles as the checklist of work to be done. What the audit found is recorded as
findings (each observed shortfall, with a
severity, an owner and a due date), and the engagement ends with one audit
report that a person writes and issues.
The screen lives at /compliance/audits, but its menu entry sits in
the AUDIT group in the left menu, alongside
Mock Audit, Benchmarking and Audit Log.
It is not the same as Audit readiness, which
scores how prepared you are; Audits is where you run the engagement itself.
This chapter is the screen-by-screen reference. To see the preparation for a real external audit worked as a story — evidence, policies, rehearsal and the audit week itself — see the full walkthrough in Scenario: prepare for an external audit.
Who uses it
Access follows your role, and the permissions differ enough that two people can look at the same audit and see different buttons.
| Role | What you can do here |
|---|---|
| Viewer |
Read-only: open the list, filter it, read any audit's status,
metadata, plan items, findings and report, and download the
engagement package with
Export package.
|
| Contributor |
Everything a Viewer can do. Contributors are the testers — they hold
the fieldwork (“conduct”) permission, so they can assign a tester to
a plan item, move its status forward directly in the plan-items
table, and record and edit findings. No
New audit button, and no way to change the audit's
status, edit its report or delete a finding.
|
| Manager | Create an audit, edit it, change its status along the lifecycle, write and issue the audit report, delete findings, and delete the audit. Managers also hold the fieldwork permission. |
| Admin | Everything a Manager can do. |
Audits also needs the Compliance module switched on for your organisation,
because the route sits under the /compliance prefix. If it is not
switched on, the Audits entry drops out of the
AUDIT group and the route itself is blocked. Opening
/compliance/audits/new without the create permission sends a
Contributor or Viewer back to the dashboard.
What's on this screen
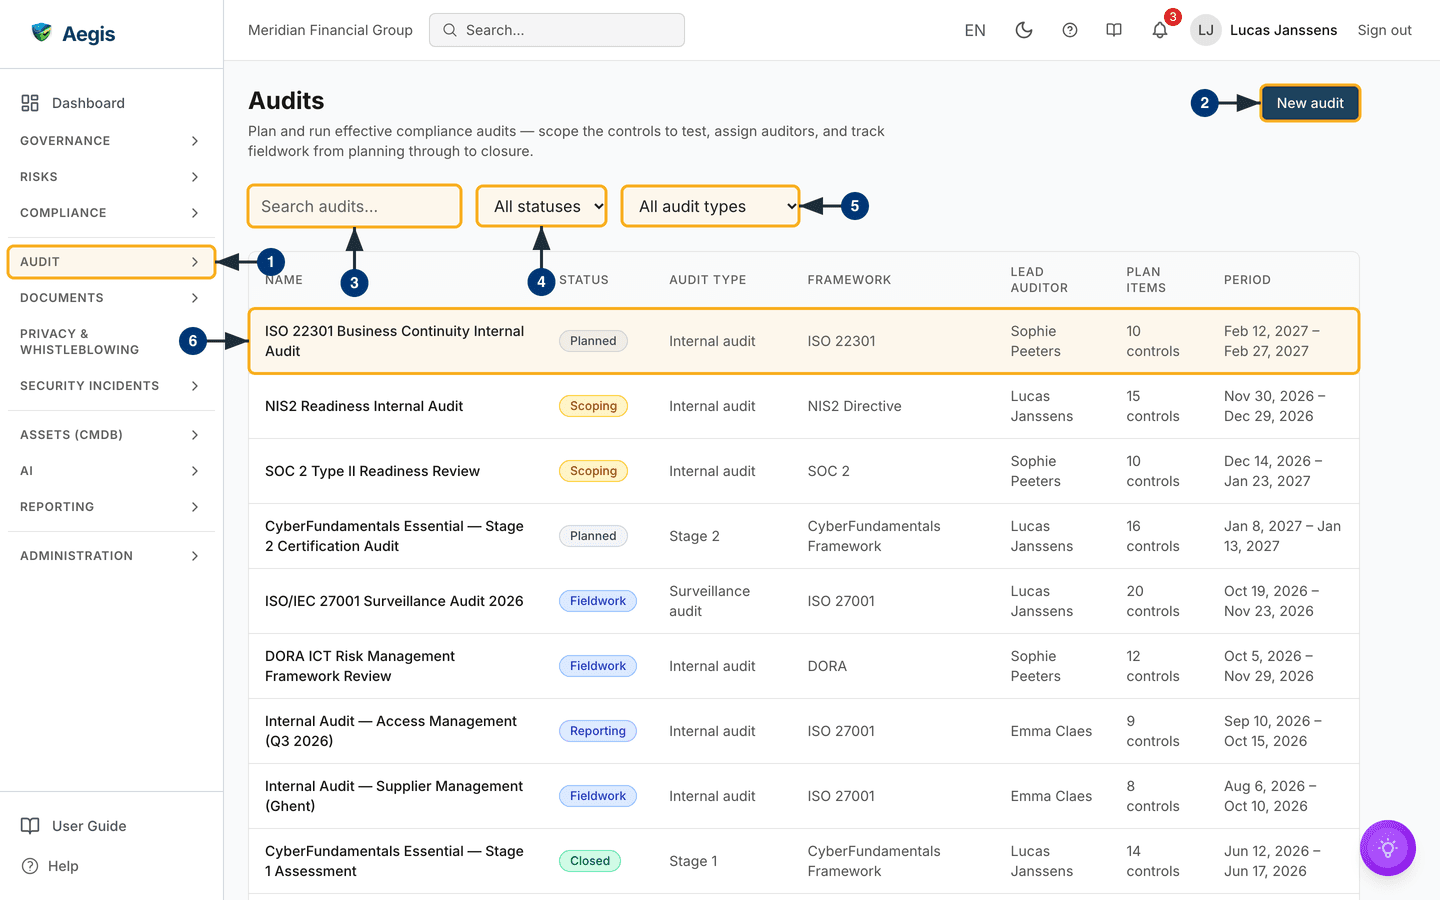
At the top-left sits the page heading Audits with a one-line
description: “Plan and run effective compliance audits — scope the controls to
test, assign auditors, and track fieldwork from planning through to closure”.
For a Manager or an Admin, as in the capture below, a navy
New audit button sits at the top-right of that same row; a
Contributor or Viewer does not see it.
Under the heading is a three-control filter bar: a
Search audits... box that matches on the engagement name, an
All statuses dropdown for the lifecycle stage, and an
All audit types dropdown for the kind of audit.
Below the filter bar is the list. The table has seven columns:
Name, Status (a coloured badge),
Audit type, Framework, Lead auditor,
Plan items (how many controls are in scope, for example “10
controls”) and Period. The captured screen shows engagements at
every stage, from Planned through Closed, including
internal audits and certification stages. A pagination row sits at the foot,
below the part of the page the capture shows, with Page 1 of 1,
Previous and Next. With no audits at all, an empty
panel reading No audits yet takes the table's place.
Find your way to the list and filter it
-
Open the
AUDITgroup in the left menu. The group expands and reveals its pages, includingAudits; select it to land on this screen. -
Select
New audit(Manager or Admin) to plan an engagement. The create page is described in the next section. -
Type part of an engagement's name into the
Search audits...box. The list re-queries shortly after you stop typing and jumps back to the first page of matches. The search matches the name only — not controls, not auditors. -
Choose a stage from the
All statusesdropdown —Planned,Scoping,Fieldwork,ReportingorClosed— to show only engagements at that stage. -
Choose a kind of audit from
All audit types:Internal audit,Stage 1,Stage 2,Surveillance audit,RecertificationorTransition audit. The certification-body types let you follow a certification cycle from the first stage through to the yearly surveillance audits. - Select a row to open that engagement's detail page, with its status control, metadata block, plan items, findings and report. If your filters exclude every audit, the message “No audits match the current filters.” appears instead; clear the box and reset the dropdowns to bring the rows back.
Create an audit
Creating an audit is a Manager or Admin task. It opens a full page at
/compliance/audits/new rather than a side panel, because the scope
picker needs the room. The page is headed New audit with the note
“Name the engagement, choose its scope and assign a lead auditor.” Fill in the
fields at the top first:
-
Audit nameis the only required field. Leaving it blank and submitting produces the inline message “An audit name is required” and nothing is saved. -
Audit typedefaults toInternal audit. Pick the certification stage when a certification body runs the audit; the type shows in the list and labels the milestone on a framework's certification timeline, such as the one on the NEN 7510 hub. You can change it later on the detail page. -
Lead auditoris a dropdown of users and defaults toUnassigned. -
Period start,Period endandReport due dateare optional. An end date before the start date raises “Period end must be on or after the period start” and blocks submission.
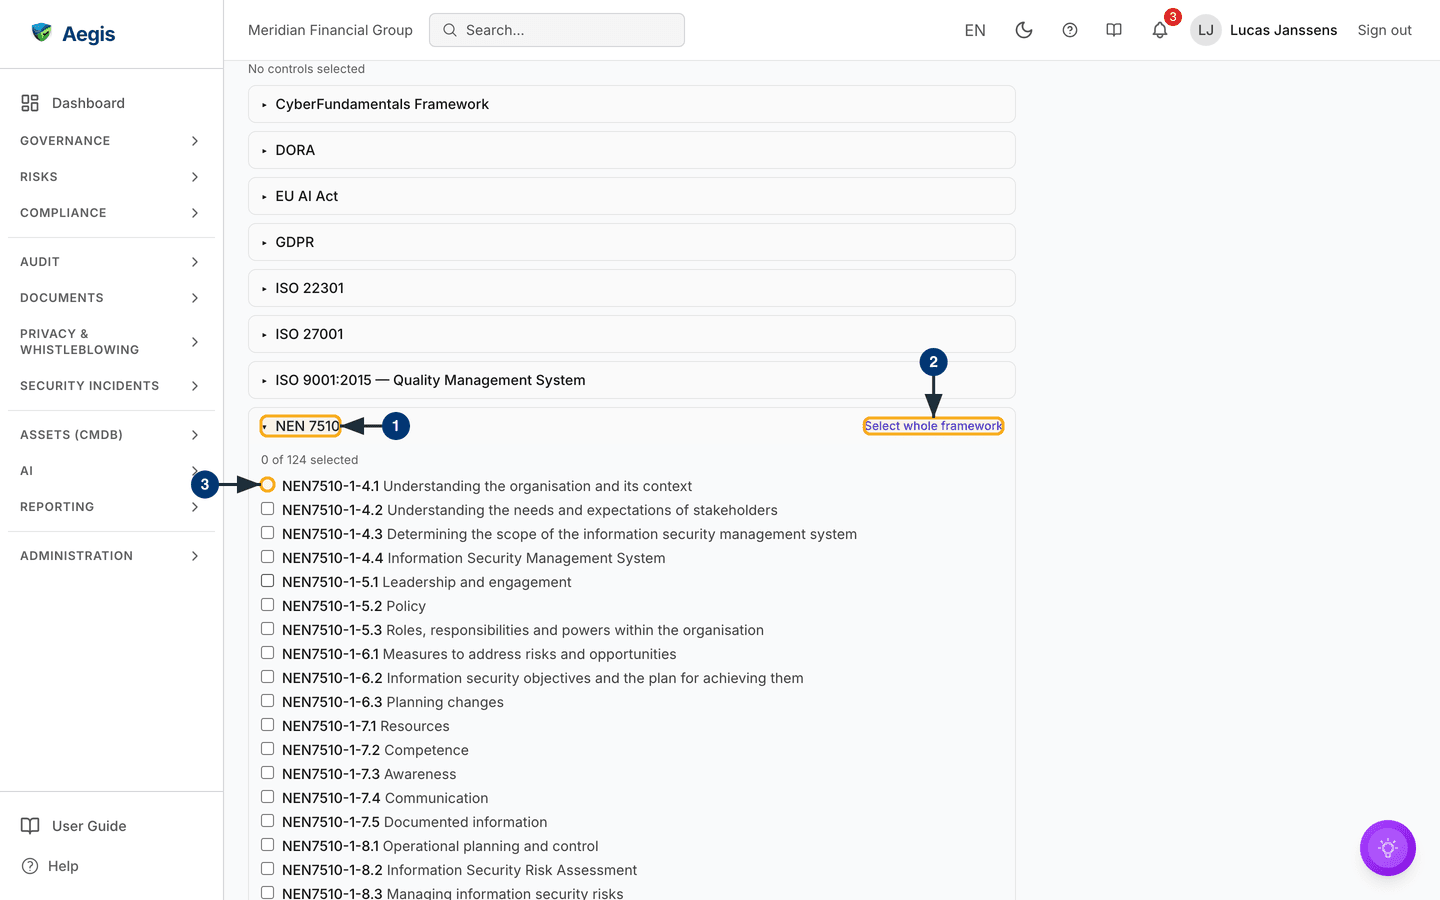
Then build the Audit scope further down the page — the part the
capture below shows. A running total above the framework groups reads
No controls selected until you tick something.
-
The picker lists your enabled frameworks as collapsed groups. Select a
framework's name, here
NEN 7510, to expand it. Its controls load at that moment, every page of them, with a count such as0 of 124 selected. -
Select
Select whole frameworkin the group header to take every control of the framework at once — all 124 for NEN 7510 on the captured screen, not only the first page. It turns intoClear frameworkwhen all are selected, and the group name shows the number selected in brackets. - Or tick individual controls; each shows its reference and title. There is no keyword search inside the picker in this release; scroll the expanded group to find a control.
Finally select Create audit. Aegis saves the engagement, confirms
with Audit created, creates one plan item per selected control, and
takes you to the new audit's detail page. Cancel returns you to the
list without saving.
You choose individual controls, so the engagement is not tied to a framework
record. The list and the detail page work the framework out from the scope:
the name of the one framework all the controls belong to,
Multiple (…) when the scope spans more than one, or
No framework when nothing is in scope yet.
The detail page at a glance
Opening an engagement shows, from top to bottom: a
Back to audits link and the engagement name, with up to three
buttons level with the name — Export package (for everyone who can
open the audit), Edit and a red-outlined Delete (for
Managers and Admins). Below come the status panel, the metadata block,
Plan items, Findings, Audit report, and
then the external-auditor panels: External auditors,
Evidence requests from auditors and
Discussion with auditors. Each is described below. No screenshot of
the detail page is included in this edition of the guide.
Move an audit through its lifecycle
An engagement runs through five stages in a fixed order. The status control sits
in its own panel at the top of the detail page: the word Status,
the current stage as a coloured badge, and a button for each stage you may move
to next.
| Status | Badge colour | Meaning |
|---|---|---|
Planned |
Slate | The engagement exists; its scope is still being worked out. |
Scoping |
Amber | In-scope controls are chosen and plan items are being prepared. |
Fieldwork |
Blue | Testers are working through the plan items and recording findings. |
Reporting |
Indigo | Fieldwork is finished and the audit report is being written and issued. |
Closed |
Emerald | The engagement is complete and kept as a read-only record of the work done. |
- Open the audit from the list. The status panel is the first thing under the engagement name, with the current stage shown as a badge.
-
Select the button for the stage you want — the label spells it out, for
example
Change status to Fieldwork. Aegis saves the change, confirms with “Status updated to Fieldwork”, and the badge and the available buttons both refresh. -
To enter
ReportingfromFieldwork, every plan item must first beCompleted, and there must be at least one. Until then that button stays disabled and an amber note reads “All plan items must be completed before reporting.” -
To enter
ClosedfromReporting, the audit report must first be issued (see “Write and issue the audit report” below). Until then theChange status to Closedbutton stays disabled and an amber note reads “An audit report must be issued before this engagement can be closed.”
You can step back to correct course — Reporting back to
Fieldwork, or Closed back to
Reporting — but you can never skip a stage. Only the adjacent
stages are offered, and the server checks the move again when you save.
Roles without the update permission see the badge and no buttons. Stepping
back from Reporting to Fieldwork while the report
is issued asks you to confirm first, because it withdraws the issue and
removes the report's signature; the engagement then cannot close until the
report is issued again.
Once an engagement is Closed, its content is locked: the plan
items, findings, report and delete controls are shown disabled, with the
note “This engagement is CLOSED and its content is read-only. Move it back
to Reporting to make corrections.” Only the audit type can still be changed
through Edit. The move back to Reporting stays
available in the status panel.
Read and work the plan items
Under the status panel sits the metadata block — Lead auditor,
Framework, Period and Report due —
followed by the Plan items section, headed with the note “One
control under test per row.”
Each row shows four things: the Control (its reference, then its
title), the Framework that control belongs to, the
Tester assigned to it (or Unassigned), and its
Status — Not started, In progress or
Completed. If you created the audit without selecting any controls,
the section shows a single notice instead: “No controls are in scope yet. Edit
the scope to add controls.”
If you hold the fieldwork (“conduct”) permission — Contributors, Managers and
Admins do — the
Tester and Status cells are dropdowns rather than
plain text. Pick a person in the Tester dropdown to assign them to
that control (or pick Unassigned to clear the assignment), and move
the item through Not started, In progress and
Completed in the Status dropdown as the fieldwork
progresses. Each change saves immediately, confirms with “Plan item updated”,
and is written to the audit log with the values before and after. Once every
item reads Completed, the
Change status to Reporting button on the status panel unlocks.
Without the permission the cells stay read-only: the tester as plain text and
the status as a coloured badge.
Record findings
The Findings section below the plan items is where the result of
the engagement lives. Its note reads “Each finding needs a severity, an owner
and a due date — and the evidence that proves it.” The table has six columns:
Finding (the title, with a link to the non-conformity it was raised
into, if any), Severity, Owner, Due date,
Follow-up status and Evidence. With nothing recorded
yet, the section reads “No findings yet. Record the first result of this
engagement.” for people who can add one.
-
Select
Add findingin the section header (fieldwork permission). ARecord findingdialogue opens. -
Fill in
Finding(what was observed, required, up to 200 characters),Description(what was tested and what fell short, required) andSeverity—Observation,Minor,MajororCritical. Missing values show inline messages such as “A finding title is required” and “Choose a severity”. -
Optionally choose an
Ownerand aDue date, theControl under testthe finding came from (orNot tied to one control), one or moreEvidencerecords, and aNon-conformityto raise it into. Linking a non-conformity records this engagement on it, so the finding is traceable from both ends. -
Select
Record finding. Aegis saves it with the follow-up statusOpen, confirms with “Finding saved.”, and the row appears in the table.
Each row carries Edit (fieldwork permission) and
Delete (Manager or Admin). Editing adds a
Follow-up status field — Open,
In progress, Resolved or Closed, all
freely selectable, because the corrective-action chain lives on the linked
non-conformity — and, where the Jira
connector is set up, a panel to link the finding to a Jira issue (see
Jira). Note that the evidence you select on
edit replaces the finding's existing evidence links rather than
adding to them. Delete asks you to confirm before removing the finding.
Write and issue the audit report
Each engagement has exactly one audit report, in the
Audit report section. Its note reads “One report per engagement.
Issuing it is what allows the audit to be closed.” A status line under the
heading shows either “Not yet issued — the engagement cannot be closed.” or who
issued it and when. Without the update permission you can read the report but
not edit it.
-
Write a
Summary(what the engagement found) and aConclusion(the overall verdict). SelectSaveat any stage to keep a draft; a summary is required before the report can be saved. -
Move the engagement to
Reporting. Only then does anIssue reportbutton appear; at any earlier stage the section notes “The report can be issued once the engagement is in Reporting.” -
Select
Issue report. Aegis saves the text, stamps your name and the date as the issuer, confirms with “Audit report issued.”, and theChange status to Closedbutton on the status panel unlocks. The issued text is now read-only. -
To correct an issued report, select
Withdraw issueand confirm. The signature is removed, the text becomes editable again, and the engagement cannot close until the report is issued again.
If someone else changes the report while you are writing, your save is refused with a message saying so; your text stays on screen, and you decide whether to reload or save again to replace theirs.
Export the engagement package
Select Export package at the top of the detail page to download the
whole engagement as a PDF — plan items, findings, the report and the linked
non-conformities. Everyone who can open the audit can download it, at any stage.
Delete an audit
-
Open the engagement you want to remove. For a Manager or Admin, a
red-outlined
Deletebutton sits at the top-right, level with the audit name. On aClosedengagement it is disabled; move it back toReportingfirst. -
Select
Delete. A confirmation dialogue asks “Delete this audit? This removes it from the list of audits.” Choose to confirm and Aegis removes the engagement, showsAudit deleted, and returns you to the list; cancel and nothing changes.
Invite an external auditor
An external auditor (your certification body, an internal-audit firm) does not need an Aegis seat to work an engagement with you. From the audit's own page you invite them by email to that engagement only. They receive a one-time sign-in link; it opens the engagement and nothing else in your Aegis, and they are never counted as a licensed user.
-
Open the audit and scroll to
External auditors. The panel appears only for people who may edit audits, invite external collaborators and read evidence — in practice Managers and Admins. -
Enter the auditor's email address and how many days the access should last
(30 by default, between 1 and 90), then choose
Send invitation. -
The auditor appears in the list as
Active, with the date access ends and when they were last active.Revoke accessends it at once, including a session they have open. Inviting the same email again re-sends the link and extends their current access to the new end date (it is never shortened) — use this when an invitation got lost or access has run out.
With the link the auditor can read the controls in scope and their testing progress, download the evidence linked to the engagement — evidence on its findings, evidence mapped to its controls, and evidence you provided for their requests — download the engagement package PDF, ask you for evidence and join the discussion. Every read, download and request is recorded in the Audit log against their invitation.
Answer evidence requests and questions
Requests the auditor raises appear under
Evidence requests from auditors, each with the control it concerns.
A Manager or Admin either chooses Provide evidence and picks an
existing record from the Evidence Locker — the auditor can then download it — or
chooses Decline and writes a reason the auditor will see. The
picker lists only evidence that has passed four-eyes review and is
Approved; a draft awaiting review, a rejected item or a superseded
version is not offered (see Evidence). If the record
stops being approved before you share it — for example because a newer version
replaced it — Aegis refuses with “Only approved evidence can be sent to the
auditor. Ask a second reviewer to approve it first.” The auditor never uploads
into your Evidence Locker. Questions and answers sit in
Discussion with auditors
below; everyone who can open the audit can read the thread.
Closing ends the auditor's access
Moving the engagement to Closed ends every invited auditor's access
immediately: their link and any open session stop working, and a nightly check
catches anything the close missed. Deleting an open engagement does the same.
Re-opening a closed engagement to Reporting restores nobody —
invite the auditor again if you need them back.
The AI assist
AI appears in one place in this module: on an open evidence request from an
auditor. Select
Suggest evidence (AI) and the AI reads the request and ranks the
Evidence Locker records you can access, each with a match percentage, its
reason, and flags such as Not approved, Superseded or
Expired. Each suggestion costs 1 AI credit.
Use this only pre-selects a record in the provide form — a person
still chooses Share evidence, and nothing is sent until they do. A
record that is not approved cannot be sent; it links to the evidence record
instead, so a second reviewer can approve it first.
The button shows only for people who may update audits and spend AI credits, and disappears while an administrator has switched AI off for the organisation. Everything else here — scoping, assigning, findings, the report and every status change — is done and decided by a person; nothing in this module moves on its own.
Tips and limits
-
Plan items track progress, not test notes. A plan item
carries a tester and a status only. Holders of the fieldwork permission
progress each plan item to
Completedstraight from the plan-items table, which is what unlocks the move toReporting. What the testing found goes intoFindings, where you can tie a finding to its control under test and link the evidence that proves it. -
Edit on the detail page.
Editon an audit's detail page swaps the metadata card for a form with the name, audit type, lead auditor, dates and the same scope picker. Removing a control from the scope also removes its plan item and its testing progress, so change the scope with care once fieldwork has started. On aClosedengagement only the audit type can be changed. - The report is the gate to closure. An engagement cannot close until its report is issued, and an issued report cannot be edited until its issue is withdrawn. Keep the underlying proof in Evidence and link it to the findings it supports.
- Nothing here is silent. Every create, status change and delete is written to the Audit log, and a status change records the values before and after the move, so the history of the engagement survives the engagement itself. The list itself pages at twenty rows.
Where this connects
- Audit readiness — check how prepared you are before, or alongside, running an engagement here.
- Mock audit — rehearse the questions an auditor will ask.
- Compliance frameworks — the source of every control you can put in an audit's scope.
- Evidence — the proof a tester relies on when working a plan item, and the records you link to findings and share with auditors.
- Non-conformities — where a finding's corrective action is followed up.
- Control monitoring — continuous checks that complement a point-in-time audit.
- Scenario: an external audit — the whole journey across the modules involved.