Scenario: responding to a security incident
A suspicious login is spotted at nine in the morning, and the next seventy-two hours decide whether you meet your reporting deadlines — this chapter walks the screens in the order you will actually open them.
An incident (a security event that has
already happened, as opposed to a risk, which is something that might) is
logged, worked and closed in the Incidents module.
A real response, though, crosses several surfaces: the register at
/incidents, the quick-view panel that a row click opens over it,
the Report New Incident page at /incidents/new, the
full incident detail page at /incidents/{id}, the NIS2 significance
wizard that opens from that page, and — for managers — the cross-incident
dashboard at /incidents/reporting. The register's eye icon (or the
title link) and a click elsewhere on the row go to different places, and it
matters: the two surfaces do not carry the same controls. We follow one event
from detection to closure with two people in it: Marcus, a
Contributor, who spots the
unauthorised access and works the case, and Lena, a
Manager, who confirms the data
breach, rules on whether it is a NIS2-significant incident and records what was
sent to the authority. NIS2 is a European cybersecurity law with staged
mandatory reporting; GDPR is the EU data-protection law, with its own 72-hour
breach-notification window.
Aegis works out which deadlines apply, counts them down from the detection
time, assembles a draft you can read, and records when you mark a filing as
done. Sending the report to the authority — and deciding whether to report
at all — stays with a named person in your organisation. The
Regulatory Notifications panel says exactly that on screen:
drafts are generated for review only, Aegis never transmits to an authority,
and the exact field mappings need sign-off from your data protection officer
or legal team.
Who does what in this scenario
Reading the register is open to every role, including
Viewer — and so is the
Export bulk action, which is gated on read permission rather than
on write. Logging an incident, moving its status, adding timeline entries,
sending communications, starting a playbook, generating regulatory drafts and
running the significance wizard need
Contributor or higher; a
Viewer sees the detail page without those buttons.
A small set of actions are decisions of record and belong to
Manager and
Admin only: confirming or dismissing
a suspected data breach, Record GDPR Notification, marking the GDPR
authority filing as filed, and recording the reporting decision. The same two
roles see the reporting dashboard, the overdue banner that crosses the top of
every page, and the delete icon in the register; a Contributor who opens
/incidents/reporting is sent back to the register. The full matrix
is in What each role can do.
What's on this screen
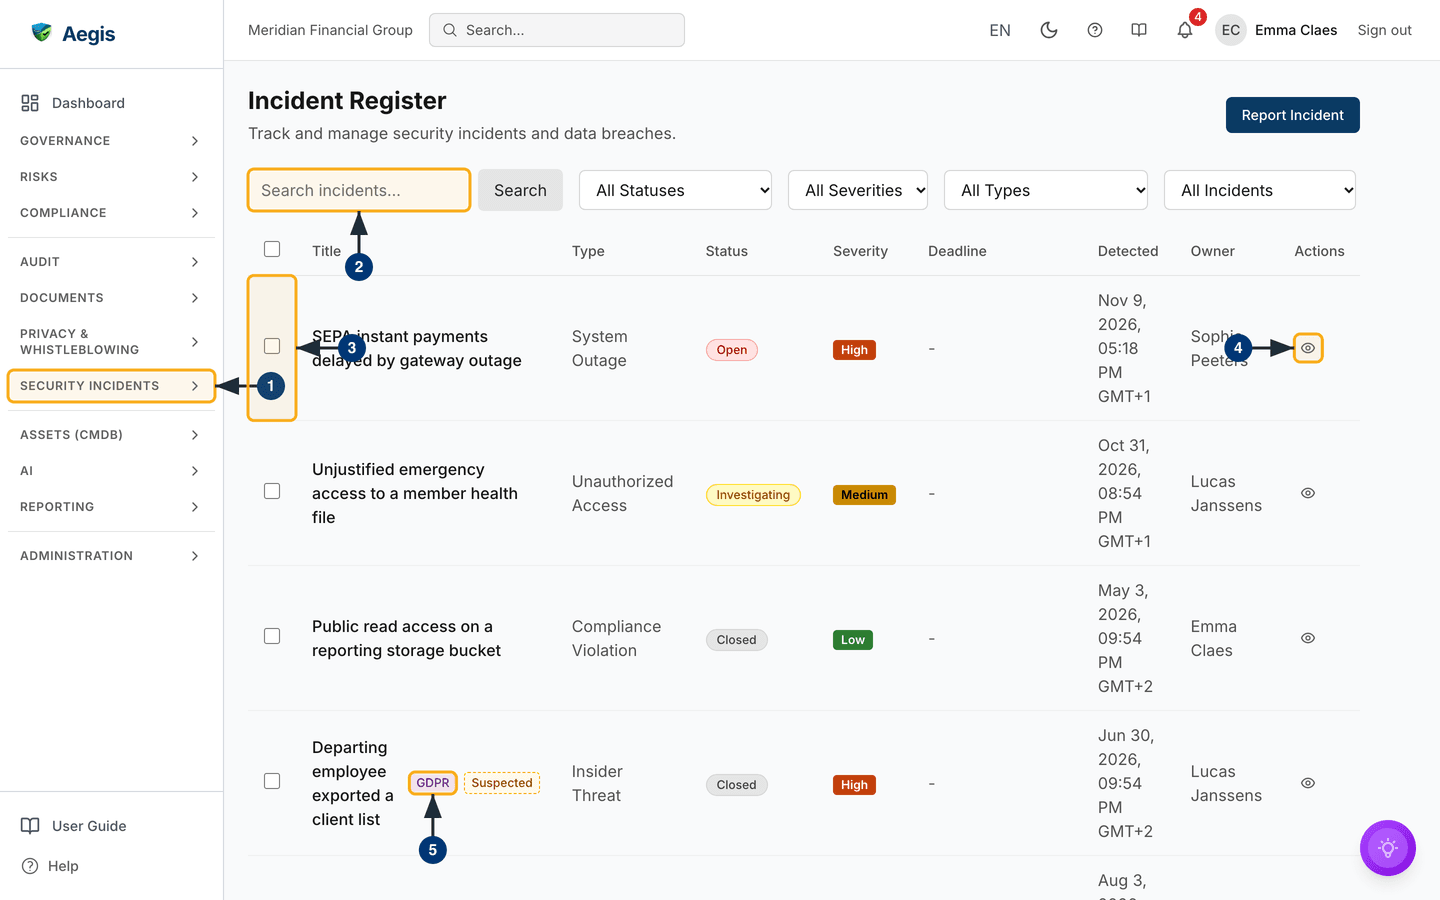
The journey starts on the Incident Register, reached from the
Security Incidents group in the left menu. The heading sits over
the line "Track and manage security incidents and data breaches.", and the
primary action — the dark blue Report Incident button — is at the
far top right. It is a link: it opens the Report New Incident page
rather than a dialog over the register.
One filter row runs beneath it: a Search incidents... box with its
own Search button, then three dropdowns reading
All Statuses, All Severities and
All Types, and a fourth reading Any breach status that
isolates data breaches (Data Breaches Only or
Non-Data Breaches). Besides the five individual statuses, the
status dropdown offers Open (not resolved), which shows every
incident that is not yet resolved or closed — the same set the dashboard's
open-incidents tile counts. The filters combine with AND.
The table begins with a selection checkbox column — that is what feeds
Export — then runs Title, Type,
Status, Severity, Deadline,
Detected, Owner and Actions.
Status and severity are coloured chips. The title cell can carry two small
badges: a purple GDPR badge on any incident flagged as a data
breach (it turns red and reads GDPR! once the 72-hour window has
passed with no notification recorded), and a dashed amber
Suspected badge while no manager has yet confirmed that breach.
Deadline is the cell to watch: when a reporting stage is
outstanding it shows a framework chip (GDPR, NIS2 or,
where DORA is switched on, DORA) and a countdown to the nearest
stage, orange inside 24 hours and red with a negative figure once the window has
passed, plus a small +n marker — hover it for "+n more deadline(s)"
— when further stages are still waiting. A deadline on a suspected breach also
carries a dashed Provisional tag. In the captured screen, taken as
a Contributor against seeded demo data, every visible row shows a dash in
Deadline, including the closed row that carries both the
GDPR and Suspected badges: nothing on those incidents
is still being counted down. A dash is about deadlines, not about status — the
top row in the capture is still Open.
Actions holds an eye icon (View details) that
opens the full detail page, as does the title link; a delete icon appears there
for Admin and
Manager, and is absent from this
Contributor capture. Clicking anywhere else on the row opens the quick-view
panel instead. Both surfaces carry Add Entry and the
Close Incident dialog. Below the table, a footer links to the
user-guide chapters on regulatory reporting and on handling an incident.
Step 1 — Find the register, and look before you log
Marcus's first move is not to create anything. Two records for one event split the timeline in half and make the countdowns ambiguous, so he checks whether a colleague has already reported it.
-
Open
Security Incidentsin the left menu and chooseIncidents. TheIncident Registerloads with the most recently created records at the top. The order follows when each record was logged, not when the event was detected, so theDetectedcolumn will not read as a straight sequence down the page. -
Type a distinguishing word into
Search incidents...— a hostname, a system name — and selectSearch. The table reloads with only matching titles; the search runs against the title, not the description. Filters are not written back to the address bar, so a link you copy will not carry them; a?search=link is the exception, because the search box is seeded from it on load. -
If that is still too broad, narrow it with the
All StatusesandAll Typesdropdowns; the table refreshes as each filter is applied. To hand the shortlist to a colleague, tick the checkbox at the start of each row you want and chooseExport: the selected incidents download as a CSV file. -
Read any matching row across. The
StatusandSeveritychips show how far the response has got, andDeadlineshows whether a reporting window is already running. If the event is on record, select the eye icon underActions. The detail page opens at/incidents/{id}with the full timeline — join that response rather than starting a second one. -
Check the title cell for badges.
GDPRmeans the incident is flagged as a personal data breach;Suspectedbeside it means that flag still awaits a manager's confirmation; a redGDPR!means the 72-hour window has run out with no notification recorded.
If nothing matches, select Report Incident at the top right. The
Report New Incident page opens at /incidents/new.
Step 2 — Get the event on record
The form is deliberately short. During a live response you want the record open
within minutes; the rest goes onto the timeline as you learn it. It sits on its
own page, with a breadcrumb back to the Incident Register, and is
split into an Incident Details card, a
Detection & Impact card and a data-breach box.
-
Enter an
Incident Titlea colleague would recognise. With the detection time further down, it is one of only two entries the form insists on: theReport Incidentbutton stays greyed out until both are filled in.Incident TypeandSeverityare marked required too, but they arrive pre-set toOtherandMedium, so change them on purpose rather than by omission. -
Use
Descriptionfor what you know so far — what happened, and how it came to light. It can stay thin at this stage. -
Choose the
Incident Type; Marcus picksUnauthorized Access. Type matters later:Data Breach,System CompromiseandUnauthorized Accesscount as high-risk types in the NIS2 checks. -
Set
SeveritytoHigh. Each option carries a one-line description, and severity can be revised as the picture changes. -
Fill in
When was the incident detected?with the moment the event was first observed. The help text under the field states plainly that this timestamp drives the GDPR 72-hour calculation. A time in the future is rejected. -
List machines and services in
Affected Systems, separated by commas. They appear as tag chips on the detail page, and "at least one affected system" is one of the four automatic NIS2 checks. -
Tick
This incident involves a personal data breachif personal data may have been accessed, disclosed or lost. ANumber of Data Subjects Affectedfield appears beneath it for an estimate. The help text explains what the tick does: the incident is recorded as a suspected breach until a manager confirms it, and the GDPR Article 33 72-hour deadline runs provisionally from detection in the meantime. -
Select
Report Incident. A confirmation reads "Incident reported successfully" and Aegis takes you straight to the new incident's detail page, inOpenstatus with your name as owner.Cancelreturns to the register without saving.
Every NIS2 stage and the GDPR window are counted from Detected,
not from when the record was created. An incident logged two days late must
still carry its true detection time, or the countdowns will be wrong in your
favour — the worst direction for them to be wrong in.
Step 3 — Open the investigation and keep a running account
-
On the detail page, find the status actions at the top right. Only
transitions that are valid from the current status are offered, so from
Openthe buttons readMark investigating,Mark containedandMark closed. Marcus selectsMark investigating: the status chip changes and the transition is stamped onto the timeline with his name and the time. If a colleague changed the status in another tab first, Aegis refuses the stale change and shows the current status and its buttons instead. -
To add an account of your own, select
Add Entryin theActivity Timelineon the same page: write what you have found in the entry box and confirm. The note appears at once, attributed and timestamped — this is the account an auditor will read, and it cannot be reconstructed honestly afterwards. The quick-view panel opened by clicking a register row carries the sameAdd Entrybutton. -
Use
Communicationsto tell colleagues. Internal messages go out directly; anything with theExternalaudience — customers, regulators or the public — runsCreate draft→Approve→Send, so no external statement leaves on one person's say-so. An external message can be markedAddressed to an authoritywith the authority's name, which also lists it among the submissions further down the page. -
If your organisation works from a response checklist, open
Response Playbookslower on the page, choose aPlaybook template(the incident-response playbook is the default) or type a custom title, and selectStart playbook. The playbook is listed with its status and percentage complete, and links through to the full playbook in Playbooks.
Step 4 — Confirm the breach and decide whether it is NIS2 significant
Because Marcus ticked the data-breach box, the detail page opens with a
Suspected data breach alert: the flag stands, but no manager has
confirmed it, and the GDPR clock runs from detection as a precaution. The
sidebar panel reads Suspected Data Breach and its
GDPR Deadline is marked provisional. Confirming it is Lena's job.
In the GDPR alert she selects Confirm breach; this records her
decision, keeps the 72-hour deadline from detection and starts the breach
notifications and workflows. If the data turns out not to be personal data,
Dismiss asks for a reason of at least ten characters, then clears
the flag and its deadline. Dismissing is no longer offered once the authority
notification has been recorded. These two buttons appear only to Managers and
Admins, and only where GDPR automation is part of your plan.
The NIS2 call is what starts the regulatory clocks for the cybersecurity side.
The wizard opens from the AI Analysis panel in the right-hand
column of the detail page — Assess Significance while no assessment
exists, Open Full Assessment once one has run — and the
NIS2 Significance Assessment it opens walks the call in three
steps. Any Contributor or higher can save the decision; in this scenario Lena
makes it.
-
Automatic checks. Four indicators are evaluated from the
incident's own data and marked
YESorNO: high or critical severity, the data-breach flag, at least one affected system, and a high-risk incident type. A summary line reports how many of the four are met. -
AI assessment. Select
Run AI Assessmentfor a second reading, orSkip to Decision. The assessment returnsLikely SignificantorNot Significantwith a confidence percentage and reasoning against the two NIS2 criteria. -
Decision. Lena chooses
Mark as Significant— its hint reads "Activates NIS2 reporting deadlines." — writes a justification, checks theNIS2 Reporting Deadlinespreview, and confirms. The alternative,Not Significant, records the decision and the reasoning without starting a clock. If your organisation is registered as a trust service provider, the decision step also offers a box for incidents that affect your trust services, which shortens the notification stage to 24 hours.
Once an incident is flagged significant, the panel shows
Review Significance Decision instead. That reopens the wizard,
which is the only way to withdraw a significance decision that turns out to be
wrong.
Step 5 — Work the deadlines
From that moment the detail page carries a
NIS2 Significant Incident — Reporting Required alert listing the
stages: an early warning at 24 hours, an incident notification at 72 hours, an
intermediate report that has no fixed date because it is sent only when the
authority asks for it, and a final report one month after the 72-hour
notification deadline. If the incident is still being handled when the final
report falls due, a progress report row appears in its place under Article
23(4)(e). Because the breach was confirmed, a GDPR alert runs alongside it,
quoting Article 33 with the time remaining in the 72-hour window, and a breach
countdown sits below the header.
-
Find
Regulatory Notificationsfurther down the detail page — the section appears once the incident is flagged as a data breach or marked significant. Authorities and deadlines are modelled for Belgium, the Netherlands, Luxembourg, France and Germany; for any other member state the panel says plainly that it is not modelled and that you must determine the authority yourself. The Belgian cards —GBAfor the personal data breach notification under GDPR Article 33, andCCBfor the NIS2 Article 23 staged report — appear only when Belgium is configured, chosen for the incident, or already has a filing. -
Select
Generate draftagainst the stage that is due. Aegis assembles the fields it holds into a draft you can read on screen and copy. If no data protection officer is configured, the GBA card warns that the contact-point field will be flagged as missing. - File the notification through the authority's own channel. Aegis transmits nothing.
-
Come back and select
Mark as filed. TheMark notification as fileddialog asks for the reference the authority gave you and forSubmitted to the authority at, which defaults to now — change it when you record a submission made earlier; it cannot be before detection or in the future. Confirm, and the stage flips toFiledwith that reference shown beside it. Marking a CCB stage is open to Contributors; marking the GBA filing is a Manager or Admin action, because it also records the incident's GDPR notification. -
For GDPR there is also a direct control:
Record GDPR Notification, which sits with the status actions while the breach is unnotified and is shown to Managers and Admins only. It opens aRecord GDPR notificationdialog with an optionalAuthority notifiedfield and the sameSubmitted to the authority attime, so a late recording no longer reads as a late notification. Use it even when the notification went out entirely outside Aegis — the point is the audit trail. Where the organisation decides not to notify at all, Lena records that in theReporting Decisionpanel with a reason; the GDPR alert then reads "Not to be notified to the supervisory authority" and no 72-hour deadline applies. -
When the authority confirms receipt, record it in
Authority acknowledgements, which lists every submission with its receipt state —Awaiting receipt,Receipt overdueorAcknowledged.Record receipt,CorrectandWithdraweach add a new version and keep the earlier ones;CopyandExport CSVtake the list out. An overdue receipt is a reminder to follow up, not a breach by you or by the authority. -
Lena watches the whole portfolio from the
Incident Reporting Dashboard. Counters across the top showOverdue,Due within 24h,On TrackandTotal Active; a filter switches between all frameworks, NIS2 and GDPR; and theActive Deadlinestable runsIncident,Framework,Stage,Deadline— a countdown — andStatus, each row ending in aViewlink into the case. A completed-notifications section below records which filings went in on time and which were late. -
If a stage goes overdue or falls inside 24 hours, a coloured banner appears
at the top of every page for Managers and Admins, naming the framework, the
stage and the incident, with
ViewandDashboardlinks.Dismiss bannerhides it for half an hour; it does not clear the obligation.
Step 6 — Contain, resolve, close
-
Once the threat has been stopped from spreading, select
Mark contained. The containment timestamp is written into theTimelinepanel of key dates in the right-hand column, besideDetected,Reported,ResolvedandClosed. -
When the root cause has been dealt with and normal service is back, select
Mark resolved. Should the problem return,Mark investigatingis offered again fromContainedandResolved. -
Select
Mark closed. AClose Incidentconfirmation opens with two optional fields:Resolution Summary (Optional), saved as the incident's remediation, andLessons Learned (Optional), saved as its lessons learned. Text already stored in either field is shown so you can keep or extend it. -
Confirm. The status moves to
Closedand the closure timestamp is set.Closedis terminal, so anything discovered later goes on the timeline as a new entry rather than reopening the case.
The close step asks for a resolution summary and lessons learned but requires neither. Root cause is a separate section that appears on the detail page only once it holds content, and as shipped there is no on-screen field for filling it in, so these two fields are the post-incident text Aegis actually captures through the interface. Treat them as required by your own policy, even though the software will let them through empty. Closing also does not wait for outstanding filings: check the deadlines first.
The AI assist
Two AI features touch this journey, and neither of them decides anything. The
AI Analysis panel offers Run AI Assessment, returning
a Likely Significant or Not Significant verdict with a
confidence figure, per-criterion reasoning, the frameworks it believes apply and
recommended actions; it can also draft the text of a reporting stage (Draft Early Warning, Draft Notification and so on) and show how much of the required
NIS2 field set is covered. A deeper pass, Deep AI Triage in the
AI Incident Triage panel, runs a broader read across NIS2, GDPR and
DORA significance, whether personal data is involved, which stages apply,
related risks, assets and controls, and prioritised immediate actions. Its own
on-screen note is the honest summary: it reads internal records only, typically
takes thirty to ninety seconds, and its conclusions must be confirmed by a
person. The clocks start when Lena confirms the decision in the wizard, never
when the AI returns a verdict. The AI triggers spend AI credits and need a role
allowed to run AI actions; if AI is switched off for your licence, the four
automatic checks and the decision step still work exactly as described above.
What to take away
- Search the register before logging — one event, one record, one timeline.
-
Get
Detectedright; every countdown is measured from that moment. - A ticked data-breach box is a suspicion until a manager confirms or dismisses it — but its 72-hour clock is already running.
- Write the timeline as you go, not afterwards.
- Filing stays manual. Aegis drafts, counts down and records; a named person decides, submits, and enters the reference and the time it reached the authority.
-
A dash in
Deadlinemeans nothing is outstanding — it does not mean closed. -
Add Entryand theClose Incidentdialog are on both the full detail page and the quick-view panel opened by clicking a register row.
Where this connects
The complete module reference is in Incidents, and the manager view in Incident reporting. To have incidents opened from connector alerts instead of by hand, see Auto-incident rules and Connectors; a linked Jira issue appears in the detail page's sidebar (see Jira), and incidents raised from data-loss alerts carry their own panel, covered in Data loss. To trigger follow-up tasks automatically, see Workflows, Playbooks and Action items. The data-breach side continues in GDPR, and financial-sector reporting has its own rules and an Article 18 classification panel on the detail page, described in DORA. Affected machines and services come from the CMDB, and a recurring cause belongs in Risks. Every status change, notification and timeline entry here is written to the Audit log. For who may confirm a breach, record a notification and reach the reporting dashboard, see What each role can do.