Vendors
A register of every third party you rely on, with a risk rating and a review date for each, so your supply-chain due diligence is on record when an auditor asks.
Keep suppliers, cloud providers, contractors and service partners here, with the risk each one carries. Most frameworks expect it: ISO 27001 (an international information-security standard), NIS2 (a European cybersecurity law) and DORA (a European law for financial-sector operational resilience) all ask you to manage third-party risk (the risk that a supplier's failure or breach becomes yours).
This chapter is the screen-by-screen reference. To see the whole journey worked as a story — from "we want to use this supplier" to a rated, monitored vendor — see the full walkthrough in Scenario: onboard and risk-rate a vendor.
Who uses it
-
Viewer can search, filter and
open a vendor. In the
Actionscolumn a Viewer sees one view (eye) icon instead of three, but may tick rows and use the bulkExport— the report-export permission Viewer holds. A Viewer cannot start AI actions or add vendors, soSmart Triage (AI)andImportdo not appear, and opening/vendors/newdirectly sends a Viewer to the access-denied page. -
Contributor can also add
and import vendors, run an AI investigation, send a questionnaire,
deactivate or reactivate a vendor and change status in bulk — but not
export, so no
Exportaction appears for that role. - Manager and Admin can do all of that, export the selection, and delete vendors in bulk as well.
What's on this screen
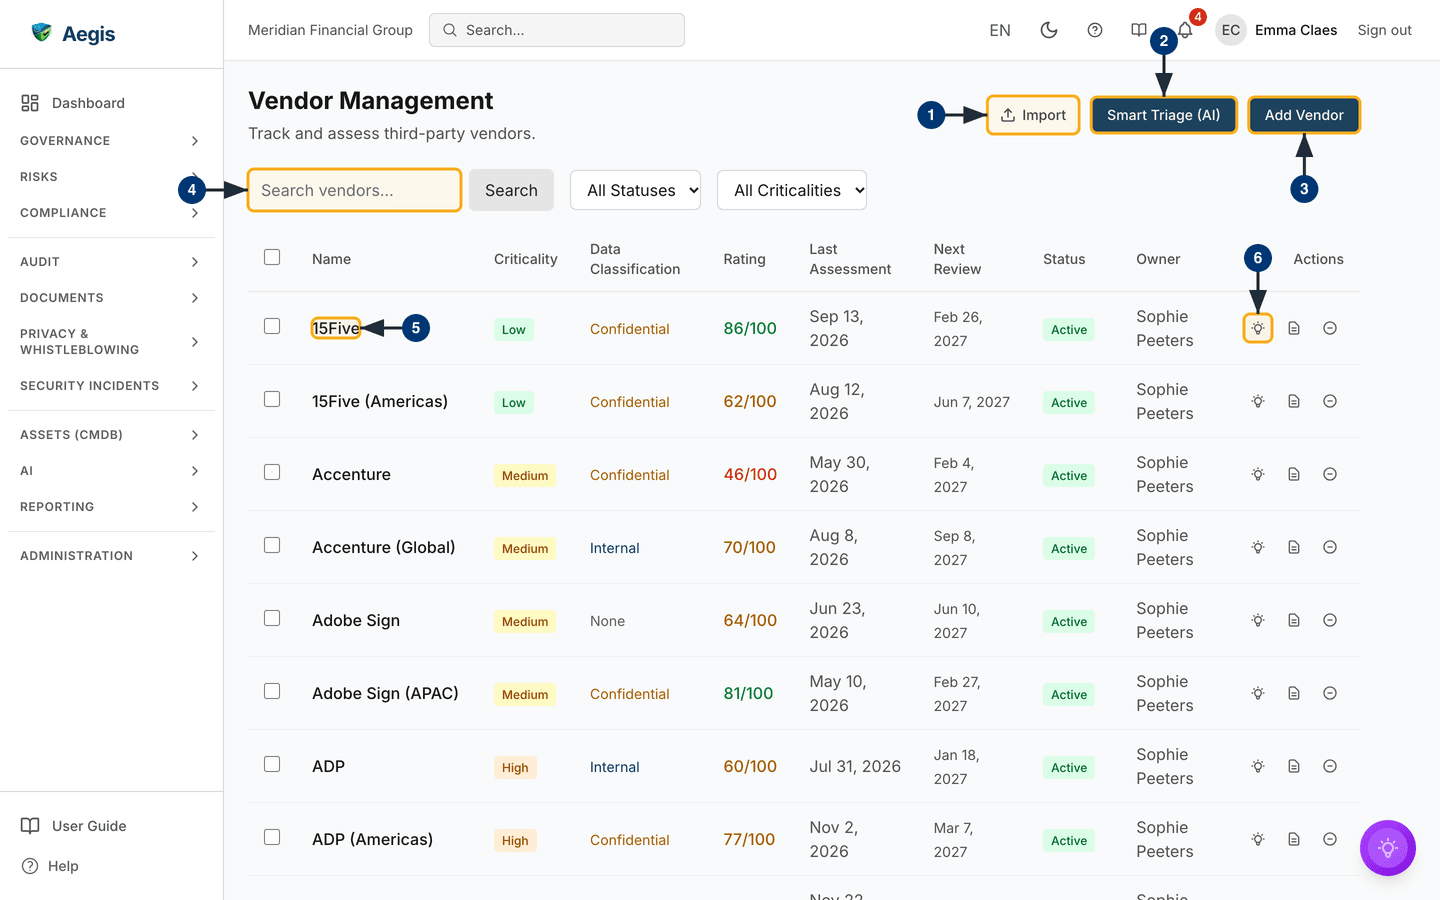
Open /vendors from the Risks group in the left
sidebar. The heading Vendor Management sits top left with the
subtitle Track and assess third-party vendors. On the same row, to the
right, are three buttons: the outlined Import, the dark blue
Smart Triage (AI) and the dark blue Add Vendor.
Under the heading is the filter bar: a Search vendors… box with a
Search button beside it, an All Statuses dropdown
(Active, Inactive) and an
All Criticalities dropdown. Then the register table, with a tick
box in the header row and on each row for the bulk actions. Left to right the
columns are the select box, Name (a link that opens the vendor),
Criticality, Data Classification, Rating,
Last Assessment, Next Review, Status,
Owner and Actions. In a narrow window the table
scrolls sideways, with a soft shadow at the edge to show there is more.
Criticality shows as a coloured chip and ratings are coloured by score band; in
the captured screen the visible rows are all Active and rated, from
86/100 in green down to 46/100 in red. A vendor never
assessed shows a dash under Rating and Not scheduled under
Next Review. If your register is empty, the table shows an empty
state and you begin at step 3. A Portfolio Report card, a
Concentration Risk panel, saved AI briefings and the action
items raised from them sit below the table, off the bottom of the screenshot.
-
Select
Importto bring in a list from a spreadsheet. The Import vendors dialog opens. -
Select
Smart Triage (AI)to ask which vendors need reassessing first. A modal opens with aRun Smart Triagebutton. -
Select
Add Vendorto create one by hand. The browser moves to the Add New Vendor page at/vendors/new. -
Type a name into
Search vendors…and selectSearch. The table redraws with only the matching vendors; the two dropdowns narrow it further. -
Select a vendor's
Name. Its detail page opens at/vendors/{id}. -
Use the three icons in a row's
Actionscell to act without leaving the list: the lightbulb runs an AI investigation, the document icon sends a questionnaire, and the circle icon deactivates the vendor (a circle with a minus) or reactivates it (a circle with a tick). Each opens its own dialog.
Adding a vendor
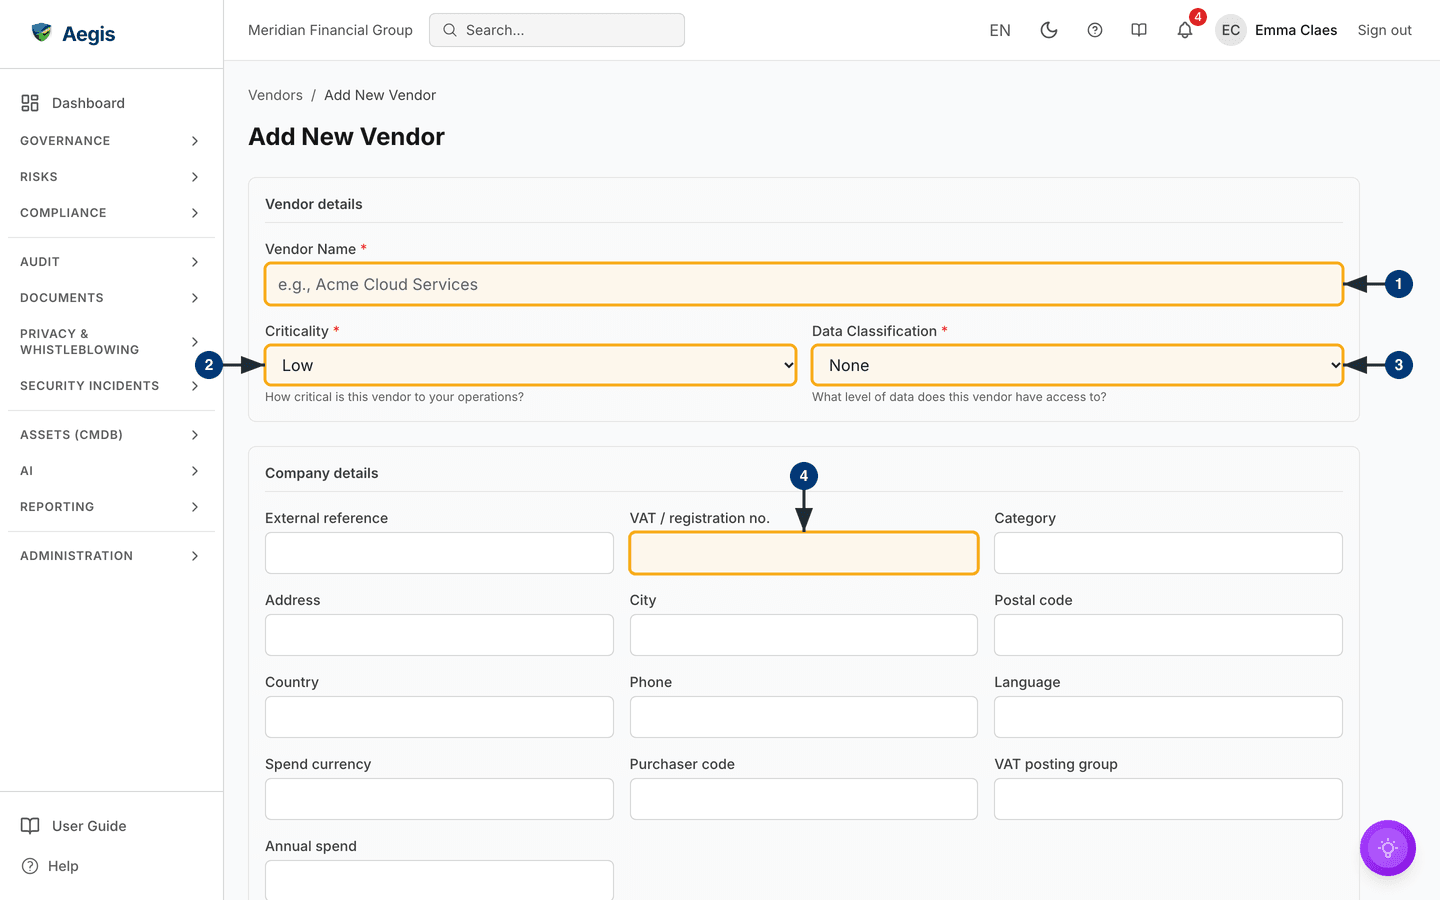
Adding a vendor is a full page, not a pop-up. The breadcrumb reads
Vendors / Add New Vendor. Three fields in the
Vendor details card are marked required; the
Company details card underneath is optional.
-
Enter the
Vendor Name. It is the only field that blocks you if left blank: the page shows Vendor name is required under it. -
Choose a
Criticality. It starts onLow; the list runsLow,Medium,High,Critical. The hint underneath asks how critical the vendor is to your operations. -
Choose a
Data Classification. It starts onNone; the list runsNone,Internal,Confidential,Restricted. The hint asks what level of data the vendor can reach. -
Enter the
VAT / registration no.if you have it: the financial screening searches on the registration number. Fill in the rest of Company details as you can —External reference,Category,Address,City,Postal code,Country,Phone,Language,Spend currency,Purchaser code,VAT posting groupandAnnual spend.
Below the fold, under Annual spend, a tick box marks the vendor
In scope for supplier assessment. At the foot of the page, select
Add Vendor to save (it reads Creating… while it works) or
Cancel to discard. On save a confirmation appears and the browser
opens the new vendor's detail page, ready for you to schedule a review and add
contacts.
Criticality is how badly a failure would hurt you; Data Classification is what data the vendor can touch. Criticality also sets the default review interval and leads the Smart Triage ordering, so set it honestly.
Further down, the Privacy & security (GDPR/NIS2) section
holds the supplier details GDPR Article 28 and NIS2 Article 21(2)(d) ask for:
Website, Contact name, Contact email,
Service provided,
Data processing agreement in place (Yes,
No or Unknown) and DPA signed on,
Processing locations (countries),
Transfers outside the EEA and their Transfer basis,
Certifications held, Exit plan and Notes.
All are optional; separate several countries or certifications with a comma or
semicolon.
Importing a list of vendors
-
Select
Import, thenDownload templatein the dialog. An.xlsxtemplate downloads with the columns Aegis expects. OpenColumns and accepted valuesin the dialog for every column's exact header, whether it is required, the values it accepts and an example; a.csvupload must use the same headers on line 1. The privacy and security details have columns too: yes/no values, dates asYYYY-MM-DD, and lists separated by semicolons. -
Fill it in, choose your file, and select
Validate. A summary appears — valid rows, error rows, and a line per bad row saying what is wrong. Nothing is written yet. -
Fix the errors, re-validate, then select
Import. Only clean rows are imported, and a confirmation says how many vendors were created and updated. The register, the Portfolio Report card and the Concentration Risk panel refresh without a page reload.
A row whose External ref (or, when that is blank or unknown,
its Registration no) matches a vendor you already hold updates
that vendor instead of adding a copy. Only the cells you fill in change;
blank cells keep the stored value. A key that matches more than one vendor,
or appears twice in the file, is reported as a row error.
Working a vendor from its detail page
Under the breadcrumb sit the vendor name, its status chip, the date it was last
updated and a row of action buttons, with Raise non-conformity on
the far right. Then the Compliance Rollup and
Supply Chain Graph side by side, and the
Managed Relationships list. Below the fold: the current rating,
assessment history, questionnaire requests, contact persons, linked evidence,
risks and roadmap work, services, security standards, data flows, and side
panels of details, statistics, company details, privacy and security, and dates.
-
Select
AI Analysisto score the vendor from the record Aegis already holds. The button shows Analyzing… while it runs, with a note that it can take a few minutes. When it finishes, an AI Analysis panel opens beneath the buttons. -
Select
Deep Investigationto run the external background check described under The AI assist below. A dialog opens and stays open while it works. -
Select
Schedule reviewto set when this vendor comes round again. A dialog asks for aReview interval (days); leave it empty and the interval follows the criticality. OnSchedulethe date is set that many days out and appears in the register'sNext Reviewcolumn. -
Select
Recompute risk scoreto re-derive the rating. It reads Recomputing…, then a message reports the new score and tier. -
Select
Raise non-conformityfor something that has gone wrong with this supplier, rather than a risk you are still watching. The non-conformity form opens with the supplier as its source and a title already filled in. -
Read Compliance Rollup for the picture across this vendor's
supply chain — an
Overall Riskbadge and counts ofDependencies,Critical DependenciesandHigh Risk Dependencies— with the Supply Chain Graph beside it drawing the same thing. In the captured screen no dependency has been recorded, so the badge readsLow, all three counts are0, and the graph holds the single vendor node.
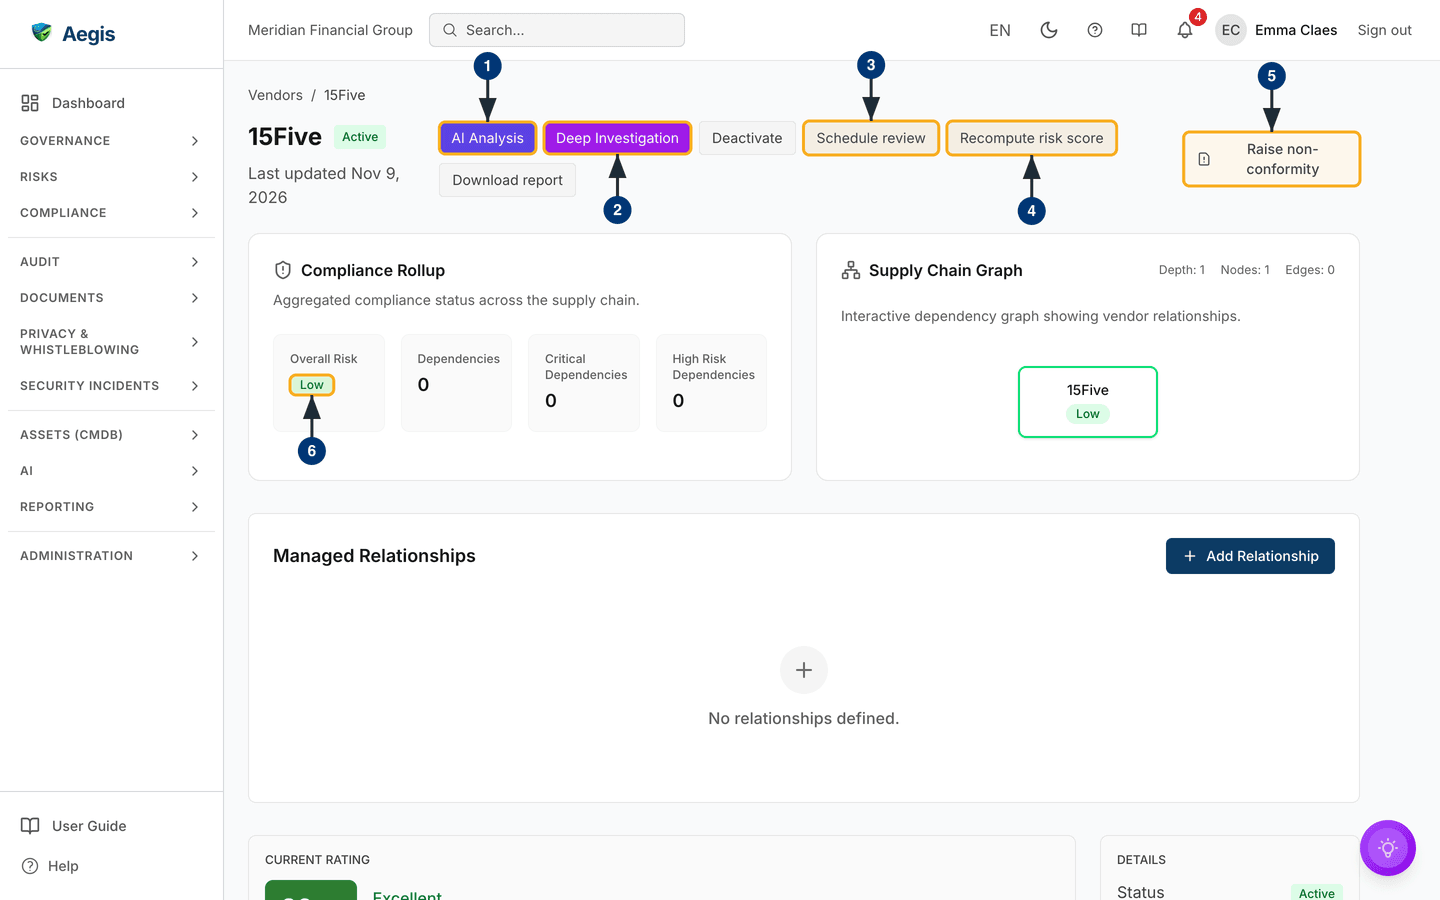
Two more buttons sit in that row. Deactivate sets the vendor to
Inactive after a confirmation (it reads Activate for
one already inactive); Download report saves a per-vendor report.
The AI Analysis panel appears only once an analysis exists, so
it is absent from the captured screen. It carries badges for the suggested
score, risk level, number of suggestions and confidence; its sections open to
show the security findings, compliance gaps, data-handling risks, DPA analysis
and recommendations behind that score. A Copy analysis button
copies it, marked as AI output with its generation time and confidence. None of
it is applied until you act.
Financial & KYC Screening shows the credit rating and sanctions/PEP (politically exposed person) results above the Compliance Rollup. It appears only when your licence includes the Creditsafe integration and your operator has configured it; otherwise the card is not shown at all, as in the captured screen.
The Privacy & security (GDPR/NIS2) card on the detail page
shows those supplier details; select Edit privacy & security to
change them in a dialog (the button appears only when you may update vendors).
When the GDPR register holds a data processing agreement for this vendor and you
may read it, the card shows it under
DPA in the GDPR register (authoritative), and that record takes
precedence over the DPA fields typed on the vendor. The
Company details card shows the master data entered at creation
and lets anyone who may update vendors edit it.
The current rating, explained
An assessment is one scored evaluation at a point in time; the
rating is the score currently held. Each assessment updates the
rating and the history stays, so you can see whether a vendor is improving or
slipping. With no rating, the register shows a dash and the page reads
Not Assessed. When the rating comes from an assessment scored under
your organisation's scoring method, the card shows that method's band name;
otherwise it uses the fixed labels below.
| Score | Label |
|---|---|
| 80–100 | Excellent |
| 60–79 | Good |
| 40–59 | Fair |
| Below 40 | Poor |
Recording supply-chain relationships
The Managed Relationships card lists the vendors this vendor depends on — its sub-processors and sub-suppliers. With none recorded it reads No relationships defined., as in the captured screen.
-
Select
Add Relationship. A dialog opens with aChild Vendorlist of the vendors in your register. -
Choose the
Relationship Type—Sub-processor,Sub-supplier,Hosting Provider,Data ProcessororOther— and, if you want, aCriticality, aDescriptionand theData Shared. - Save. The relationship appears in the list with edit and delete controls, and the Compliance Rollup counts and Supply Chain Graph take it into account.
Only people who may update vendors see the add, edit and delete controls; everyone else sees the list read-only.
Contact persons
The Contact persons card holds the people you deal with at the
vendor. Add one with a name, an email address and a
Preferred language (Dutch, French or
English), then select Add contact. One contact can be
marked Primary for questionnaires with Make primary:
questionnaire campaigns go to that person in their preferred language. A vendor
with no primary contact is skipped by campaigns, and the card says so.
Requesting an assessment
-
Select the document icon in the vendor's
Actionscell. The Send Assessment Questionnaire dialog opens, showing the vendor it is sending to. -
Choose an email request template under
Select Questionnaire Template. These choices are separate from the Questionnaires module. -
Enter the
Recipient Emailand, if you want, a custom message, then selectSend Questionnaire. The request is recorded with its own reference and delivery state. This email asks the contact to reply; it creates no response portal or scored assessment.
A request changes no rating, assessment date, review date or risk snapshot. On the vendor detail page, Questionnaire requests shows separate request history. Refresh to read the stored state. SENT means the email service accepted the message, not confirmed recipient delivery. READY has no confirmed sending claim; SENDING and UNKNOWN require verification. NOT_SENT records no transport attempt. Uncertain attempts are never automatically resent; check the outcome before making another request.
Completed assessment quality runs from 0 to 100, higher better; zero is valid. Assessment saves use the latest completed score. Recompute risk score uses the inverse of a weighted risk calculation, so it may differ from the raw assessment score. Confirmed historical requests are excluded only after explicit provenance review; ambiguous historical records remain unchanged.
The browser remembers the request identity across reloads in private session storage, without storing recipient or message text. Retrying uses that same identity. Start new request explicitly prepares a fresh attempt but does not send it; check uncertain delivery before using it.
When your licence includes questionnaire automation, a separate
Questionnaires
panel on the detail page lists every campaign round sent to this vendor, with
the score trend, the approval summary, open actions still awaiting a person, and
— if you may send campaigns — a
Send questionnaire shortcut into the campaign wizard. See
Questionnaires.
Deactivating and reactivating a vendor
-
Select the circle-with-minus icon in the vendor's
Actionscell (its tooltip readsDeactivate). The Deactivate Vendor confirmation opens. -
Read the message — the vendor keeps all of its data and history and stays in
the register, but is left out of active-vendor lists and reporting — and
confirm. The
Statuschanges toInactive. -
To bring it back, select the same icon, now a circle with a tick
(
Activate), and confirm Activate Vendor. You can also use the bulk Change Status action, orActivateon its detail page.
There is no separate archived state: Inactive is the only
offboarded state a vendor has, and it is fully reversible. Inactive vendors stay
visible under All Statuses; filter to Inactive to see
only them.
Bulk actions and export
Ticking rows reveals an action bar showing only what your role allows.
Change Status sets the selection to Active or
Inactive (Contributor
and above). Delete asks for confirmation and removes them
permanently (Manager and
Admin only).
Export downloads the selection as
vendors-export-{timestamp}.csv (Viewer, Manager and
Admin).
The AI assist
- Deep Investigation (the lightbulb icon, or the detail-page button) searches external sources for breach history, certifications and security incidents, then combines that with the vendor's own record — criticality, assessment history, DPA (data-processing agreement) details, GDPR and compliance requirements — to list gaps and recommendations. It usually takes 30 to 90 seconds; keep the dialog open.
- AI Analysis scores the vendor from the record you already hold, proposing a rating, a risk level and suggestions with a confidence level attached. If a recent analysis already exists, Aegis shows that one instead of running another.
- Smart Triage (AI) ranks active vendors by criticality, overdue review, never-assessed and rating, then narrates that order. The ranking is worked out deterministically — the AI describes it rather than choosing it — with no external data. Saved briefings appear below the register.
All three gather, score and suggest. None changes a vendor's status, rating or owner on its own: a person reviews the output and decides. Investigation works best for well-known software and cloud providers; for a small local supplier it may return very little, so record your own due-diligence files as evidence. AI actions are recorded against your organisation's AI usage, and only roles allowed to run AI actions see these buttons — and only while AI is switched on for your organisation.
Tips and limits
-
A new vendor has no rating and no review date. Use
Schedule reviewon its detail page, or it sits in the register as Not scheduled indefinitely. -
An overdue review shows in red under
Next Reviewwith an (Overdue) marker. Whether you also get an alert depends on your notification setup. - Deactivate rather than delete. Deactivating keeps the record and its history; a bulk delete is permanent.
- Add a primary contact before a questionnaire campaign, or the campaign skips the vendor.
- If you are subject to DORA, its third-party-provider register is separate from this one and more detailed; you may keep both — see DORA.
Where this connects
Due-diligence files — questionnaire results, audit reports, certifications — belong in Evidence and link back to the vendor. Findings are raised in Risks, questionnaires built in Questionnaires, claimed certifications tracked in Security standards. For a worked example, see the vendor scenario.