Signing in
How an Aegis account comes to exist, how you sign in to it, and how you add a second factor so a stolen password is not enough on its own.
Before you can prove anything in Aegis, two things must be true: you have an
account (a record holding your email, your name, and your role), and you have a
live session (proof that the account belongs to the person at the keyboard).
This chapter covers both, and then
multi-factor authentication (MFA — a second
proof of identity on top of your password), which you manage yourself under
Account security.
Who uses it
Signing in is for everyone: /signin is public. What you can do
after you sign in depends on your role:
Admin,
Manager,
Contributor, or
Viewer. The account security page
at /account/security is open to every signed-in user whatever their
role (the second screenshot was captured as a Viewer), and each person manages
only their own second factor there — nobody can change another person's.
How an account is created
An Aegis account comes to exist in one of two ways, and the third route people look for is closed.
-
An administrator invites you. Most people join this way. A
one-time link in your email opens
/accept-invite, where you set your name and a password and are joined to the existing workspace with the role the administrator chose. - Single sign-on (SSO). Where your organisation federates logins through Microsoft Entra ID or Keycloak you never set an Aegis password: you authenticate with your work account, and your role is mapped from your identity provider's groups.
-
You cannot sign yourself up. Aegis is provisioned by an
administrator, so
/signupcarries no form: it showsRegistration Disabledwith the lineSelf-registration is not available for this application., points you at your administrator, and sends you to the sign-in page after a few seconds. An operator can open the underlying credential sign-up endpoint for a first-time installation, but the page itself always reads the same.
Every password is at least 12 characters. When you accept an invitation the
server applies the full policy on top of that: an upper-case letter, a
lower-case letter, a digit, and a symbol, and it must not contain the local
part of your email address. Where an operator has switched on the breach
check, a password found in a public breach corpus is refused as well. The
invitation form's hint reads Must be at least 8 characters, but
the server applies the twelve-character policy — choose twelve or more and
your first attempt is accepted. A password reset enforces the same
twelve-character minimum.
What's on this screen
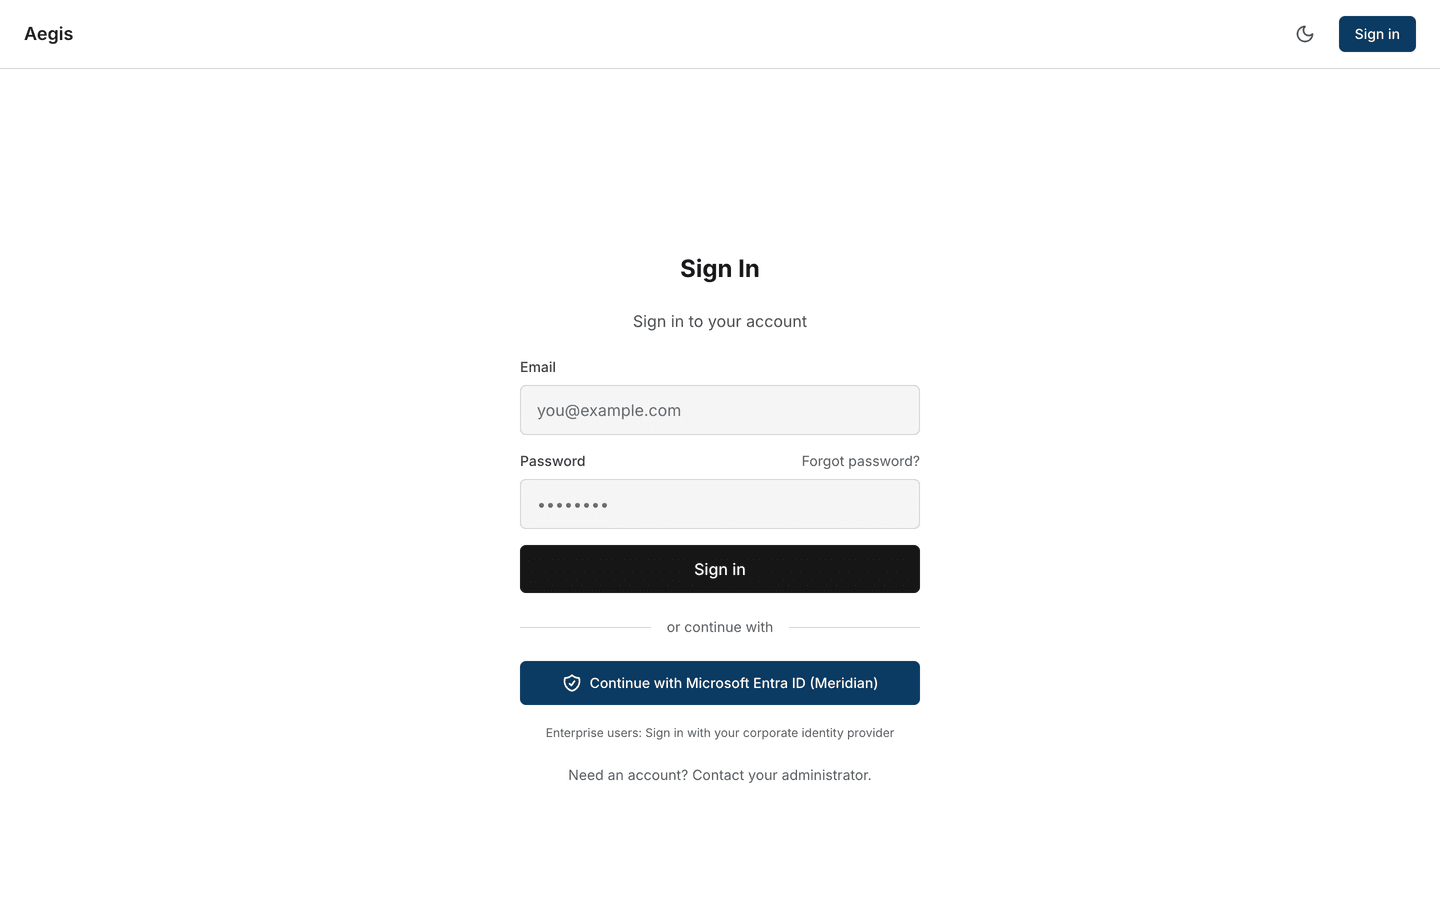
The sign-in page is a single centred column. A thin header runs across the top:
the
Aegis wordmark on the left, and on the right a moon icon that
switches between light and dark appearance beside a
Sign in shortcut. Everything else sits in the column beneath, top
to bottom:
-
The heading
Sign In, with the sub-lineSign in to your account. -
An
Emailfield showing the placeholderyou@example.com. -
A
Passwordfield, with theForgot password?link on the same line as the label, over on the right. - A full-width
Sign inbutton. -
A
Sign in with a passkeybutton with a key icon, shown only where the operator has switched passkeys on for the tenant; the captured workspace has none. -
A divider reading
or continue with, then one button per configured enterprise provider, each readingContinue withand the provider's name — on the captured screen there is one,Continue with Microsoft Entra ID (Meridian), noted underneath asEnterprise users: Sign in with your corporate identity provider. -
The closing line
Need an account? Contact your administrator.
Those buttons and dividers appear only when an administrator has configured the
provider, so a workspace without SSO shows the form and the closing line with
nothing between them. Where a social sign-in (Continue with Microsoft
or Continue with GitHub) is also configured, a second divider
reading or separates those buttons from the enterprise ones; the
captured workspace has none. The public page carries no instrumented controls,
so the figure below has no numbered callouts — the labels in the steps match the
words on screen exactly.
Signing in with email and password
-
Open
/signin. Opening the plain web address first shows the public Aegis landing page, whoseSign inbutton brings you here. If you already have a live session,/signinshowsRedirecting to dashboard...instead and takes you straight in. If Aegis sent you here because you opened a page while signed out, it remembers that page and returns you to it once you are in. -
Type your work email into the
Emailfield and your password into thePasswordfield. -
Select
Sign in. The button readsSigning in...while it works, then your dashboard (or the page you were sent from) opens if the details are correct and your account has no second factor. An empty field or a bad password puts a red banner above the form —Email and password are requiredorInvalid email or password— and leaves you on the page to retry. Three other banners mean something different:Too many sign-in attempts. Please wait a moment and try again.(wait, do not reset your password),This account has been deactivated — contact your administrator, andAn unexpected error occurredwhen the server itself failed. -
To use single sign-on instead, leave the fields empty and select your
organisation's
Continue with …button — on the captured screen,Continue with Microsoft Entra ID (Meridian). Your identity provider takes over, and once it is satisfied you return to Aegis already signed in. -
To use a passkey you have already added on the account security screen,
leave the fields empty and select
Sign in with a passkey. Your browser or device asks for the fingerprint, face or PIN you use to unlock it, then your dashboard (or the page you were sent from) opens. A passkey sign-in does not ask for the six-digit code. If you cancel the prompt or the device has no passkey for Aegis, a red banner readsPasskey sign-in did not complete. Try again, or sign in with your password.and you stay on the page.
If your account asks for a six-digit code
When an account with an
authenticator app (TOTP) enrolled — a
time-based one-time code app such as a password manager or an authenticator —
signs in with email and password, Aegis does not sign you in
yet. The form is replaced by a challenge headed
Two-factor authentication, with the line
Open your authenticator app and enter the current 6-digit code to finish
                        signing in.
- Open your authenticator app and read the current six-digit code for Aegis.
-
Type it into the code box under
Enter your 6-digit authentication code, which accepts digits only and keepsVerifydisabled until six are entered. -
Select
Verify; it readsVerifying...while it checks. Only a correct, unexpired code completes the sign-in; a wrong or stale one showsInvalid authentication code. Please try again., clears the box, and leaves you to enter the next code. If you waited too long, the challenge itself has lapsed: you are returned to the email-and-password form withYour sign-in attempt has expired. Please sign in again.The rate-limit and deactivated-account banners described above can also appear at this step. -
On the wrong account, select
Use a different accountunderneath: the code and the password you typed are discarded and the email-and-password form returns, with the email still filled in for you to overtype.
The six-digit challenge belongs to the email-and-password route. If you sign in through SSO, your identity provider is responsible for any second factor, and Aegis does not ask again.
If you forget your password
-
On the sign-in page, select
Forgot password?beside the password label. A short page opens that asks only for your email address. - Type your email and request the reset link. The page confirms it has been sent whether or not the address is registered, so the form cannot be used to discover who has an account.
- Open the link from your inbox and enter a new password twice. Anything under 12 characters, or two entries that differ, is refused. The link is single-use — opening it again reports it is no longer valid and you request a fresh one.
What's on the account security screen
Once you are signed in, you manage your own second factor at
/account/security. There is no menu entry for it: you arrive either
from the Set up MFA button on the
Add a second factor to your account banner, or by typing the
address. It is a normal application page, with the usual furniture around it.
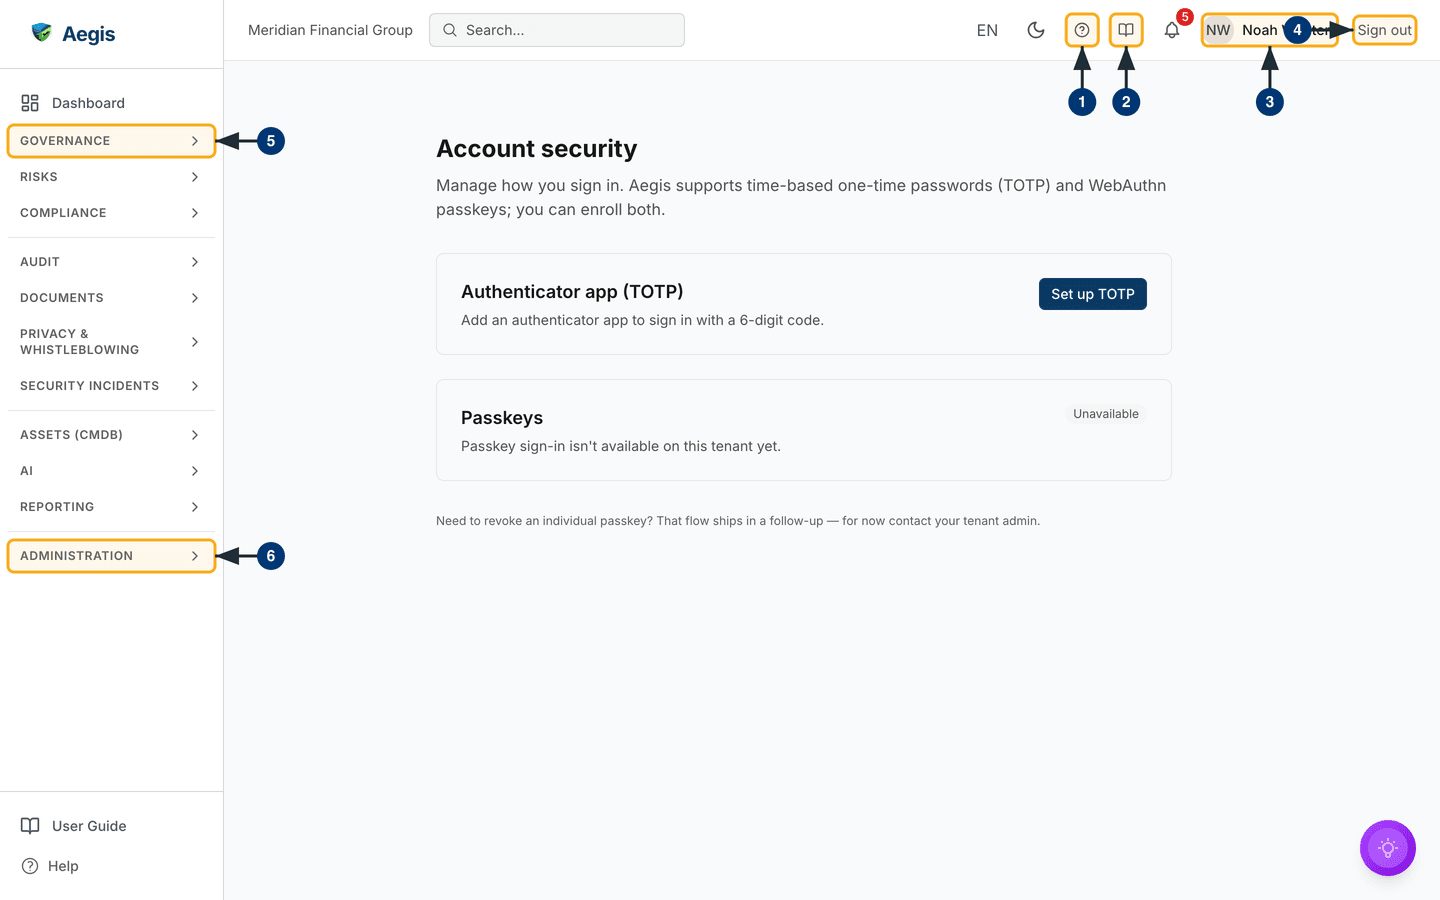
The left sidebar carries Dashboard and the collapsed module groups
— GOVERNANCE, RISKS, COMPLIANCE,
AUDIT, DOCUMENTS,
PRIVACY & WHISTLEBLOWING, SECURITY INCIDENTS,
ASSETS (CMDB), AI, REPORTING and
ADMINISTRATION — with User Guide and
Help pinned at the foot. The top bar carries your organisation's
name (on the captured screen, Meridian Financial Group), global
search, the language switch EN, the light/dark switch, a
? help icon, an open-book User Guide icon, the notification bell
(the captured screen shows five unread), your avatar and name, and
Sign out. A round purple button in the bottom-right corner opens
the AI assistant; it plays no part in account security.
The page body itself is a narrow column headed Account security,
with the sub-line
Manage how you sign in. Aegis supports time-based one-time passwords (TOTP)
                        and WebAuthn passkeys; you can enroll both.
, and two cards:
-
Authenticator app (TOTP) — here it reads
Add an authenticator app to sign in with a 6-digit code.beside aSet up TOTPbutton, because this account has not enrolled one. Once enrolled, the card readsTwo-factor authentication is enabled on your account., the button gives way to anEnabledbadge with anEnabled ondate beneath the text, and a control to turn it off again appears. -
Passkeys — here the card shows an
Unavailablebadge andPasskey sign-in isn't available on this tenant yet.Passkeys need an operator to configure them for your workspace; until that happens there is no enrolment button, and the card says so rather than dead-ending you. Where an operator has configured them, the card offersAdd a passkey(thenAdd another) and lists each enrolled passkey with its device type and the date it was added.
Each enrolled passkey carries its own Revoke button: after you
confirm, that passkey can no longer sign in to your account, and you can add the
device again later.
Finding your way around this screen
-
The
?in the top bar opens the help panel, which slides in over the page with help topics for the screen you are on and a search. You stay on the page underneath. - The open-book icon beside it opens the in-app User Guide at the chapter for the screen you are on. It is a normal link, so it replaces the page — come back with your browser's back control.
-
Your avatar and name, at the right, are one link: selecting either opens
your own profile page at
/account/profile. The name is also a reminder that this page only ever edits the account named here. -
Sign out, at the far right, ends your session — see Signing out, below. -
GOVERNANCEheads the working modules. Your security settings are not among them, and no group in the sidebar leads here —/account/securityis reached from the second-factor banner or by address. -
ADMINISTRATION, at the foot of the groups, can holdWorkflows,HR,Connectors,Settings,API KeysandWebhooks, along with a few administrator-only settings entries; each entry shows only if your role and your workspace's licence allow it, and the group appears whenever at least one does. Inviting people, setting roles and configuring single sign-on all sit underSettings, and a Viewer does not get the user-management pages.
Setting up an authenticator app
Enrolment happens on its own page, headed
Set up two-factor authentication. There is no sidebar link to it:
you reach it from the Set up TOTP button, or Aegis sends you there
itself if your organisation has made a second factor compulsory for your role.
That page is not captured in this guide, so follow the labels below.
-
Select
Set up TOTPon the first card. The enrolment page opens and asks you toConfirm your current passwordfirst — this stops anyone who finds your unlocked screen from quietly adding their own second factor. -
Enter it and select
Continue, which stays disabled until the field has something in it. A wrong password showsCould not start enrollment. Check your password and try again.A correct one brings up a QR code underAdd this account to your authenticator app, with the plainotpauthtext underneath for devices that cannot scan. -
Scan it, then type the six digits your app produces and select
Verify and enable. A code that does not match is rejected withThe code you entered did not match. Try again.and you try the next. A matching code switches the factor on. -
Aegis then shows your backup codes under
Save your backup codes— single-use codes for the day you lose your phone, displayed once. TakeCopy codes, store them safely, tickI have securely saved my backup codes, and selectDone. That button stays disabled until the box is ticked. Pressing it completes the enrolment: Aegis records the date shown on the card and writes the enrolment to the audit log, then confirmsTwo-factor authentication is now enabled on your account.If you were sent to enrol on your way to another page, you are taken on to that page instead.
The codes cannot be shown again. Navigate away before saving them and you can still sign in with your authenticator, but you have no fallback if the device is lost — an administrator would have to reset the factor for you.
Turning a second factor off
-
Return to
/account/security. With TOTP enabled the first card shows theEnabledbadge and aDisable two-factor authenticationcontrol. -
Select it. The card expands and asks you to re-enter your account password,
noting that your password alone will get you in until you set the factor up
again.
Cancelcloses it with nothing changed. -
Enter it and select
Disable two-factor. A wrong password is refused withThat password is incorrect. Two-factor authentication is still enabled.; on success aTwo-factor authentication disabled.notice appears and the card returns to itsSet up TOTPstate.
Signing out
Select Sign out at the top right of any page (on a phone-width
screen it shrinks to an icon). Your session is ended on the server and the
cookie is removed from your browser, and you land on the public Aegis landing
page, whose Sign in button takes you back to /signin.
On a shared or public computer, sign out rather than only closing the tab.
Tips and limits
- Provider buttons depend on configuration. Yours may show different providers from the capture, or none.
- A rate-limit message is not a wrong password. After too many attempts Aegis asks you to wait; resetting your password will not help, and waiting a moment will.
- The code challenge is fail-closed. Until a correct code is verified no session exists, so closing the tab at that point leaves you signed out.
-
Passkeys need operator setup. Once you have one, you revoke
it yourself from
/account/security; a lost device does not need an administrator. -
Your organisation may require a second factor. A banner
headed
Add a second factor to your accountprompts you until you have one; itsSet up MFAbutton opens/account/securityandRemind me laterhides it for now. Where a second factor is compulsory for your role the prompt becomes a redirect to the enrolment page. Keep at least one working factor, and keep the backup codes.
Where this connects
Once you are in, The screen layout and The left menu orient you to the sidebar and the top bar, and First-time setup covers the one-time onboarding that configures your workspace. What you can do next depends on your role — see Roles and what each can do. Administrators configuring Entra ID for the whole organisation should read Single sign-on with Microsoft Entra ID, and Getting help lists the common sign-in problems and how to reach support.