Settings
One tabbed screen holding your own account and theme, the organisation profile, users and roles, the integration directory, the system-wide switches, frameworks and a health panel.
Settings is where Aegis is configured. You come here for your own profile and theme, but it is also the door to what shapes the whole tenant (your organisation's private Aegis instance): who may sign in, what is connected, which frameworks are tracked. Most of that is reserved for administrators, so the tabs you see depend on your role.
Who uses it
Everyone can open /settings, but almost every tab beyond the first
is gated.
-
Admin sees all nine tabs —
Account,Organization,Users,Roles,Permission Groups,Integrations,System,FrameworksandDiagnostics— and can change what is on them. -
Manager holding the
department-settings permission also sees
Organizationand can edit the profile there; the risk-severity and risk-review-reminder cards further down that tab stay administrator-only. -
Contributor and
Viewer normally see only
Account. The other tabs read from an administrator-only API, so their buttons are hidden rather than opening an empty panel.
The active tab is mirrored into the address as ?tab=users, so a
bookmark reopens it. A link naming a tab your role cannot see falls back to
Account rather than a blank panel.
What's on this screen
The page opens with the heading Settings and the line "Manage your
account, system configuration, and integrations." Under it runs the tab strip,
with Account selected and underlined. A save anywhere on this page
confirms itself with a short "Settings saved successfully." notice (or the
section's own message), shown as a pop-up toast so you see it beside the section
you saved rather than at the top of a long page; a failed save shows its reason
the same way. If the page itself cannot load, a red message appears above the
tabs, and rate-limiting shows there as an amber banner with a Retry
button.
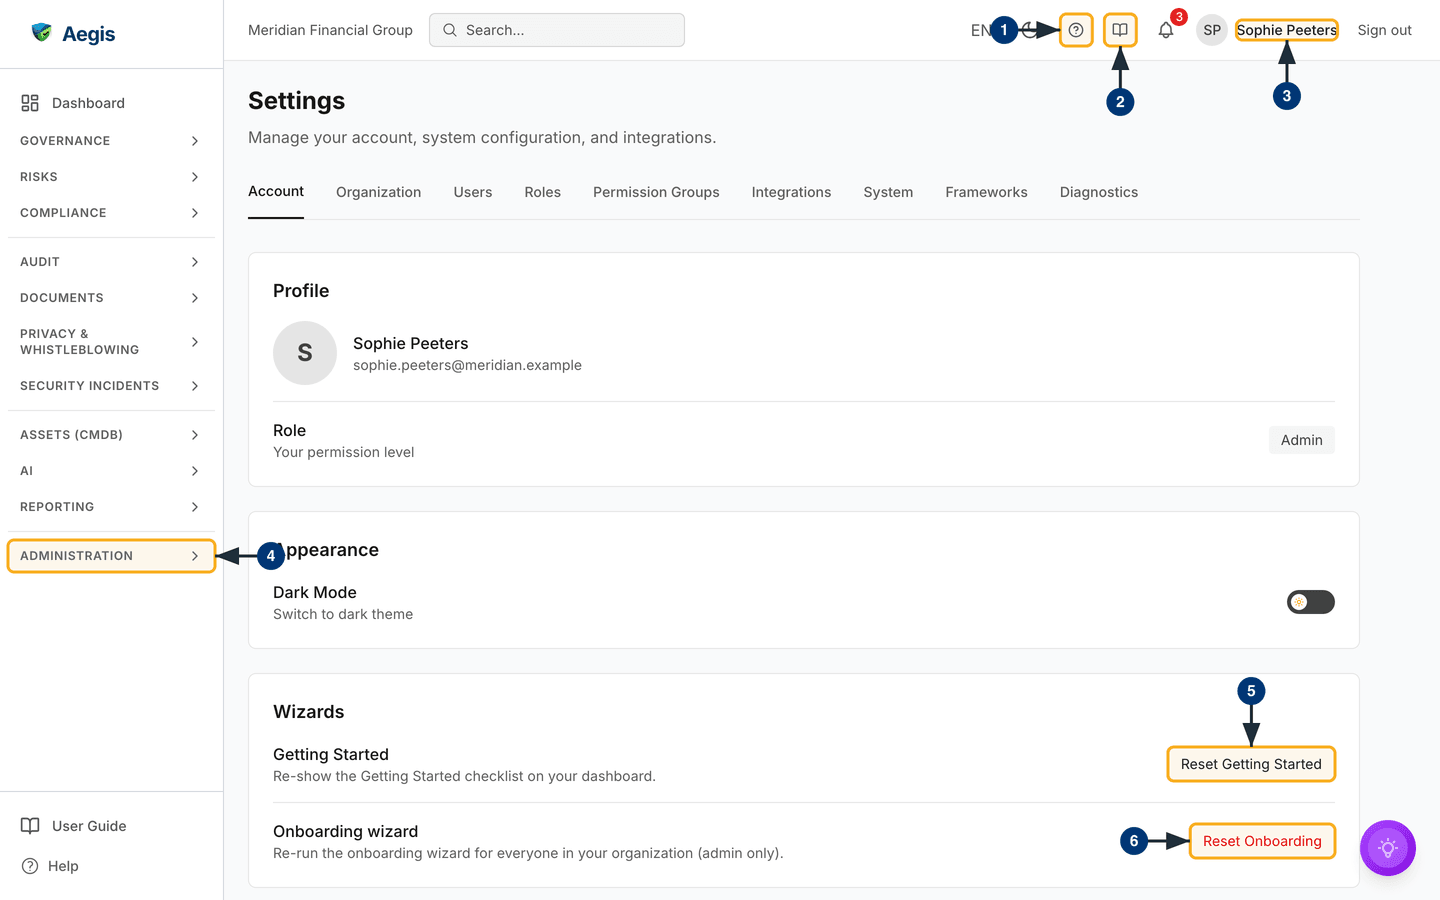
The Account tab stacks its cards. Profile shows an
avatar built from the first letter of your name, your name and email address,
and a Role row labelled "Your permission level" with your role as a
grey badge at the right — Admin in the captured screen. Nothing on
this card is editable; to change your own name, job title or phone number,
select your name in the top bar (see Your account).
Appearance holds a single row, Dark Mode / "Switch to
dark theme", with a toggle at the far right. Wizards holds the two
reset controls covered below. Under the fold of the capture, administrators also
get a Dead-letter queue card, and everyone gets
Quick Links, with shortcuts to
Configure Connectors and View Compliance.
Around the page is the usual Aegis frame: a top bar with your organisation's
name, search, the language code, a moon for dark mode, a help "?", an open-book
icon for the User Guide, a notification bell, your initials and name, and
Sign out. On the left is a sidebar with Dashboard at
the top, eleven collapsed groups from Governance down to
Administration, and User Guide and
Help at the foot.
Get your bearings, and reset the wizards
- Select the help "?" in the top bar. A help panel slides in from the side with short topics for the page you are on and a search box.
- Select the open-book icon beside it. The built-in User Guide opens at the chapter for the screen you are on.
-
Your name sits at the right of the top bar with
Sign outbeside it; theProfilecard repeats it and adds your role. Selecting your name or initials opens your own profile page. -
Select
Administrationat the foot of the sidebar groups. The group expands to show the administration pages,Settingsamong them — that is how you get back here. The group appears for any role with at least one page in it, so what it lists depends on your role. -
In the
Wizardscard, selectReset Getting Started. The button reads "Resetting…", then a message confirms that Getting Started will re-appear on your dashboard. This affects only you. -
Select the red-outlined
Reset Onboarding— administrators only. A dialog headed "Reset onboarding for all users?" warns that everyone sees the wizard again at their next sign-in. Confirm, and a message reports that onboarding has been reset for all users.
Switch the theme, and jump to a linked screen
-
On the
Appearancecard, select theDark Modetoggle. The dark theme applies at once and the row relabels itselfLight Mode/ "Switch to light theme", so the same toggle takes you back. -
Scroll to
Quick Linksand selectConfigure ConnectorsorView Complianceto leave Settings for those screens.
Redrive a failed background job
Administrators see a Dead-letter queue card on the
Account tab, below Wizards. It lists
compliance-critical background jobs that failed for good, after all their
retries — the work that would otherwise be lost without anyone noticing.
-
Read the card. When nothing has failed it says "No compliance-critical job
has failed permanently." Otherwise a table lists each job under
Job,Failed at,Retries,ErrorandActions. -
Once the cause is fixed, select
Redriveon the row. The button reads "Redriving…", then a "Job queued again" message confirms the job will run once more.
Set the organisation profile
The Organization tab records the jurisdiction, the NIS2
classification and the data-protection contact Aegis uses for regulatory
reporting. Select Organization; the cards load with your stored
values, starting with Jurisdiction & NIS2 Classification. At
the top of that card, choose your EU Member State and
NIS2 Entity Type; both start at Not set.
-
Choose the
NIS2 sector, and theNIS2 subsectorwhere one applies. The sector decides which sectoral reporting duties Aegis shows on incidents — for example Z-CERT and the IGJ for Dutch healthcare, which need the sectorHealth. A change re-derives the NIS2 controls. -
Fill in the size and status fields if they apply:
Annual balance sheet total (EUR)for the EU SME size test, aMember-State designation, andQualified trust service provider (eIDAS). A designation or qualified status makes you an essential entity regardless of size. Choosing a designation adds aDesignation justificationbox for the reason. -
Read the
NIS2 authority — …card that appears once a member state is saved. Its badge marks the body the NIS2 registry lists for that state as theCompetent authorityor as theSingle point of contact. A single point of contact is not necessarily your supervisor, because in those states supervision depends on your sector; the card then says so. ANot verifiedbadge appears when the entry could not be confirmed against an official source. - Select the authority's name to open its own website in a new tab.
-
Read the
Notethe registry carries for that state, and theChecked ondate under it, which says when the entry was last confirmed.
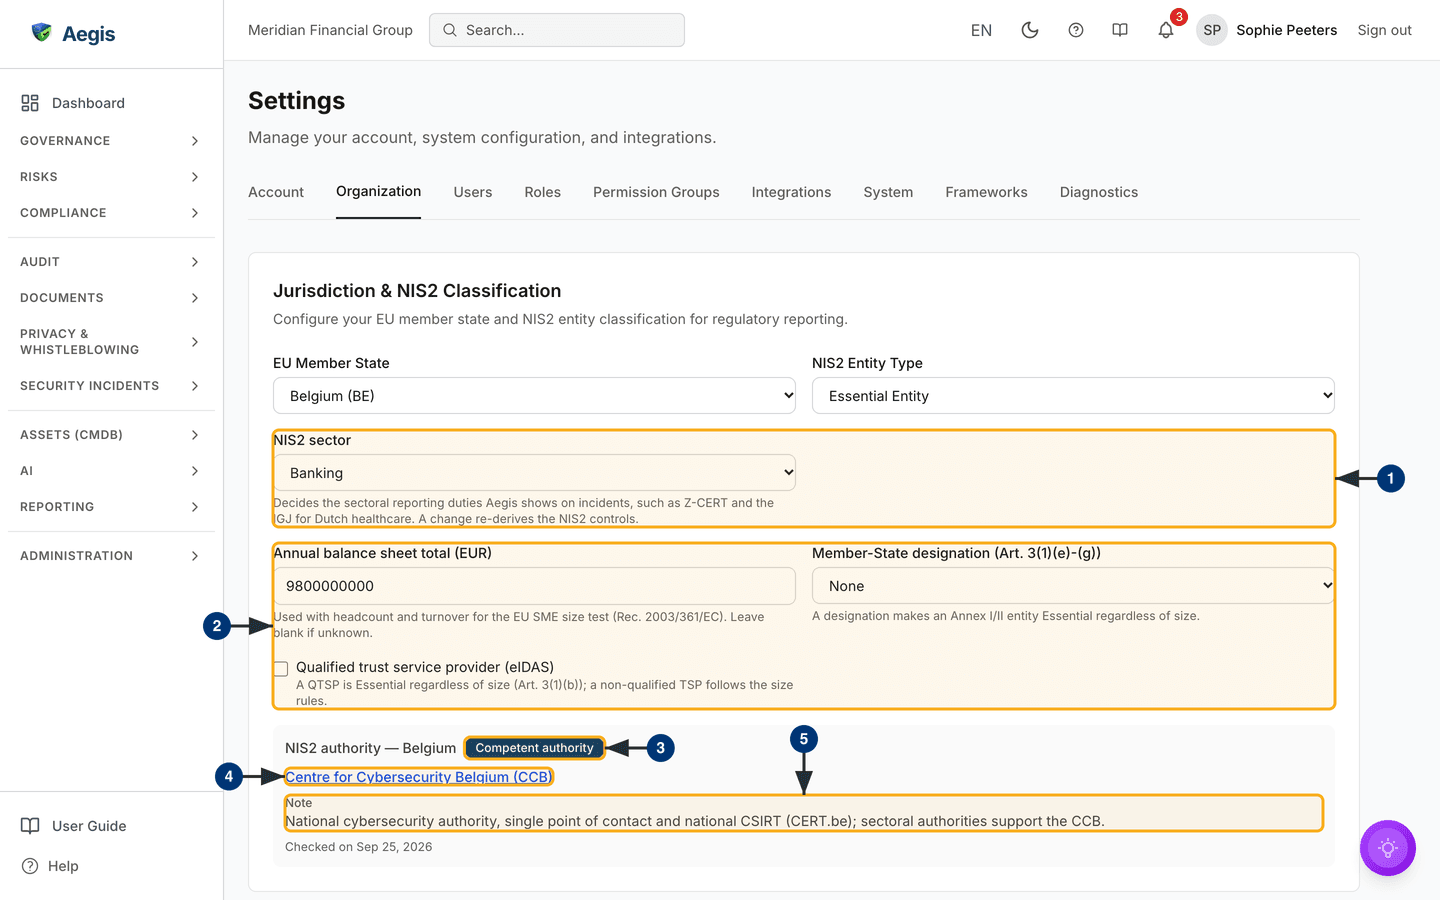
In the captured screen the demo organisation is set to Belgium as an essential entity in the banking sector, and the card names the Centre for Cybersecurity Belgium (CCB) as the competent authority. If you pick a different member state without saving, the card asks you to save first; before any member state is saved it asks you to select and save one.
Further down, Incident-reporting jurisdictions lists the member
states your incidents are reported in besides the one above. Use
Add a member state to add, for example, the Netherlands;
authorities and deadlines are modelled for Belgium, the Netherlands, Luxembourg,
France and Germany, and other states are saved but shown as not modelled. For
Germany you also pick the Land of your establishment. A
Resolved incident-reporting authorities list shows which authority
Aegis will name for each duty.
-
Fill in
DPO NameandDPO Email— the contact used for GDPR and NIS2 notifications — then selectSave Organization Settings. A confirmation message appears; an invalid email address is refused inline first. -
Administrators also see a
Risk Severity Levelscard below. Pick aSeverity Preset—Default (5 levels)orISO 27005 (4 levels)— or switch toCustomand set each level'sKey,Label,Min ScoreandColor, with aPreviewgrid showing how scores will be shaded. Saving is refused, with the reasons listed, unless there are between two and ten levels, every key is unique, and the lowest level starts at aMin Scoreof 1 so no score is left uncovered. -
Below that, administrators set
Risk review reminders: theReminder (days before the review date), 1 to 90, when the risk owner is reminded of a coming review; and theEscalation (days after the review date), 1 to 60, after which every manager is alerted if nobody has confirmed the review. SelectSave; a "Risk review reminders saved" message confirms it.
Manage users, roles and permission groups
Three administrator-only tabs carry access control.
-
Open
Users. A table lists everyone underUser,Role,Status,Last Login,CreatedandActions, with a search box,RoleandStatusfilters and anInvite Userbutton above it. The row actions change someone's role, reset their password and deactivate or reactivate the account; select several rows and a bulk bar offers the role change, deactivation and deletion for all of them at once. Invitations not yet accepted sit in their own table underneath. Select a user to open their detail page, whereEdit name & job titlecorrects their name and job title (see What each role can do). -
Open
Roles. This tab only reports: a card per built-in role with the number of users holding it, then aPermission Matrixof what each may do. A notice states that the built-in roles have fixed permission sets and cannot be edited here, and points to Permission Groups for finer access. -
Open
Permission Groupsfor finer-grained access than a role gives. SelectCreate Group, name it and choose the permissions it carries; the table then listsName,Description,Permissions,MembersandView,EditandDeleteactions. Mapping groups from your identity provider onto Aegis roles is a different screen — see Single sign-on with Microsoft Entra ID.
Open an integration
The Integrations tab is a directory of link cards in two groups.
-
Under
External Integrations, openSingle Sign-On (SSO)to configure OIDC providers and group mappings, orWebhooksto push Aegis events to other tools. -
Under
Advanced Configuration, openControl Monitoring,Hybrid Appliances,MCP Servers,Peer Benchmarking,Custom domain,Meeting Rooms,Notification Preferences,Install toolorHR Connections(register an HR system so Aegis can sync your employee directory). Each opens its own page; the back button returns you here. An extraAI Modelscard joins this group when model management is switched on. -
A card whose capability is outside your plan carries an amber
Not in your planbadge and a greyed icon. It still opens, and the page behind it explains what your licence covers. OnHybrid Appliancesthat means an organisation without the licence can still list and decommission appliances it already enrolled.
Connect Microsoft Teams or Zoom for meeting rooms
The Meeting Rooms page lists the online meeting providers —
Microsoft Teams, Zoom and kMeet. Turning a provider on with its
Enabled checkbox only makes it available on the governance meeting
form, where people paste a join link. For Aegis to create a Teams or Zoom room
itself, an administrator must also connect the provider with an app registration
your organisation owns. kMeet needs no connection. This page is for
administrators only; everyone else is sent back to Settings.
Before you start, prepare the app on the provider's side.
-
Microsoft Teams — register an app in Microsoft Entra ID,
add the
OnlineMeetings.ReadWrite.Allapplication permission and grant admin consent. Then allow the app to create meetings for one organiser account with the Teams PowerShell commandsNew-CsApplicationAccessPolicyandGrant-CsApplicationAccessPolicy. You need the directory (tenant) ID, the application (client) ID, a client secret value and the organiser's user object ID. -
Zoom — create a Server-to-Server OAuth app in the Zoom App
Marketplace with the
meeting:write:meeting:adminscope (meeting:write:adminon classic apps). You need the account ID, client ID, client secret and the host user — an email address or a Zoom user ID — who will own the meetings.
-
Open
Settings›Integrations›Meeting Rooms. Each Teams and Zoom row carries a status badge:Not connected,ConnectedorReconnect required. -
Select
Connecton the provider's row (Replace credentialsonce it is connected). A form opens inside the row with the setup reminder and one field per value. The form is always empty — Aegis never shows stored values again, not even the IDs — and the client secret is a password field. -
Fill in every field and select
Verify and save. Aegis first asks the provider for a token with these values. If the provider accepts them, they are stored encrypted, the form closes and the badge turnsConnected. If the provider refuses them, or cannot be reached, nothing is saved and a message under the form says which; the IDs stay filled in and only the secret is cleared. -
Make sure the provider's
Enabledcheckbox is ticked. Only a provider that is both enabled and connected can create rooms — draft meeting minutes then offer a button to create one (see Governance bodies). -
To stop Aegis creating rooms, select
Disconnectand confirm. The stored values are deleted; join links already on meetings keep working.
A provider shows Reconnect required when its stored credentials
are in an older format — for example a pasted access token from an earlier
version — or can no longer be read. Aegis never uses them. Select
Replace credentials and enter the values again.
Saving proves the app credentials work, but not that the organiser or host user is right, or that the Teams access policy covers them. A mistake there shows up the first time someone creates a room: Aegis then reports that the provider rejected the connection and asks an administrator to check it. Connecting, replacing and disconnecting are each written to the audit log with the names of the fields that changed — never their values.
Use your own domain
By default Aegis runs at the address Euraika gave your organisation. An
administrator can move it to a domain of your own, for example
grc.yourcompany.com. Sign-in, the links in e-mails and single
sign-on then all use that domain, and the old address forwards to it, so
bookmarks keep working. Open Settings, the
Integrations tab, and the Custom domain card. The page
is for administrators only.
-
Create the DNS record. The page shows the exact record to
create with your DNS provider: a
CNAMEfrom your domain to your current Aegis address. It must be a DNS-only record. On Cloudflare that means the grey cloud, not the orange one. Do not add a forward, a page rule or a redirect rule for the domain: a proxy or a redirect breaks single sign-on and stops Aegis from obtaining a certificate. If your zone has aCAArecord, it must allowletsencrypt.org. A second record of the same kind is needed forwhistleblow.<your-domain>, with the same target: your whistleblowing channel moves to the domain too, and Aegis switches over only once both records are in place. -
Request the domain. Type the domain and choose
Request domain. Aegis checks the record for up to 48 hours, obtains a certificate and then switches over by itself. The status line shows each stage:Waiting for DNS,DNS verified,Switching overand finallyActive. When something is in the way, the page says what in plain words, for example that the domain redirects to another site. -
Update your single sign-on app. Once the domain is
Active, the page lists the new redirect URIs, one per SSO provider, in the formhttps://<your-domain>/api/auth/oauth2/callback/<provider>. Add each one to the app registration in your identity provider. In Microsoft Entra ID that isApp registrations → your app → Authentication → Redirect URIs. SSO sign-in fails until you do. Remove the old redirect URI only after SSO works on the new domain.
Everyone signs in once more after the switch, because sign-in is tied to the
address. Links in older e-mails keep working through the forward. Systems
that send webhooks or call the Aegis API must use the new domain, because
most of them do not follow a forward. To go back, choose
Remove domain: Aegis returns to its previous address and
everyone signs in once more.
Configure the system
The System tab carries the tenant-wide switches, all
administrator-only.
-
Use the
Enable AI Assistancetoggle in theAI Featurescard to turn the AI helpers on or off across the product. It saves as soon as you select it, and the AI controls in the other modules — the assistant button included — stop offering suggestions straight away. Switching it off also stops the AI steps in GDPR automation; non-AI processing such as deadlines, monitors and manual request handling carries on. -
Use the
AI Modelscard below it — "Configure AI models available in the chat interface" — toAdd Model, or to edit, disable or delete an existing one. A dot at the left of each row shows whether it is enabled, and the model in use by default carries aDefaultbadge. -
Read the
Licensecard forType,Max UsersandMax Storage, plus anExpiresrow when your licence has an end date; uncapped values readUnlimited, andManage license & usageopens the licence page. -
Under
Session Duration, choose aSession Lifetime— 1, 3, 7, 14, 30, 60 or 90 days. ASavebutton appears beside the list once the value differs from the stored one. -
If your tenant is licensed for regulatory intelligence, switch on
Enable regulatory digestand enter aDigest email recipient. An invalid address is refused inline before anything is saved; clearing the field removes the recipient. Teams and Slack delivery follows your connector webhooks. -
Use
Regulatory Feed Sourcesto add, edit, enable or disable the feeds the digest draws on. Two link cards follow:Vendor scoring methodology, whoseEdit methodologylink sets the criteria, weights, answer scales and rating bands for vendor assessments, andVendor questionnaires, whoseOpen questionnaire settingslink checks the module's prerequisites and sets the defaults new questionnaire campaigns start from. Last comesSupport Contact, where you set where people are sent for help; itsPreviewbutton shows them what they will see.
Saving Session Lifetime stores the value, but the hint under
the field says the change applies after the next application restart. Plan
it with whoever operates your Aegis instance. Active sessions are extended
automatically while people keep working.
Set the defaults for documents
Document settings (/settings/documents, Admin only)
holds the defaults every policy and procedure starts from. A document's own
reviewers and approvers always win over these defaults. Every change is recorded
in the audit log. Anyone else who opens the address is turned away.
| Field | What it sets |
|---|---|
Default review deadline (days) |
How many days reviewers get when a document sets no deadline of its own. |
Reminder interval (days) |
How often an open review, approval or read request is reminded. |
Read link access (days) |
How long a reader without a login keeps access after publication, 1 to 90 days. The e-mailed link itself works once and for 24 hours; a new one can be requested. |
Re-confirmation |
How often required readers confirm a document again by default, or
Off.
|
Confirmation method |
Fixed to Read link with a code; it cannot be changed.
|
-
Expand
Administrationin the sidebar and selectDocument settings. TheDocumentspage opens with aSave changesbutton at the top right. -
In
Reviews and reminders, set the values from the table above. UnderApproval, tickLet the owner approve when nobody else canto allow an owner to approve their own document when no other eligible approver exists; the approval is then marked as the owner's own. Further down,Reader sourcesshows the last synchronisation of the HR system and of the Entra ID groups that feed reader groups, orNever. -
Under
Default reviewers and approvers per category, each policy or procedure category has its own row. Tick theAdminorManagerboxes underReviewersandApprovers, tickUse these approversto put the category's approvers in force, and setApprovals neededwhere the category counts approvals. Then selectSave changes; a "Documents settings saved." message confirms it.
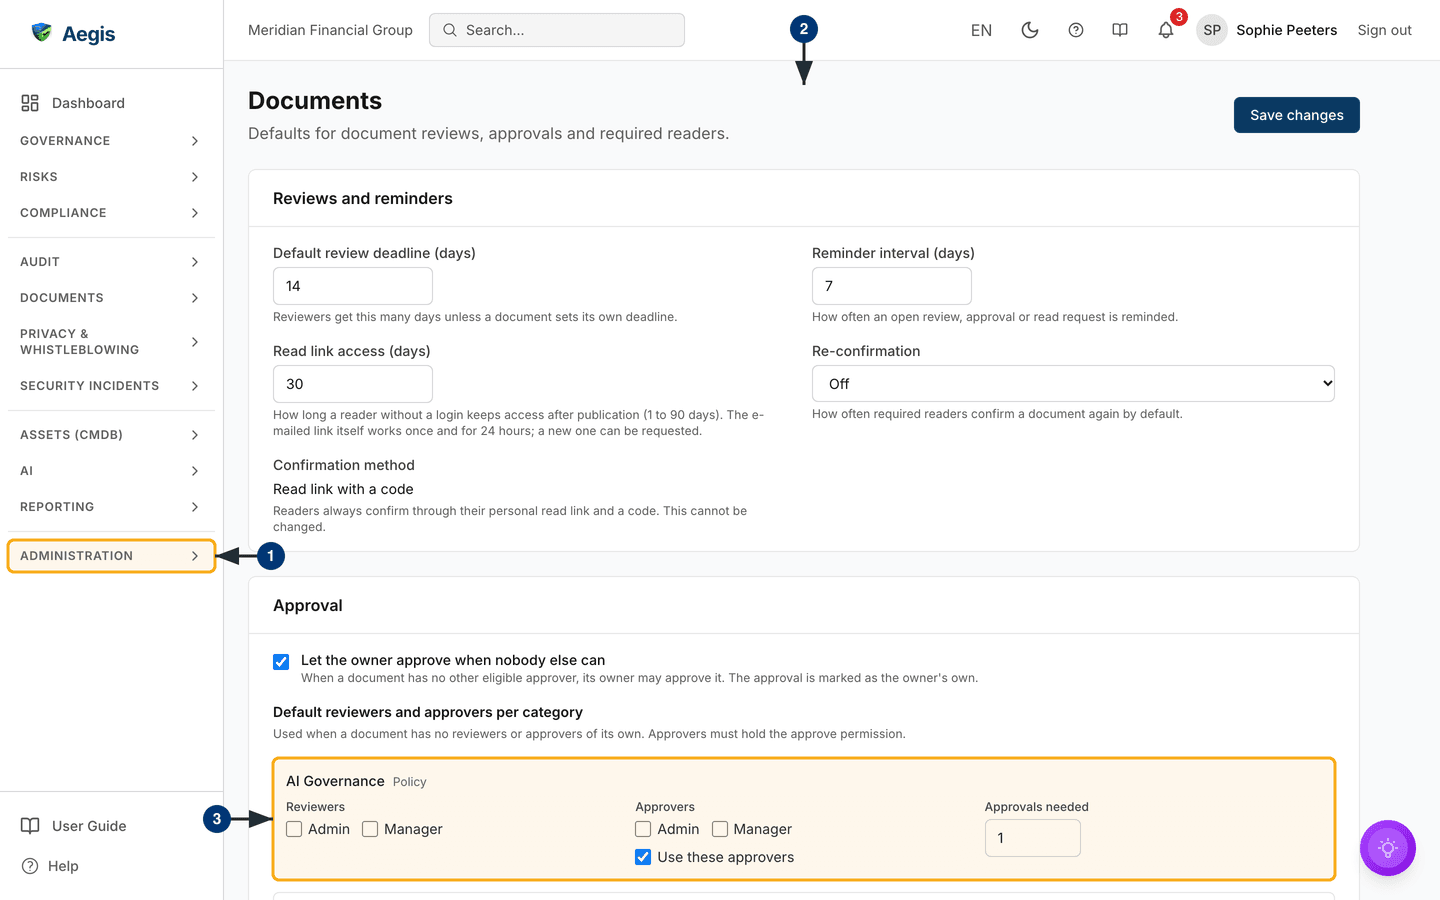
A save is refused with a message naming the category when a category whose approvers are in use has none, when a chosen reviewer or approver lacks the permission the step needs, when a chosen group no longer exists, or when the category can only take a single approval. Approvers must hold the approve permission. A category row can also note extra named people set elsewhere. If you have no policy or procedure categories yet, the section says so instead of showing rows.
Turn frameworks on and off
-
Open
Frameworks. TheCompliance Frameworkscard lists each framework your tenant holds, with its key, control count and a read-only maturity-scale summary. -
Use the toggle at the right of a row to enable or disable it. The switch is
greyed out while the change saves, then a message with the framework name
followed by
enabledordisabledconfirms it. Disabled frameworks drop out of the tracking views, their own pages show a “… is switched off” card instead of their content, their API calls are refused and their reminders stop. The data is kept: enabling one again brings its controls back into scope, and Audit Readiness recalculates straight away rather than waiting for its nightly run. A framework outside your licence shows aNot available in your licencebadge and a locked switch. -
On an enabled framework, select
Check for new templatesto pull in document templates added to that framework since it was set up. A checklist headedChoose templates to createlists them with the missing ones pre-ticked; templates you already have are listed but never changed. SelectCreate … selected, and a line under the button reports how many were added as drafts and how many were already present. -
If the card reads
No frameworks available, none is provisioned for your tenant yet. Frameworks are licensed one at a time, so ask your provider.
The list shows what your tenant is entitled to. SOC 2 is on the roadmap, not shipped, so it does not appear here.
Check system health
-
Open
Diagnostics. Two cards report whether theDatabaseisConnectedand whether theBackground Workeris running, with its queue depth and the number of jobs that failed in the last hour. A coloured dot repeats what the text says: the worker's dot turns amber when it is not running or a job has failed in that hour. -
Read the
Usagecard forUsersandStorageagainst your licence limits. AnUnlimitedlimit shows the numbers without a bar; the storage bar turns amber past 70% and red past 90%. -
Read
License Statusfor your licence type and expiry date, orNo expiration; an expired licence readsLicense expiredbeside a red dot.
The AI assist
Settings is where AI is switched on, not where it acts. Aegis AI only suggests: a person reviews and decides, and it never changes a setting on its own.
Tips and limits
-
You cannot change your own role here; that is an administrator action on the
Userstab. -
Reset Getting Startedaffects only you;Reset Onboardingaffects everyone. -
An amber "temporarily unavailable because of too many requests" banner is
short-lived rate-limiting — a second browser tab loading this page will
cause it. Select
Retry. - The regulatory digest section stays hidden unless your tenant is licensed for regulatory intelligence. Changes made here are written to the audit log, so it answers "who changed this?".
- Save confirmations appear as short pop-up messages. If you miss one, reload the tab: the cards always show the stored values.
Where this connects
-
Roles at a glance — the full matrix behind
the
Users,RolesandPermission Groupstabs. - Signing in and Single sign-on with Microsoft Entra ID — what the session and SSO settings govern.
-
First-time setup — the wizard that
Reset Onboardingbrings back. -
Connectors,
Webhooks,
Control monitoring and
Benchmarking — all reached from
Integrations. -
Compliance frameworks and
Risks — fed by the
Frameworkstoggles, the severity levels and the risk review reminders. - Regulatory alerts — what the digest summarises — and Audit log, where these changes are recorded.