Audit readiness
One screen that answers a single question — if an auditor walked in today, how would you fare across every framework you have switched on?
Doing compliance work and being ready for an audit are not the same thing, and this screen shows the distance between them. Audit readiness reads records you already keep — policies, framework controls, evidence (the proof a control works), risks and vendors — and turns them into a weighted score, a trend over time, a framework table and a short list of the moves that would lift the score most. Reading it never changes a record; the fixes happen in the modules it sends you to.
Who uses it
Opening the page needs audit-readiness:read, which all four
employee roles hold, so Viewer,
Contributor,
Manager and
Admin see the same score, trend,
table and recommendations, with nothing to create or edit in them. The controls
below are gated more tightly.
-
Readiness Triage (AI)renders only for a role holding bothaudit-readiness:generateandai:execute(the right to spend an AI credit) — Manager and Admin. Contributor and Viewer do not see the button, which is why the captured Contributor screen has none. It also needs theAI_ASSISTlicence feature, disappears while an administrator has switched the organisation's AI off, and spends an AI credit per run. -
Editing or deleting a plan in
Saved AI insightsneedsaudit-readiness:generate— Manager and Admin only. Turning one into an action item needsaction-item:create, held by Contributor and above. -
Starting a mock audit needs
mock-audit:write, held by Manager and Admin; all four roles can read past runs. -
Without the
AUDIT_READINESSmodule the sidebar entry is absent, and a role without the read permission that opens the route directly lands on/unauthorized.
What's on this screen
The page sits at /audit-readiness, under the
COMPLIANCE group in the left sidebar, below the standard top bar
(organisation name, search box, EN language switch, light/dark
toggle, Help ?, the User Guide book icon, notification bell, your
name and Sign out). The heading reads
Audit Readiness over "Assess your readiness for compliance
audits across all frameworks." For Manager and Admin one button sits on the
right of that row — Readiness Triage (AI); in the captured
Contributor session the row has no button.
Four stat cards follow. In the captured screen:
Overall Readiness 63%, with "Whole organisation ·
Medium · Score as of …" beneath it — a weighted composite for the whole
organisation, not a count; Frameworks 11, "Active
frameworks"; Controls with Approved Evidence 614,
"of 847 total"; and Evidence Coverage Rate 72%,
"Approved, current evidence linked", which is those 614 over the 847. A control
counts in the last two cards when approved, unexpired evidence is linked to it;
the content of that evidence is not assessed. With no controls at all, the rate
reads N/A rather than 0%.
The Readiness Trend card sits under the stat cards. It draws a small line of the organisation-wide score across its stored snapshots, then the latest score, the change since the first snapshot (green when up, red when down) and a line giving the snapshot count and date range. The captured screen reads "Latest: 63%", "+14.8 pts since the first snapshot" and "12 snapshots · Dec 14, 2025 – Nov 9, 2026". The trend reads up to the 30 most recent snapshots and only the organisation-wide ones, never the per-framework rows.
The Framework Readiness table gives one row per active
framework and four columns: Framework,
Evidence Coverage (a bar with the fraction and percentage beside
it), Evidence (a percentage) and Readiness. The
Readiness badge carries both a level and a percentage — for example
Low · 39% — with a short line under it naming how that figure was
measured. There is no search box, no filter bar and no row menu — it is a
read-out, and rows open nothing. In the captured screen the visible rows run
CyberFundamentals Framework, DORA,
EU AI Act and GDPR, and onwards below the fold.
Further down sit the Recommendations panel, then
Saved AI insights, then Action items.
Open the page and read your headline
-
Open the
COMPLIANCEgroup in the left sidebar and selectAudit Readiness. Four grey placeholder cards appear first, then the real figures, the trend and the framework table fill in as the data loads. -
Select the Help
?button in the top bar. Aegis opens this guide at the matching chapter in place of the screen, with the sidebar and top bar still in view; your browser's Back returns you to the page. -
Read the latest score in the
Readiness Trendcard. It is the newest stored snapshot, so it matches the Overall Readiness card above it. -
Read the change beside it, such as
+14.8 pts since the first snapshot. Green means the score has risen since the earliest snapshot shown; red means it has fallen. - Check the snapshot count and date range on the right. They tell you how much history the line covers — a long range with few snapshots means the score has not been recomputed often.
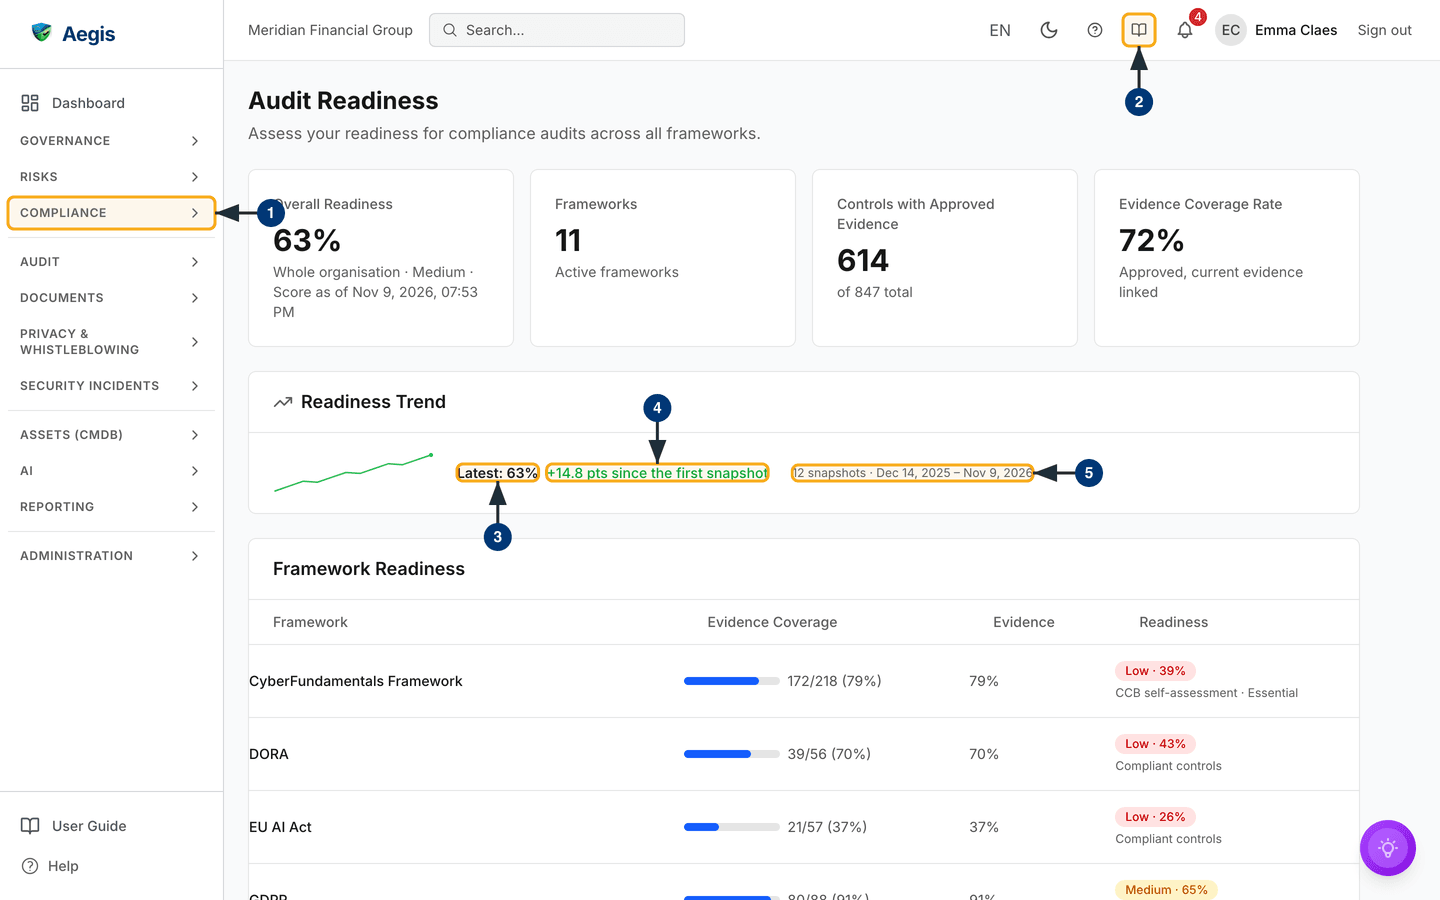
With the page open, read the Overall Readiness card first,
glance at the trend to see which way it is moving, then scan the
Readiness column for frameworks badged Low or
Medium. Those rows are where the work is.
A single point is not a trend, so with fewer than two snapshots the card reads "Not enough history yet — a trend appears once at least two readiness snapshots have been computed." A new organisation sees this until the daily job has run twice. If the history cannot be fetched, the card says "Could not load the readiness history." instead; the rest of the page still works.
How the score is worked out
Overall Readiness is a weighted composite of five dimensions,
taken from the most recent stored snapshot. A background job computes it daily,
and again as soon as a framework is enabled or disabled. The card says how old
the snapshot is — under the score it reads, for example,
Whole organisation · Medium · Score as of … with the date and time:
| Dimension | Weight | What raises it |
|---|---|---|
| Control implementation | 25% | Bringing controls to a compliant state |
| Evidence completeness | 25% | Attaching fresh evidence to more controls |
| Policy coverage | 20% | Approving and publishing more policies. A policy you move back to Draft to revise keeps counting while its earlier approved version is in force, until the revision is approved or the policy is retired |
| Risk management | 15% | Mitigating or accepting open risks |
| Vendor compliance | 15% | Completing assessments for active vendors |
Where no snapshot exists yet the card falls back to the plain control-coverage
ratio, so the number is never blank. The word under the score, and every
framework badge, follow one fixed scale: High (green) at 80% and
above, Medium (amber) from 50% to 79%, Low (red) below
50%. With no active frameworks at all, the table body is replaced by "No
frameworks configured. Add a compliance framework from the Compliance page to
get started."
How a framework row is scored
Each row's Readiness badge is the framework's
conformity (how far the framework is met) —
the same figure the readiness score and the coach use — and it is measured live,
not from the snapshot. The line under the badge says which measure applies:
| Line under the badge | Used for | What counts as met |
|---|---|---|
CCB self-assessment · <level> |
CyFun (CyberFundamentals) |
A requirement that is not a gap at your CyFun assurance level (for
example
Essential), by the CCB self-assessment rules over your
maturity scores
|
Compliant controls |
Every other framework |
A control in the COMPLIANT state, which needs current
evidence
|
So the Evidence Coverage bar and the Readiness badge
can tell different stories. In the captured screen the CyFun row has evidence on
172/218 (79%) of its controls yet reads Low · 39% at
the Essential level: linked evidence alone does not meet a
requirement. A framework with nothing in scope, or whose conformity could not be
loaded, reads N/A with no percentage and no line beneath.
Work through the recommendations
The Recommendations panel beneath the table tells you what to do
next. A fixed rule engine builds it — not AI — so the same data always yields
the same list in the same order, read from the stored snapshot rather than the
live records. Each row carries a priority badge, an impact label, a title, a
description and a Take action link, and the panel heading shows the
snapshot's age (As of …). The three count-driven rows — stale
evidence, missing evidence types and open control gaps — also name up to ten
controls each, such as A.8.13 Information backup. Each name opens
that control, and a final link such as +12 more opens the filtered
list. Controls of CyFun, NIS2, ISO 27001, DORA, the EU AI Act and ISO 42001 are
listed first, then those with the most severe unresolved gap. A snapshot
computed before this list existed names no controls until the next recompute.
| Recommendation | Raised when | Take action opens |
|---|---|---|
| Improve a dimension | It scores under 80; High at 40 or under |
Policies, Compliance, Evidence, Risks or Vendors |
| Refresh stale evidence | Evidence past the freshness window; High at 10 |
Evidence, filtered to stale |
| Attach missing evidence types | Controls missing an expected type; High at 10 |
Compliance, filtered to missing type |
| Close open control gaps | Controls not yet compliant; High at 20 |
Compliance, filtered to non-compliant |
-
Scroll to the
Recommendationspanel. Rows arrive sortedHighfirst, then by descending impact, so the top row is the largest single move open to you. -
Read the impact label beside the priority badge. A dimension row reads
+4.5 pts— the weighted points it would add at 100. A count-driven row reads12 controls— the records to work through. -
Select
Take action. Aegis opens the matching screen with the filter already applied, so you land on the records concerned rather than the whole list. - Fix the gap and return. The panel is rebuilt from the same snapshot as the score, so a cleared item stays listed until the next recompute — the daily run, or sooner when a framework is enabled or disabled.
The panel is out of shot in the captured screen, so no figure accompanies these
steps. If it cannot load, it shows "Could not load recommendations." with a
Retry button.
When no rule fires, the panel shows "You're audit-ready" over "No recommendations right now — every readiness dimension is in good shape and your evidence is up to date". That means one thing only: as of the last snapshot, no rule fired. A tenant with no snapshot at all also has no recommendations, so a brand-new organisation sees the same message before anything has been measured.
The AI assist
Readiness Triage (AI) drafts a "what's missing before the audit"
plan. It is deliberately narrow: it reads your readiness score and the same
fixed recommendation list shown on the page, and writes them up as a sequenced
plan with a concrete next step per item. It does not reorder the priorities,
rescore anything, or invent gaps or numbers. A person reviews the plan and
decides; the triage never changes a record, a control status or a score on its
own. The button is shown to Manager and Admin only, so the captured Contributor
screen cannot illustrate these steps.
-
Select
Readiness Triage (AI). Where your organisation requires it, the AI transparency notice appears first, once, for you to acknowledge. Then a dialog opens, titledAudit Readiness Triageand subtitled "What's missing before the audit", listing what it will and will not do. -
Select
Run Readiness Triage. Four progress lines appear in turn — reading the score, gathering the recommendations, sequencing what to fix first, drafting the plan — then the answer streams in below them. -
Read the result, then either
Run againorSave as record. Saved plans land inSaved AI insights, stamped with the date;EditandDeleteappear there for Manager and Admin only. -
From a saved insight, select
Create action item. It appears in theAction itemspanel below and in Action items, to track to done. A Viewer does not see this control.
The dialog's note says to run a readiness scan first if there is no score yet. Run it anyway on a tenant with no snapshot and the answer reports that nothing has been computed to assess, rather than guessing a plan — and the run still spends a credit. Every run spends an AI credit against your monthly quota, so re-run it when the numbers have moved, not to reword the same plan.
Rehearse with a mock audit
Readiness answers "how much of the work is done?". A
mock audit answers "how would we hold up
under questioning?", by rehearsing against one framework. It sits at
/compliance/mock-audit, under the AUDIT sidebar group,
and needs the MOCK_AUDIT licence feature; without it the route
shows "Mock audits are not available on your current plan" under the heading,
instead of the list. The screen is a plain list headed
Mock Audits over "Simulate audit scenarios to test compliance
readiness across frameworks." — an All Frameworks dropdown over a
table of Framework, Status, Readiness,
Completed and Created, then a count line and
Previous/Next paging.
-
Open the
AUDITgroup in the sidebar and selectMock Audit. The entry is singular; the page it opens is headedMock Audits. -
Select the Help
?button to open this guide at the Mock Audit chapter; your browser's Back returns you to the list. -
Check the top-right corner for the account you are signed in as.
Run Mock Auditrenders for Manager and Admin only — which is why the captured Contributor view has no such button. With the permission, select it, pick a framework and confirm withRun Audit; the new row readsIn Progresswith aPendingreadiness until the score arrives.
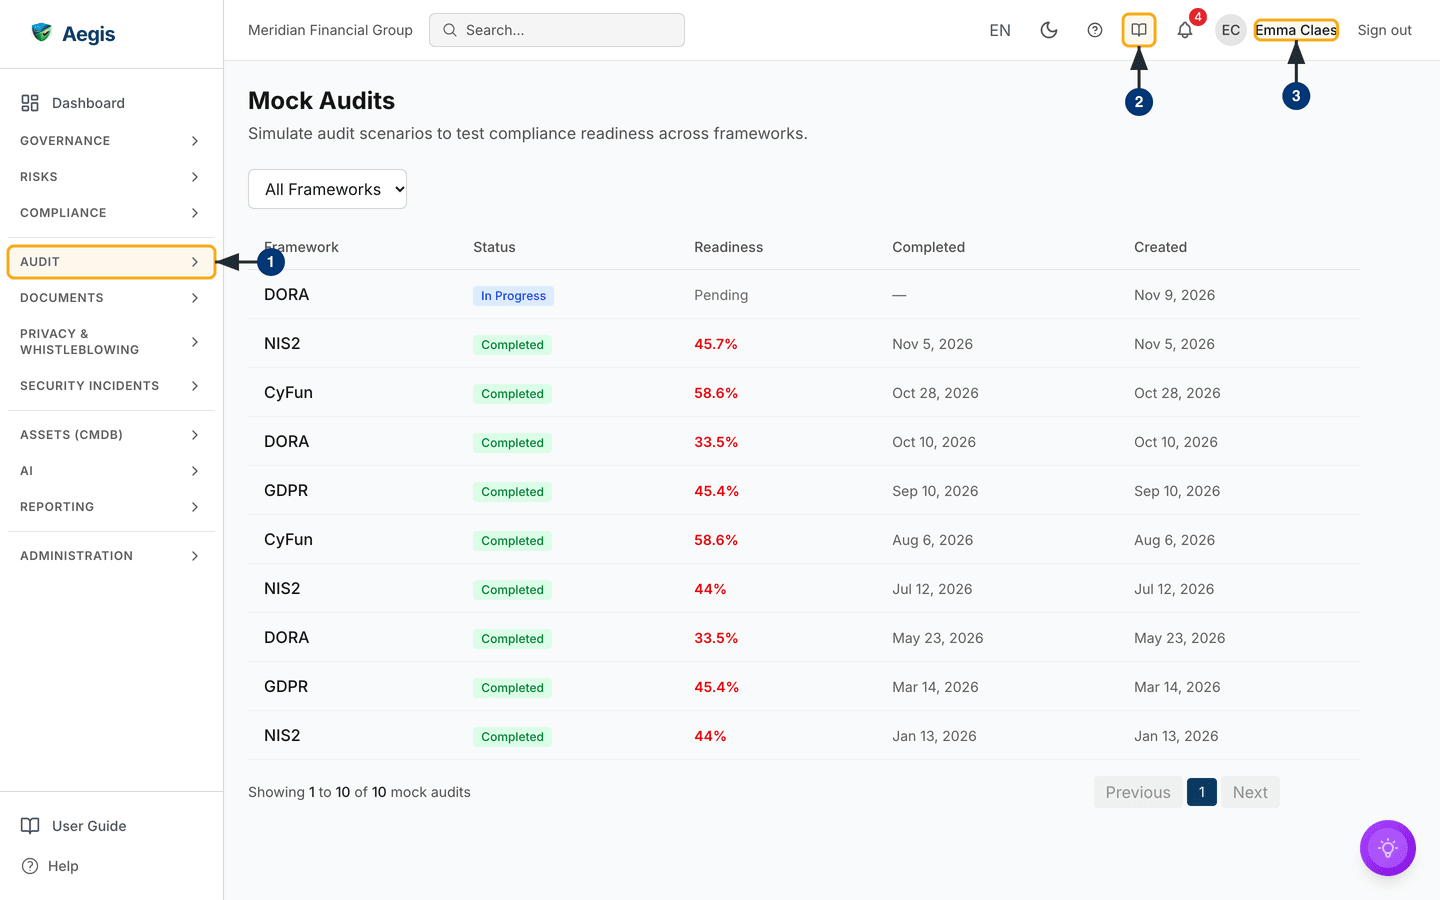
The All Frameworks dropdown above the table narrows the list to
NIS2, GDPR, CyFun, DORA or
NEN 7510. Selecting a row opens its detail dialog — status and
readiness badges over the report sections. Readiness shows green from 80%, amber
from 60% and red below that. The captured screen lists ten runs, newest first: a
DORA run still In Progress with a
Pending readiness and no completion date, then nine
Completed rehearsals of NIS2, CyFun, DORA and GDPR scoring between
33.5% and 58.6%, all in red.
Mock audits covers that dialog in full.
Tips and limits
- The two headline percentages measure different things. Overall Readiness is the weighted five-dimension score; Evidence Coverage Rate is covered controls over total controls. They diverge whenever policies, risks or vendors are in a different state from your evidence-backed controls — the reason the captured screen shows 63% beside 72%.
-
The same goes for each framework row:
Evidence Coveragecounts controls with approved evidence, while theReadinessbadge counts controls (or CyFun requirements) actually met. Expect the badge to sit lower. - The composite score and the trend come from stored snapshots, so they move after the daily job runs or a framework is switched on or off, not the moment you attach evidence. The framework table, its readiness badges and the two coverage cards are recalculated on each page load.
- Activating a framework adds all its controls to the denominator, and evidence past its validity date stops counting — so a score can fall with no one having touched anything, and the trend will show the dip. Renew expired items in Evidence.
- The table does not name the individual uncovered controls, and the recommendations name at most ten per row. For the full list, open the framework in Compliance frameworks and read its gaps there.
- Only frameworks Aegis carries and you have activated appear. SOC 2 is not among them today — it is a planned addition, not shipped, so no SOC 2 row can appear here. Activate what you have in Compliance frameworks.
- A readiness score is an internal preparation aid built from your own records — not an audit result, a certification, or a prediction of one, and the work it measures is never finished.
Where this connects
Readiness is assembled from Policies, Compliance frameworks, Evidence, Risks and Vendors, and every recommendation links back into one of them. The formal programme lives in Audits, saved triage plans surface in Action items, the headline level and its trend suit a board report, and Benchmarking sets the same score against your peers. For the whole journey through to an evidence pack in an auditor's hands, read the external-audit scenario.